New Android malware uses AI to steal bank logins and PINs
RatHat can navigate infected phones while stealing bank logins, authentication codes, and screen-lock PINs.
Ransomware campaigns, trojan analysis, botnet takedowns, infostealer tracking, and malware IOC reports from cybersecurity researchers worldwide.
RatHat can navigate infected phones while stealing bank logins, authentication codes, and screen-lock PINs.
Kaspersky experts have discovered a new MovieReaper campaign. The multi-stage Trojan spreads through movie torrents, such as "The Odyssey," and uses the Solana
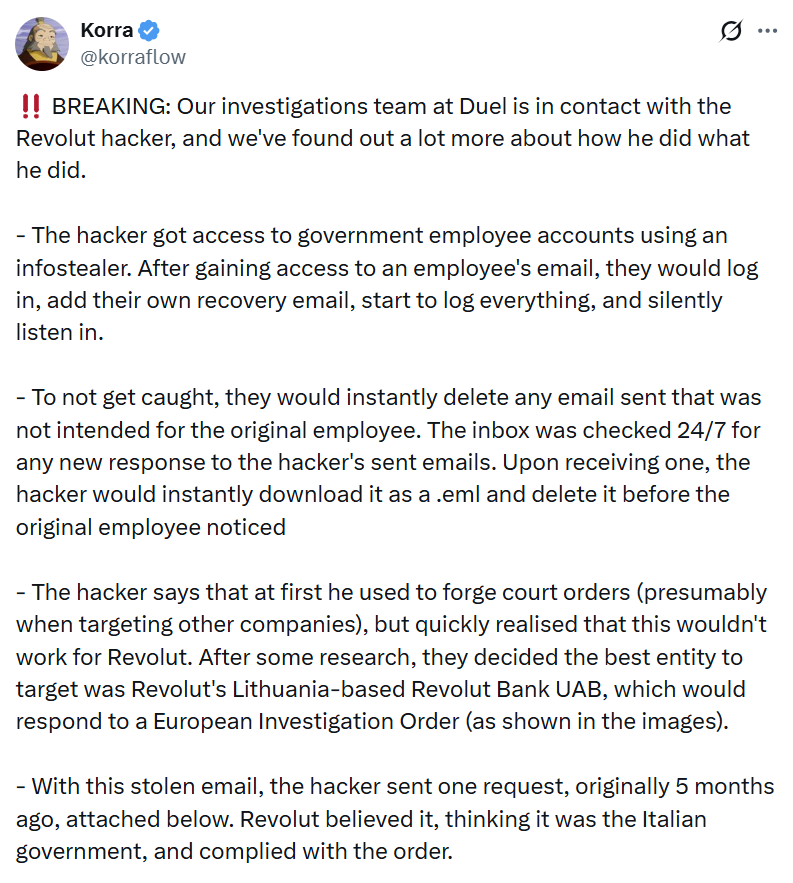
Revolut Hackers Exploited Infostealers for Social Engineering Revolut Hackers Used Infostealers for Elaborate Social Engineering BREAKING: The investigations te
Cybercriminals used HBO Max’s verified Reddit account to run 108 malicious ads that tricked people into installing information stealers.
The Gigabud banking Trojan can clone a banking app into a separate work profile on an Android device to help hide fraudulent transactions.
Oleksii Lytvynenko joined the notorious group in 2021 and was directly involved in attacks on at least 12 companies. The post Conti ransomware crew member sente
See how Microsoft Defender detects and disrupts AI-themed phishing, malware, and multi-stage attacks across the attack chain. The post Detect and disrupt AI-the
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Sep. 9, 2026 – Read the Full Story from J.S. Held Court-appointed receive
This week on the Lock and Code podcast, we speak with Kim Sutherland about loyalty points fraud and how everyday people can stay safe.
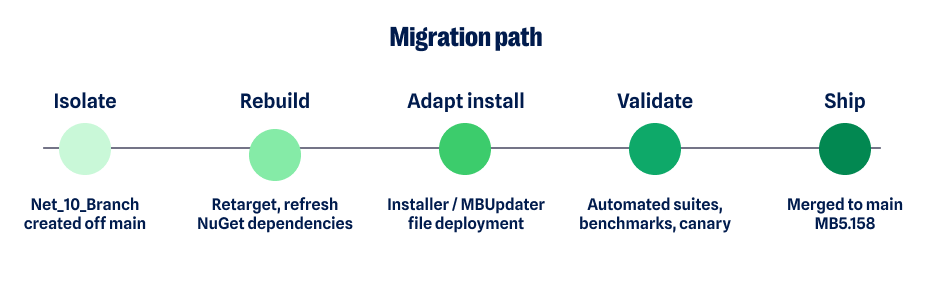
Why disciplined dependency modernization is one of the highest-leverage engineering investments a security product can make.
Kaspersky GERT experts have discovered new backdoors used by the Toy Ghouls group. One version of the backdoor uses the HiveMQ MQTT broker as its command-and-co
In Part 1 of this guide, we examined two common incident scenarios: cross-account Amazon Simple Storage Service (Amazon S3) data deletion with ransomware implic
Social media ads for a free streaming service exposed roughly 570,000 people to StreamRat, a banking Trojan that can take control of infected phones.
Sality’s peer-to-peer infrastructure allowed it to evade system-wide disruption efforts for an exceptionally long period. Authorities and cybersecurity experts
It’s the first Pegasus infection of 2026 that Citizen Lab is forensically confirming, and the SHARE Foundation said it’s the biggest wave of spyware surveillanc
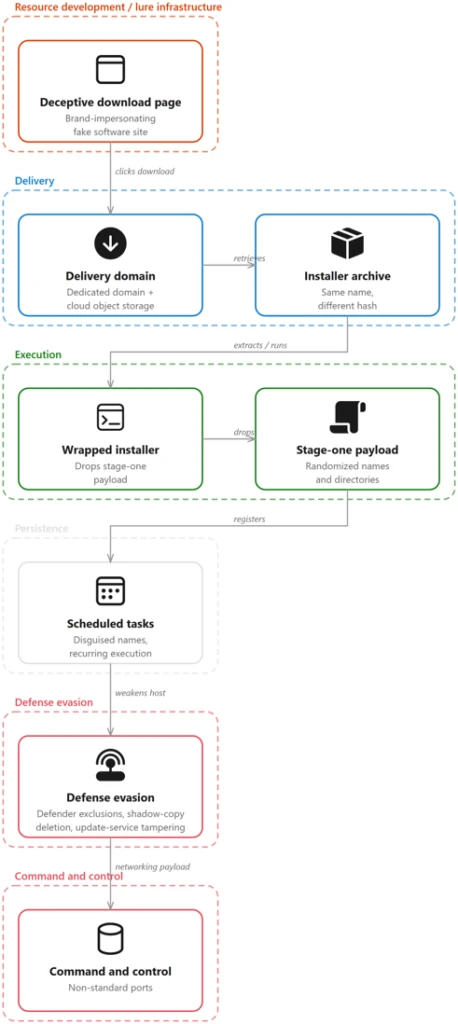
An active campaign is impersonating legitimate software vendors to deliver malware through look-alike download pages and regenerated installer archives. Microso
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
The major healthcare sector vendor did not identify the attackers, but ShinyHunters, a prolific group increasingly targeting the sector, claimed responsibility.
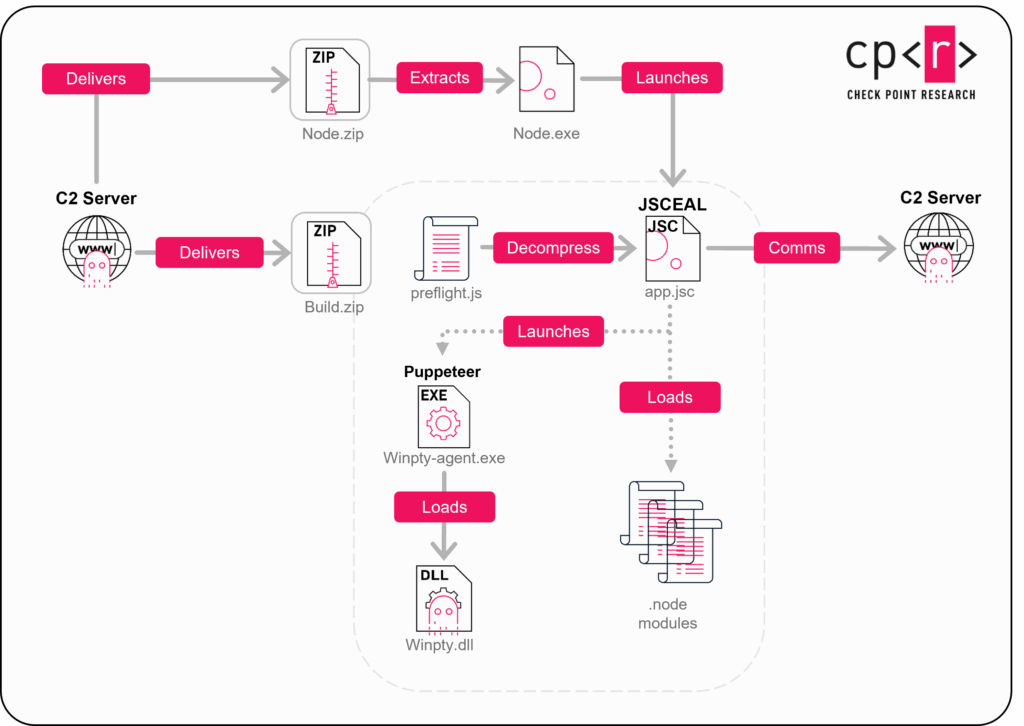
Research by: hasherezade Key Points Introduction JSCeal is a stealer delivered as compiled V8 bytecode (.jsc) and executed by a bundled Node.js runtime, ta
Threat actors are distributing the ValleyRAT backdoor disguised as adware. We analyze the infection chain, from the malicious installer to the final payload.
The CyberHawk platform goes far beyond news. Scan indicators, track active campaigns, monitor infostealer feeds, and access a complete analyst toolkit — all free to join.