Ransomware recovery CEO indicted after allegedly paying hackers and pocketing millions
Zohar Pinhasi allegedly deceived ransomware recovery clients into a payment scheme disguised as a specialized service that helped victims avoid paying cybercrim
Ransomware campaigns, trojan analysis, botnet takedowns, infostealer tracking, and malware IOC reports from cybersecurity researchers worldwide.
Zohar Pinhasi allegedly deceived ransomware recovery clients into a payment scheme disguised as a specialized service that helped victims avoid paying cybercrim
In this post, we analyze the evolution of CastleStealer, including the sensitive data it targets, new techniques for bypassing browser protections, remote comma
More than 3,400 servers have been compromised by malware that hides its infrastructure coordinates in a poem. The post PoeLLM malware has assembled a sweeping b
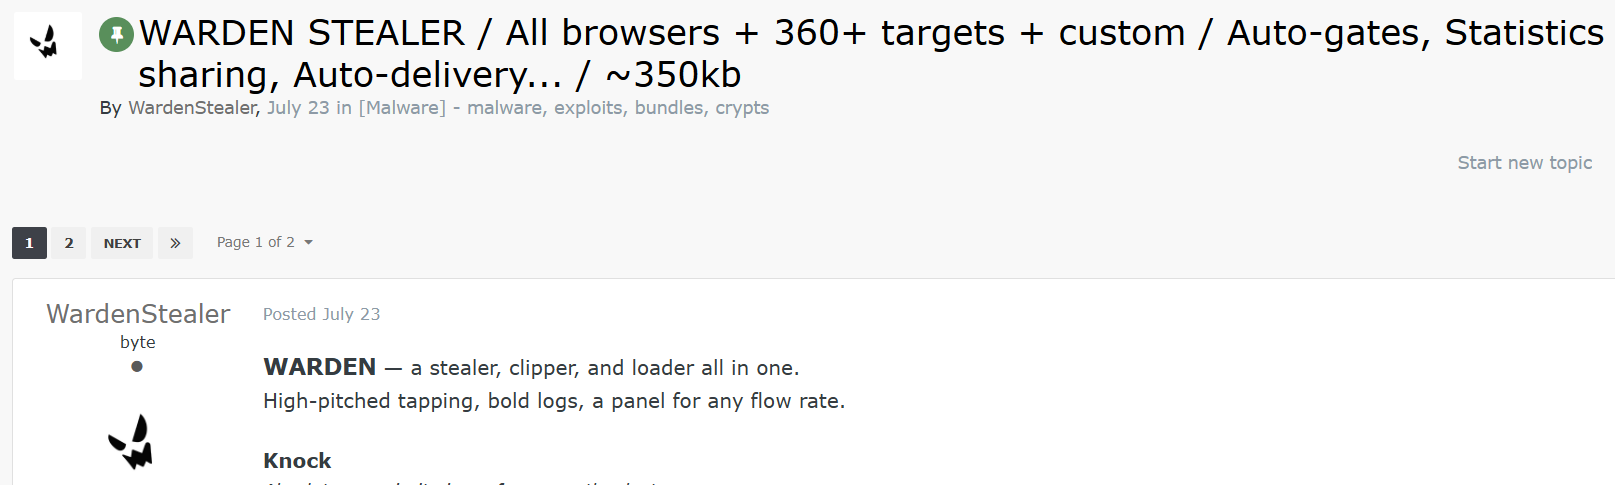
Infostealers Are Actively Hunting AI Agents and Developer Keys – Warden Infostealer Initial announcement and feature breakdown of Warden Stealer on the Ex
The FBI and Secret Service warned Fortinet users that FortiBleed, uncovered this summer, is a continuing threat. The post Alert: FortiBleed remains active campa
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Oct. 6, 2026 – Listen to the Podcast Episode A new study shows that
A list of topics we covered in the week of September 28 to October 4 of 2026
The teenager-run cybercrime group victimized roughly 500 organizations in less than two years. The post Authorities seize KillSec extortion group infrastructure
Flashpoint was awarded U.S. Patent No. 12,705,360 for its Ransomware Risk model, which rates how closely new vulnerabilities match those used in ransomware atta
Since January 2026, Microsoft has observed Russian state threat actor Star Blizzard evolve their detection evasion capabilities through large-scale phishing cam
Authorities in the Netherlands have arrested a 23-year-old convicted cybercriminal on suspicion of aiding in data thefts and extortions by the prolific hacker g
Microsoft Threat Intelligence identified NeedyMantis, a modular post-compromise malware framework used in targeted intrusions that combines custom loaders, encr
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Sep. 28, 2026 – Watch the YouTube Video With nearly $20 billion in estima
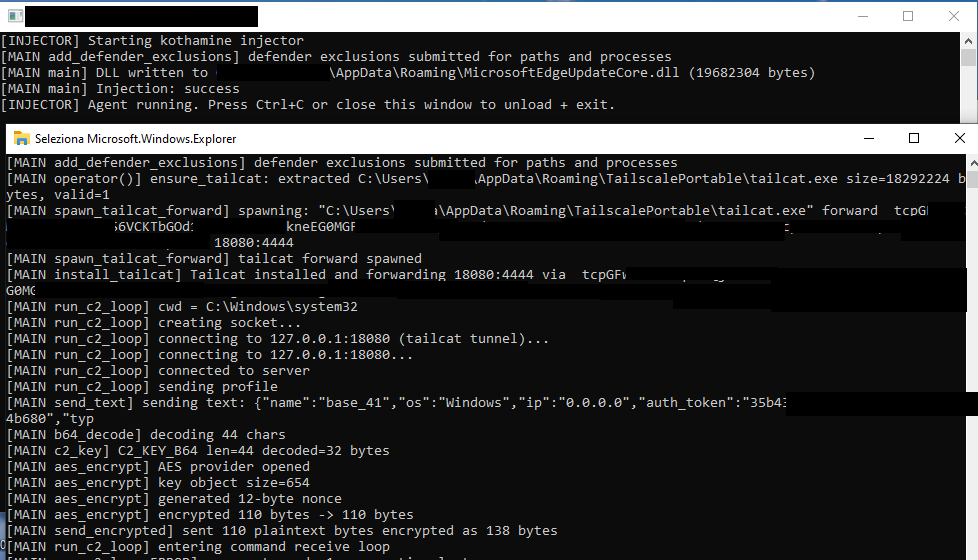
Kothamine uses a legitimate Tailscale tool to receive attackers’ commands through an encrypted connection with no malicious domain to block.
Storm-2570 is a ransomware affiliate that uses consistent post-compromise tools and techniques across deployments involving Qilin, DragonForce, Anubis, and BERT
This is an impressive piece of malware . Its sophistication says nation-state to me, but there is no direct evidence and certainly no attribution.
We look at a new version of the MacSync macOS stealer with a backdoor module that targets crypto enthusiasts and developers.
The Armenian national was extradited from Ukraine to the United States last year and pleaded guilty to cybercrimes in July. The post Ryuk ransomware operator se
SpyCloud’s study found 1,787 of the approximately 10,000 U.S. organizations had it, including one infected device that saved logins for 167 utility metering ten
Kaspersky GERT experts dive into the technical incident analysis of PAYLOAD ransomware: an encryptionless, binary-less operation that abused Active Directory me
The CyberHawk platform goes far beyond news. Scan indicators, track active campaigns, monitor infostealer feeds, and access a complete analyst toolkit — all free to join.