Apple notifications alert victims in 99 countries about mercenary spyware infections
The notifications come shortly before the Pall Mall Process is nearing final negotiations on guidelines for the use of commercial hacking tools. The post Apple
Ransomware campaigns, trojan analysis, botnet takedowns, infostealer tracking, and malware IOC reports from cybersecurity researchers worldwide.
The notifications come shortly before the Pall Mall Process is nearing final negotiations on guidelines for the use of commercial hacking tools. The post Apple
HUDSON ROCKINFOSTEALERS.COM · THREAT RESEARCH Developing investigation Polymarket / Third-party JavaScript Polymarket Breach Alert: Wallet-Draining Code Found i
The Russian-speaking cybercrime storefront was among the most active bulletproof hosting providers this year to date, receiving almost one-fifth of all illicit-
HR HUDSON ROCK / INFOSTEALERS.COM Threat Intelligence  •  October 28, 2026 Research / Cryptocurrency privacy 38,628 Crypto Orders. 10,139 IPs. What Wa
Artem Stryzhak participated in a series of ransomware attacks on hospitals, government entities and law firms from the middle of 2018 to late 2021. The post Pro
Flashpoint's new guide examines how modern ransomware attacks unfold, from initial access to recovery, and the intelligence security teams need to disrupt attac
Key Points Introduction Over the past two months, we have been tracking a campaign that abuses the popularity of AI tools such as ChatGPT and Claude to spread a
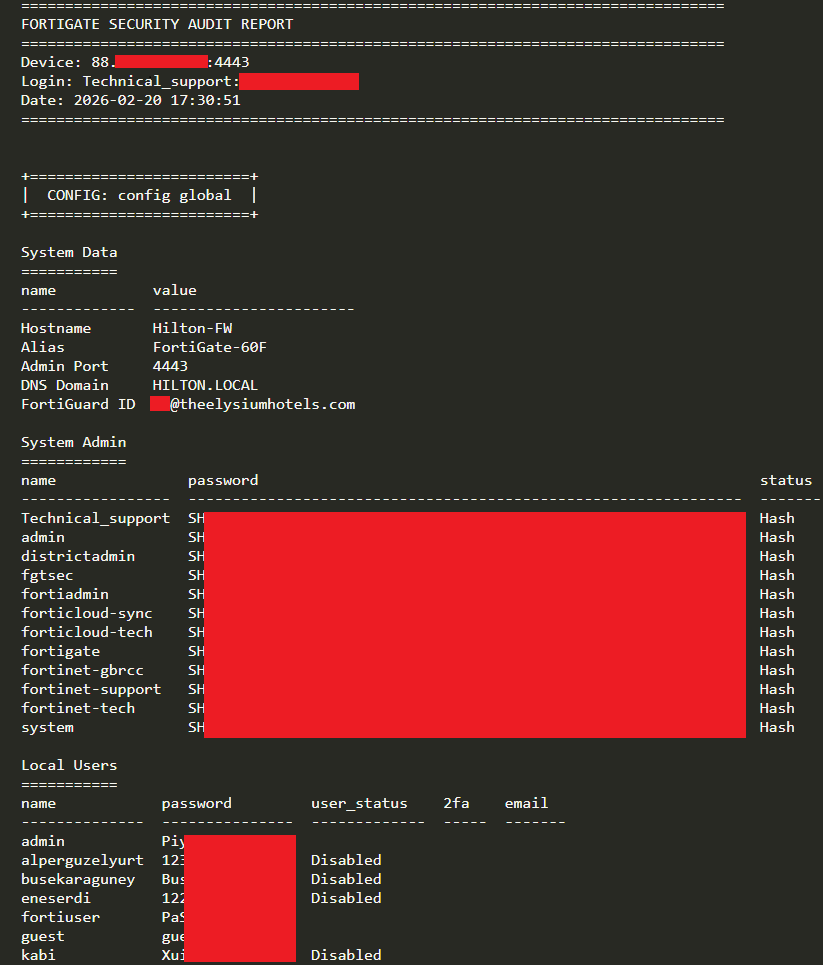
FortiBleed 2.0: 975 New Domains & 40,573 Exposed Secrets – Claim Your Ethical Disclosure | Hudson Rock Hudson Rock Threat Intelligence FortiBleed
A China-linked ransomware crew disabled the security tools at a critical infrastructure operator before it launched the encryptor. Most security budgets never p
For the latest discoveries in cyber research for the week of 26th October, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Japanese c
Key Points Introduction Infostealers commonly target browser passwords, session cookies, and cryptocurrency wallets. This malware combines those established cap
Kaspersky researchers analyze Operation FlashHole – a recent complex attack by Lazarus, involving a sophisticated malware set, watering-hole technique and abuse
The order cites national security concerns, including sending data to servers in China, the potential malware and the overall risk to federal IT systems. The po
Attackers tampered with AOMEI Backupper’s update system to deliver malware that could give them remote access to users’ PCs.
A researcher found serious flaws in Eiliko’s security, exposing private conversations and allowing remote changes to what the robot says.
Not sure if a link is safe? Malwarebytes Scam Link Check scans suspicious links for signs of phishing, scams, malware, and other online threats before you click
The 2026 Infostealer Index: A Comprehensive Vendor Ranking The 2026 Infostealer Index An independent, deep-dive analysis of Hudson Rock’s benchmark threat
Partnership Announcement October 14, 2026 · Cybercrime Intelligence Hudson Rock Partners with TRM Labs as a Launch Data Partner for Ardence, the New AI Inv
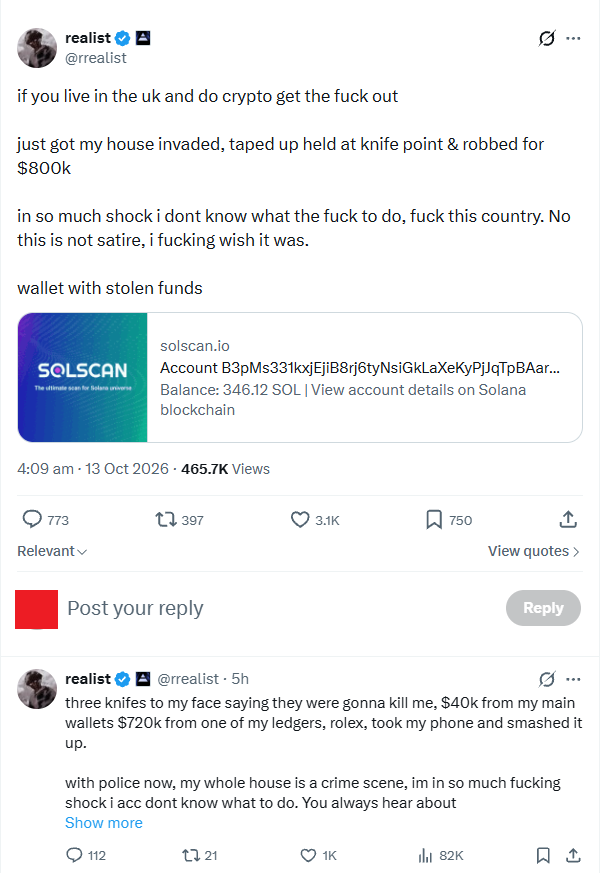
First Physical Robbery Potentially Linked to Revolut Hack First Physical Robbery Potentially Linked to Revolut Data Breach Following the recent Revolut hack we
Details of the case align with the investigation into ShinyHunters’ attack on FBI IT systems. The post Canadian cybersecurity executive arrested in federal exto
The CyberHawk platform goes far beyond news. Scan indicators, track active campaigns, monitor infostealer feeds, and access a complete analyst toolkit — all free to join.