What’s new in Microsoft Security: August 2026
This month’s updates provide new capabilities to help organizations gain insights into agent activity, expand security coverage across supported environments, a
In-depth threat intelligence and security research from Palo Alto Unit 42, Cisco Talos, Mandiant, Check Point, CrowdStrike, and other leading intelligence labs.
This month’s updates provide new capabilities to help organizations gain insights into agent activity, expand security coverage across supported environments, a
A monthly analysis of how artificial intelligence is used in illicit communities, based on Flashpoint proprietary intelligence and direct visibility into real t
OpenAI disrupted a social engineering group from Cambodia that used ChatGPT. Its scope is impressive: The network simultaneously conducted multiple types of sca
If you found time for a bit of vacation this summer, you might be in catch-up mode. Here’s a list to help: all the expert blog posts, new service capabilities,
The company says the breach stemmed from a systemic failure of alignment and security, and has taken measures to prevent agents from independently orchestrating
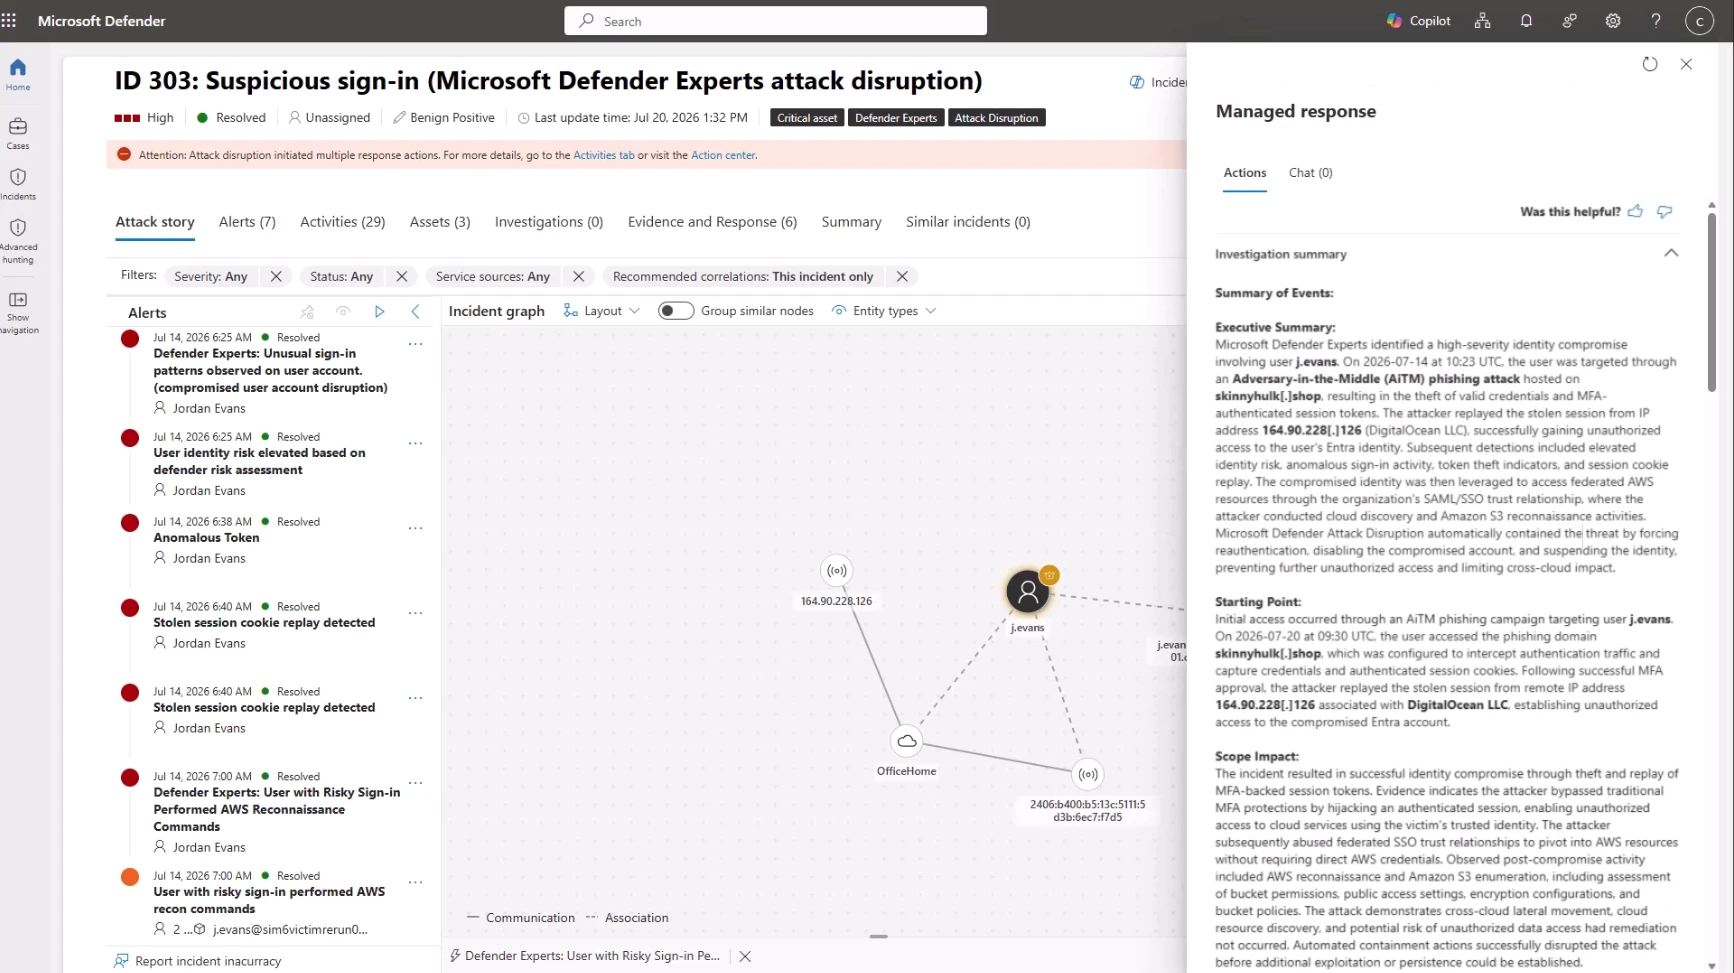
A single alert from one security service tells you something happened. Read that signal alongside activity from other services and your own business context, an
As part of Patch the Planet, we received preview access to GPT 5.6-Cyber with a simple task: evaluate its cyber capabilities. Recent events inspired me to give
This post announces the availability of a new independent assessment report available on AWS Artifact analyzing how Landing Zone Accelerator on AWS (LZA) can au
Organizations need protection that operates in the gap between discovery and remediation. The post The patch window is collapsing: Why security needs a new cont
We found and reported a bug in Provenance Blockchain, a public proof-of-stake chain built on Cosmos SDK, that lets any user grant themselves admin control over
Andy Ellis has a roundup of the security vendors at Black Hat this year. Key Takeaways: We have entered into an AI world. While nearly half of booths didn’
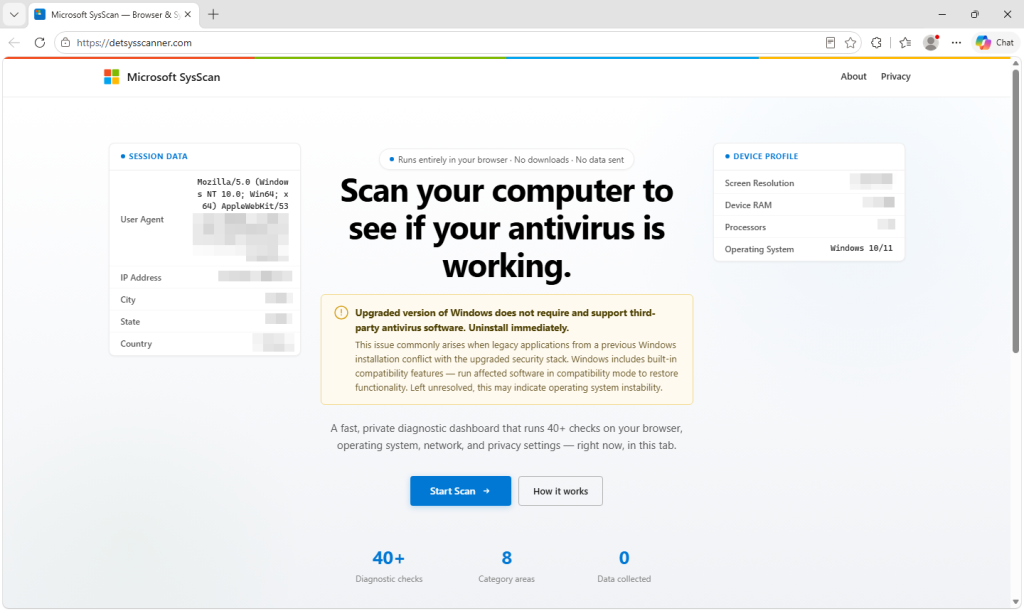
We found fake Microsoft-branded scanners that invent security problems, tell victims to uninstall AV, and then steer them into a refund scam.
For the latest discoveries in cyber research for the week of 24th August, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Latvia’s Ro
Interesting paper : Abstract: With entrepreneurial fraud cases on the rise, we investigate how entrepreneurs carry out criminal deception , employing deceptive
The neon flying squid can fly in formation. The shoal of about 100 squid rose unexpectedly from a patch of the Pacific Ocean around 370 miles from Tokyo and gli
The AI Security Institute has a new report of AI systems engaging in "unsanctioned behavior"—what I have been calling " genie behavior —while being
As firewall rule sets grow in complexity, security teams face a common challenge: manual log analysis is used to determine which rules are actively matching tra
OpenAI presented details of its AI’s model’s cyberattack on Hugging Face at Black Hat last week. Simon Willison details the timeline. It’s rea
Flashpoint’s monthly analysis of insider threat recruitment, illicit access advertising, and threat actor activity targeting enterprise environments. The post I
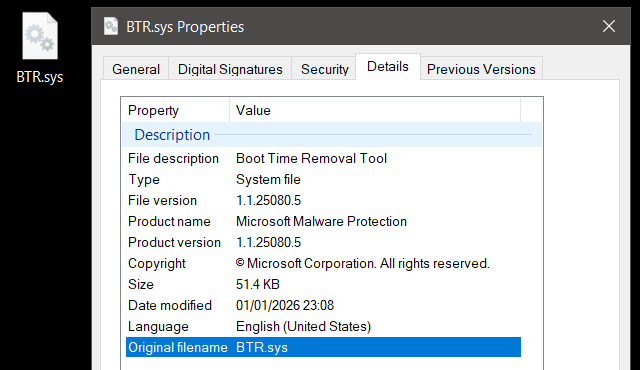
Research by: Jiří Vinopal (@vinopaljiri) Abstract What if a trusted security component could be repurposed into an attacker-controlled kernel primitive? What if
The CyberHawk platform goes far beyond news. Scan indicators, track active campaigns, monitor infostealer feeds, and access a complete analyst toolkit — all free to join.