How World ID wants to put a unique human identity on every AI agent
Iris scan-backed tokens could help stop agent swarms from overwhelming online systems.
Iris scan-backed tokens could help stop agent swarms from overwhelming online systems.
Internet-exposed devices that give BIOS-level access? What could possibly go wrong?
Account abstraction transforms fixed “private key can do anything” models into programmable systems that enable batching, recovery and spending limits, and flexible gas payment. But that programmabili
Questions remain as Google prepares to lock down Android app distribution in the name of security.
That guest network you set up for your neighbors may not be as secure as you think.
If you’ve ever done Linux memory forensics, you know the frustration: without debug symbols that match the exact kernel version, you’re stuck. These symbols aren’t typically installed on production sy
Before launching their Comet browser, Perplexity hired us to test the security of their AI-powered browsing features. Using adversarial testing guided by our TRAIL threat model, we demonstrated how fo
Two popular AES libraries, aes-js and pyaes, “helpfully” provide a default IV in their AES-CTR API, leading to a large number of key/IV reuse bugs. These bugs potentially affect thousands of downstrea
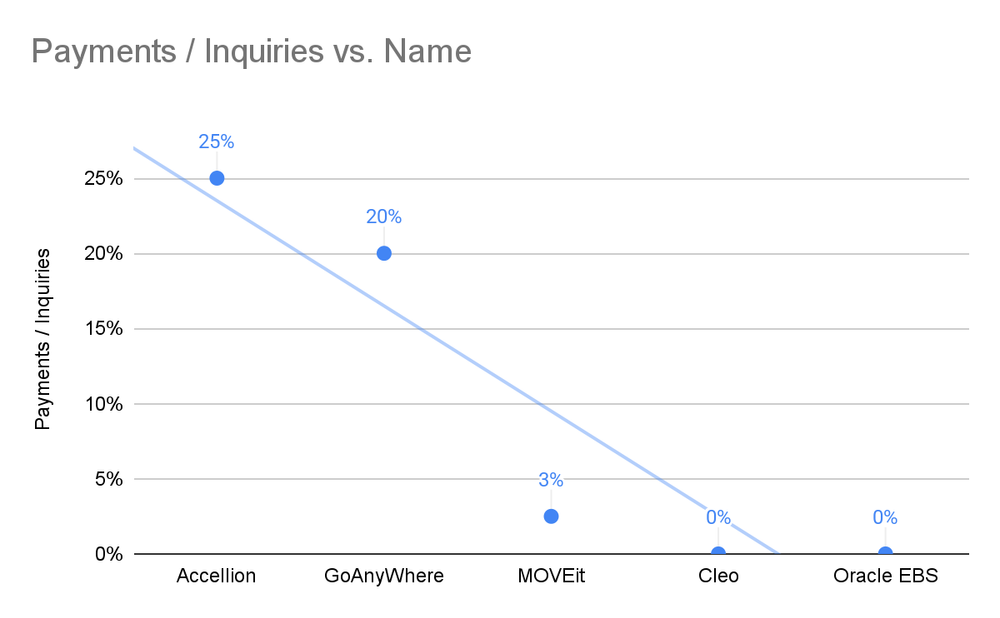
Are we seeing the extinction of mass data exfiltration campaigns? The stats demonstrate these attacks are losing their efficacy.
Nitrogen ransomware was derived from the previously leaked Conti 2 builder code, and is similar to Nitrogen ransomware, but a coding mistake in the ESXi malware causes it to encrypt all the files with
After reading recent reports of AI’s impact on cybercrime, one might assume that the world is about to enter an era of frightening, AI-powered ransomware attacks. As Trend Micro put it in its November
Between October and November 2025, one of the biggest cybercrime operations in Interpol history saw the arrest of 574 people suspected of business email compromise (BEC), digital extortion, and ransom
Last year, our engineers submitted over 375 pull requests that were merged into non–Trail of Bits repositories, touching more than 90 projects from cryptography libraries to the Rust compiler. This wo
Software signatures carry an invisible expiration date. The container image or firmware you sign today might be deployed for 20 years, but the cryptographic signature protecting it may become untrustw
Even well-known services with millions of users are exposing sensitive data.
Even Google's own earbuds are vulnerable to the Fast Pair hack.
Google says the reports lacked "helpful next steps."
Discover how Obscura ransomware corrupts encrypted files beyond recovery, and why technical validation is key to smart ransom response decisions
Cellebrite can apparently extract data from most Pixel phones, unless they're running GrapheneOS.
The percentage of companies choosing to pay ransoms dropped significantly, while threat actors shift their tactics in response to decreasing profits.