
VECT: Ransomware by design, Wiper by accident
Key Takeaways Background VECT Ransomware is a Ransomware-as-a-Service (RaaS) program that made its first appearance in December 2025 on a Russian-language cybercrime forum. After claiming their first
Key Takeaways Background VECT Ransomware is a Ransomware-as-a-Service (RaaS) program that made its first appearance in December 2025 on a Russian-language cybercrime forum. After claiming their first
For the latest discoveries in cyber research for the week of 27th April, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Vercel, a frontend cloud platform, has disclosed a s
We’re open-sourcing Trailmark, a library that parses source code into a queryable call graph of functions, classes, call relationships, and semantic metadata, then exposes that graph through a P
CTO says new AI model is "every bit as capable" as world's best security researchers.
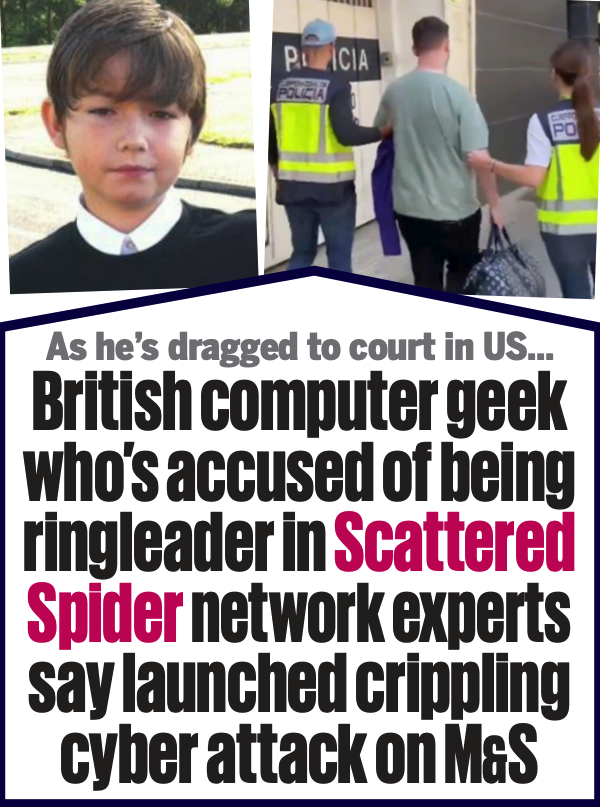
A 24-year-old British national and senior member of the cybercrime group "Scattered Spider" has pleaded guilty to wire fraud conspiracy and aggravated identity theft. Tyler Robert Buchanan admitted hi
For the latest discoveries in cyber research for the week of 20th April, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Booking.com, the Amsterdam-based travel platform, ha
Key Points The Gentlemen RaaS The Gentlemen ransomware‑as‑a‑service (RaaS) operation is a relatively new group that emerged around mid‑2025. The operators advertise their services across multiple unde
Two weeks ago, Google’s Quantum AI group published a zero-knowledge proof of a quantum circuit so optimized, they concluded that first-generation quantum computers will break elliptic curve cryptograp
Microsoft today pushed software updates to fix a staggering 167 security vulnerabilities in its Windows operating systems and related software, including a SharePoint Server zero-day and a publicly di
New model is the first AI system to complete a difficult multistep infiltration challenge.
For the latest discoveries in cyber research for the week of 13th April, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES The Los Angeles Police Department has reported a dat
We added a new chapter to our Testing Handbook: a comprehensive security checklist for C and C++ code. We’ve identified a broad range of common bug classes, known footguns, and API gotchas across C an
WhatsApp’s new “Private Inference” feature represents one of the most ambitious attempts to combine end-to-end encryption with AI-powered capabilities, such as message summarization. To make this poss
Mixed Boolean-Arithmetic (MBA) obfuscation disguises simple operations like x + y behind tangles of arithmetic and bitwise operators. Malware authors and software protectors rely on it because no stan
Code coverage is one of the most dangerous quality metrics in software testing. Many developers fail to realize that code coverage lies by omission: it measures execution, not verification. Test suite
This post is adapted from a talk I gave at [un]prompted, the AI security practitioner conference. Thanks to Gadi Evron for inviting me to speak. You can watch the recorded presentation below or downlo
After years of success, it looks as if the era where ransomware gangs could make easy money from data leak extortion might finally have ended. Despite its huge success, extortion-led ransomware is a s
We’re releasing a new Claude plugin for developing and auditing code that implements dimensional analysis, a technique we explored in our most recent blog post. Most LLM-based security skills ask the
Using dimensional analysis, you can categorically rule out a whole category of logic and arithmetic bugs that plague DeFi formulas. No code changes required, just better reasoning! One of the first le
DarkSword, a powerful iPhone-hacking technique, has been discovered in use by Russian hackers.