The State of Ransomware Q2 2026
For the past year, the ransomware conversation has centered on concentration: a handful of dominant RaaS operations controlling most of the damage, and a shrinking pool of active groups fighting over
For the past year, the ransomware conversation has centered on concentration: a handful of dominant RaaS operations controlling most of the damage, and a shrinking pool of active groups fighting over
Largest AI Supply Chain Breach of 2026: LiteLLM Hack Impacts Thousands of Global Enterprises – Claim Your Ethical Disclosure Largest AI Supply Chain Breach of 2026: LiteLLM Hack... The post Larg
A convincing fake CCleaner website delivers a multi-stage malware attack that installs a spyware extension inside Chrome.
The ransomware-as-a-service outfit has gone after a range of critical infrastructure sectors across the globe. The post U.S., South Korean government agencies caution to be on lookout for Gunra ransom
This week on the Lock and Code podcast, we speak with Chris Parr about his inventive and all-too-funny stress-test of surveillance pricing.
Microsoft Threat Intelligence examines DeadLock ransomware, an emerging financially motivated operation distinguished by its use of decentralized infrastructure to support victim communications, negot
The report presents key trends and statistics on malware that targeted personal computers running Windows and macOS, as well as internet of things (IoT) devices, during Q2 2026.
Maksim Silnikau participated in cybercrime since at least 2005. He ran Ransom Cartel from 2021 until his arrest in 2023. The post Ransom Cartel creator sentenced to 16 years in prison appeared first o
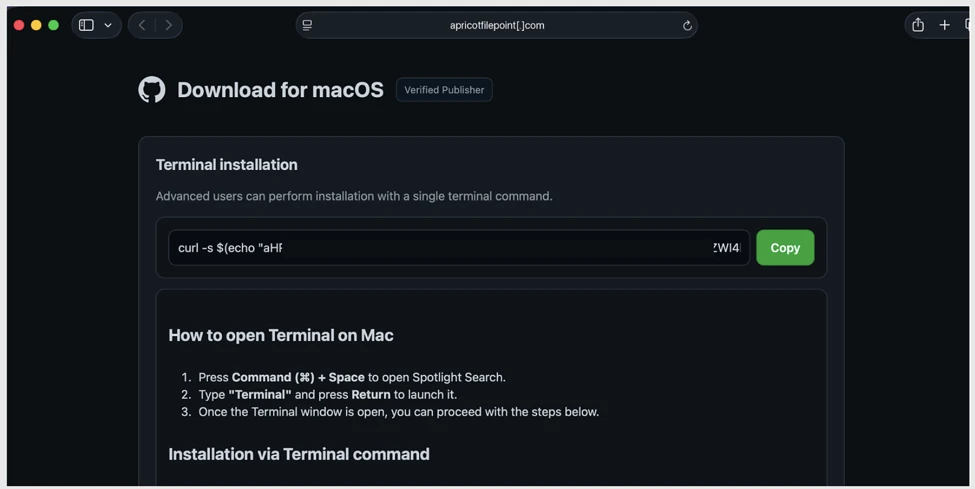
A macOS ClickFix campaign shifted tactics from openly serving infostealer lures to hiding them behind a browser-fingerprinting gate. The change makes malicious infrastructure harder to detect while gi
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Aug. 4, 2026 – Watch the YouTube short "ILOVEYOU", sometimes referred to as the Love Bug or Loveletter, was a com
Over time, passkeys are supposed to replace passwords. But what happens when malware steals the master key?
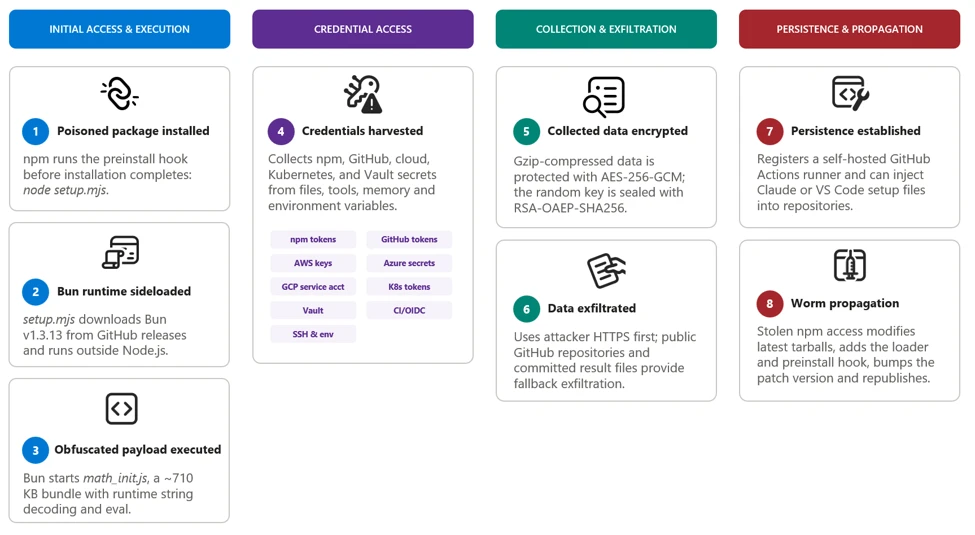
A credential-stealing worm hidden in more than 400 compromised npm packages automatically spread across software ecosystems by republishing malicious updates. This analysis details the attack chain, a
Researchers from multiple security firms observed a variant of Mini Shai-Hulud, self-replicating malware linked to TeamPCP, in all the affected packages. The post Massive supply-chain attack compromis
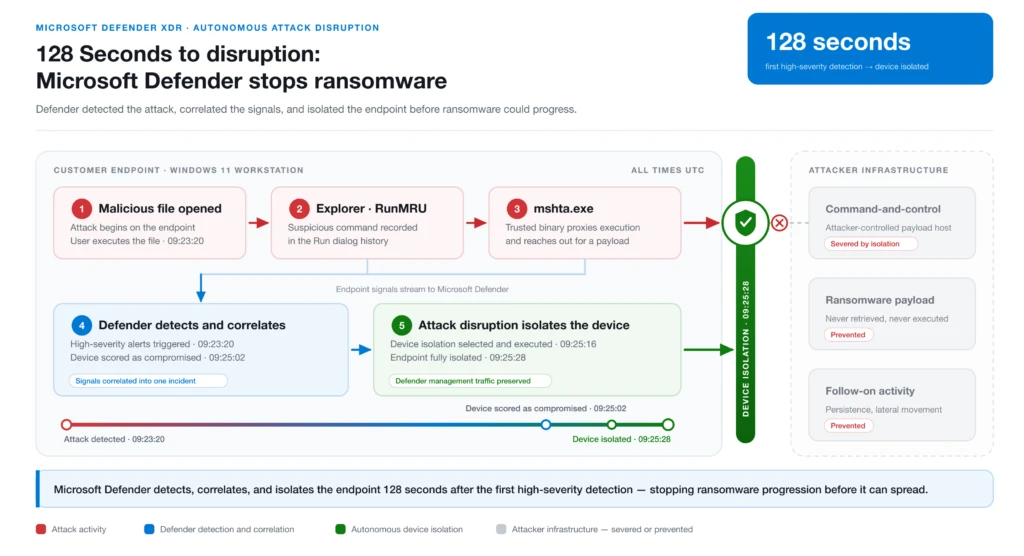
Microsoft Defender automatically isolated a compromised QNET endpoint in 128 seconds, stopping a multi-stage attack before the payload could persist or spread. The post 128 Seconds to disruption: Micr
INC ransomware wasn’t the first group to exploit the zero-days, but it’s been the most assertive and effective in chaining both vulnerabilities to steal and encrypt data for extortion. The post Prolif
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Aug. 4, 2026 – Listen to the podcast "This wasn’t someone behind the keyboard using AI as a tool to write m
We cover a cloud-based AitM attack scenario leveraging service workers and Ultraviolet, and provide detailed phishing hosting statistics across platforms like Cloudflare Workers, Vercel, Netlify, GitH
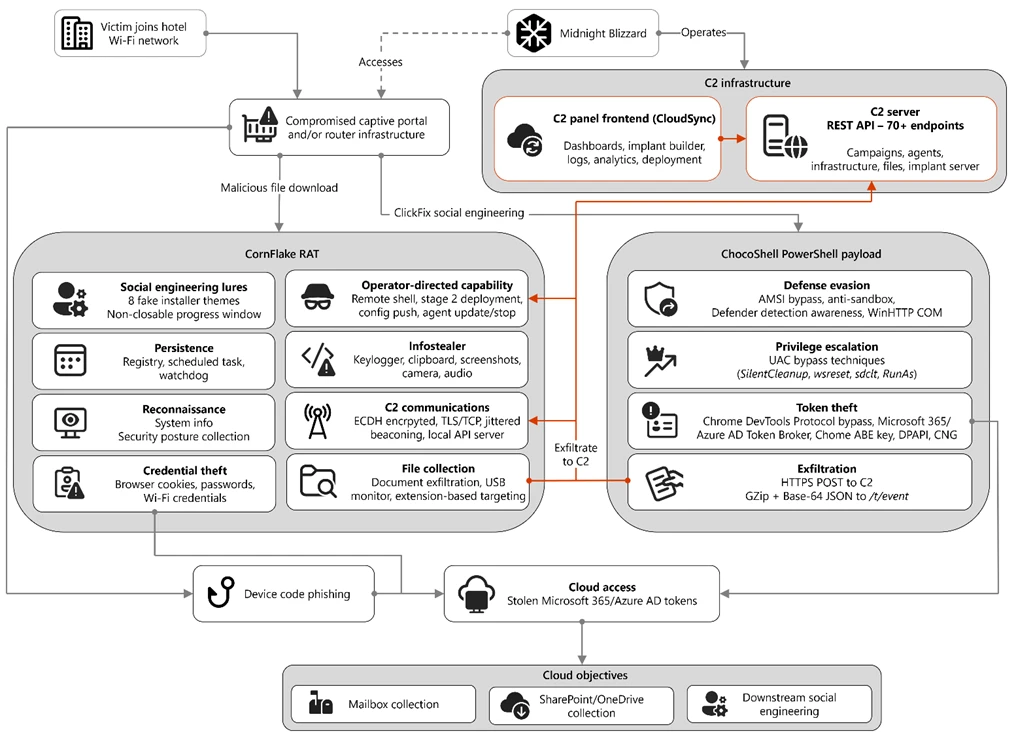
Storm-2945, a sub-cluster of the Russian threat actor Midnight Blizzard, has been observed compromising the sign-in portals of hospitality-related organizations such as hotels since May 2026 in order
Researchers have uncovered a new campaign that spreads the AtlasRAT remote access Trojan by disguising it as a Flash Player installer.
A new type of attack can trick Microsoft Copilot for Word into spreading hidden prompt injections from document to document.