Attackers exploited Citrix NetScaler zero-day for at least three weeks undetected
Mandiant researchers said dozens of organizations have been impacted by attacks attributed to advanced and suspected state-sponsored threat groups. They expect
Latest CVE disclosures, CVSS-scored vulnerabilities, and patch advisories from the NIST National Vulnerability Database and leading security researchers.
Mandiant researchers said dozens of organizations have been impacted by attacks attributed to advanced and suspected state-sponsored threat groups. They expect
As the leader in WordPress security, Wordfence provides unparalleled security coverage that fully encompasses protection, active monitoring, detection, and resp
In June 2026, the Wordfence Bug Bounty Program received 1066 vulnerability submissions from our growing community of security researchers working to improve the
Last week, there were disclosed in and that have been added to the Wordfence Intelligence Vulnerability Database, and there were that contributed to WordPress S
The white paper is the latest step in trying to create a “Quality Era” for the Common Vulnerabilities and Exposures (CVE) program as the number of CVEs surges.
WordPress has released security updates for a critical unauthenticated path traversal vulnerability that can lead to local PHP file inclusion and, on affected s
The Wordfence Threat Intelligence Team identified an interesting malware sample in mid June during a site clean. TThe malware was installed as a must-use plugin
A simple terminal command can hijack Muse and use its extensive permissions to spy on Mac users and control their connected accounts.
Wordfence Argus found a critical CVSS 9.8 vulnerability in libheif, a library many servers use to process HEIC images. We demonstrated protected-file disclosure
The latest zero-day has a maximum-severity rating and affects Cisco Identity Services Engine, a product hit with three actively exploited vulnerabilities since
Wordfence Argus discovered a PHP Object Injection vulnerability in Tutor LMS, affecting more than 100,000 WordPress sites. Subscriber-level attackers could achi
Last week, there were disclosed in that have been added to the Wordfence Intelligence Vulnerability Database, and there were that contributed to WordPress Secur
Google’s September Pixel update fixes 110 vulnerabilities, including a modem flaw being used in limited, targeted attacks.
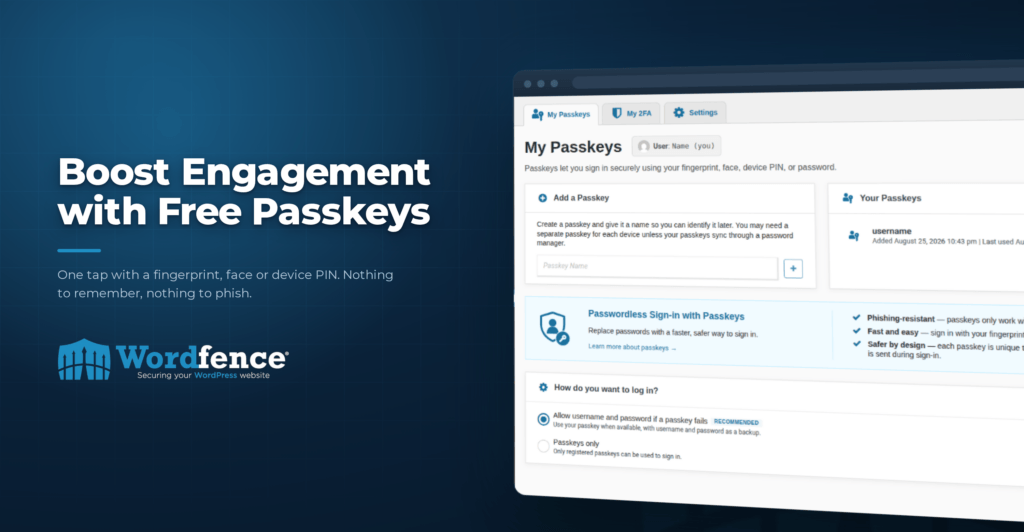
Wordfence 9 introduces passkeys, and passkeys provide a huge friction reduction because your user no longer has to remember their password or retrieve it from a
The company confirmed the defect was exploited before it was disclosed and patched, but it did not describe the nature of the attacks or the scope of impact acr
On February 20th, 2026, a critical Unauthenticated Arbitrary File Upload vulnerability was publicly disclosed in WooCommerce Wholesale Lead Capture, a premium W
On August 21 and August 22, 2026, Wordfence Argus, created by the Wordfence Threat Intelligence team, identified two independent critical vulnerability chains i
In May 2026, the Wordfence Bug Bounty Program received 1095 vulnerability submissions from our growing community of security researchers working to improve the
Once a month, Microsoft pushes a security update to all Windows users. Tomorrow’s is a new record : Microsoft’s patch for September is a doozy, with
Last week, there were disclosed in and that have been added to the Wordfence Intelligence Vulnerability Database, and there were that contributed to WordPress S
The CyberHawk platform goes far beyond news. Scan indicators, track active campaigns, monitor infostealer feeds, and access a complete analyst toolkit — all free to join.