Is this link safe? Find out with Malwarebytes Scam Link Check
Not sure if a link is safe? Malwarebytes Scam Link Check scans suspicious links for signs of phishing, scams, malware, and other online threats before you click.
Not sure if a link is safe? Malwarebytes Scam Link Check scans suspicious links for signs of phishing, scams, malware, and other online threats before you click.
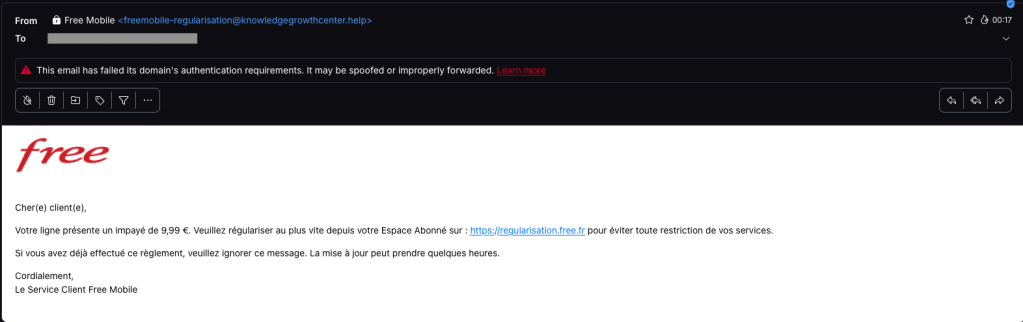
Free Mobile customers received very convincing phishing emails after major data breach.
Free Mobile customers received very convincing phishing emails after major data breach.
Earlier this month, Anthropic published a long report detailing all of the Claude misuses it detected. Daniel Meissler usefully summarized the report into 117 findings. A few of the highlights: AI age
Revolut customers received phishing texts only days after the digital bank acknowledged disclosing customer data to a government impostor.
A large phishing campaign is using fake T-Mobile rewards points and looming expiry dates to pressure recipients into clicking malicious links.
The ongoing social engineering threat, which dates back to late 2025, tricks victims into granting threat actors long-term access to their accounts. The post FBI raises alarm over deceptive phishing c
Leaked personal and financial data of around 750,000 US citizens, including SSNs and bank details, could put victims at risk of identity theft and phishing.
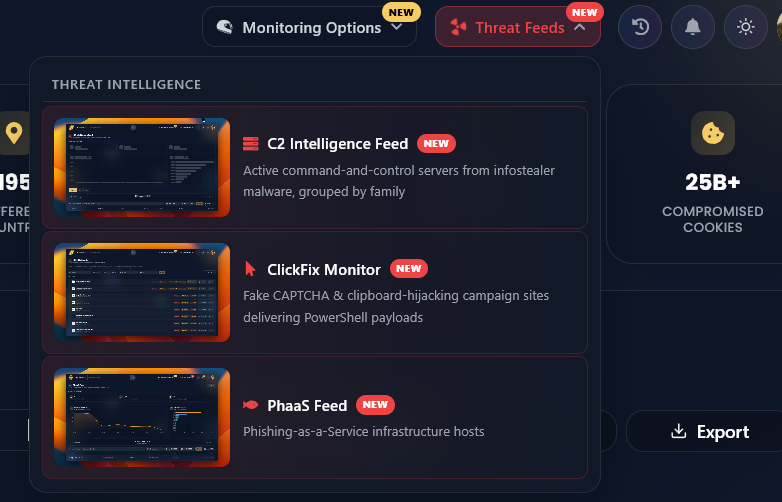
Introducing Cavalier’s New Threat Feeds: Comprehensive Visibility into Attacker Infrastructure We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and Phaa
Introducing Cavalier’s New Threat Feeds: Deep Dive into Phishing-as-a-Service (PhaaS) Intelligence We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and
Introducing Cavalier’s New Threat Feeds: Deep Dive into ClickFix Monitoring We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and PhaaS (Phishing-as-a-se
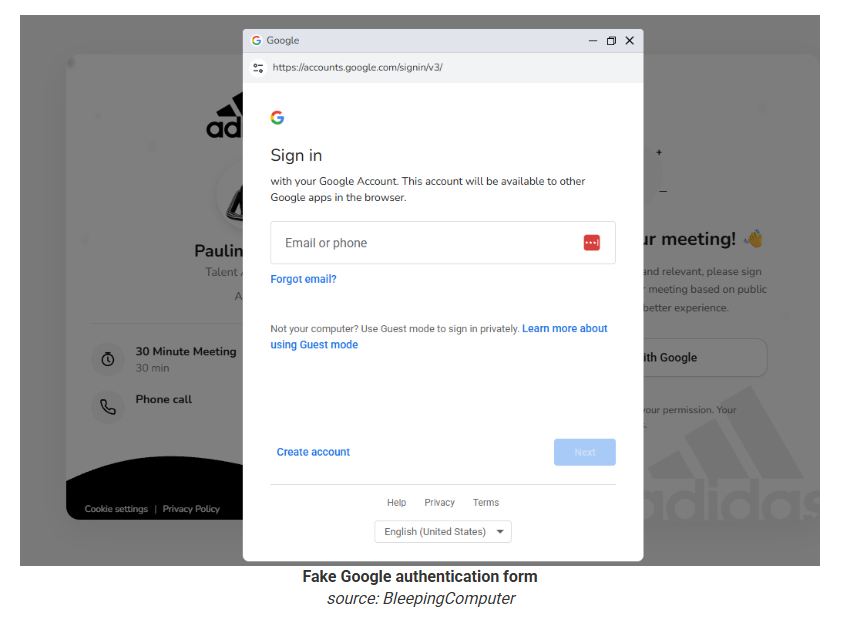
A fake recruiter phishing campaign uses trusted brands, nested redirects, and fake Google prompts to steal accounts.
A phishing campaign installs a malicious Chrome extension to hijack browser sessions and compromise Windows devices.
Malwarebytes got top marks in independent tests against malware, phishing, and other online threats.
We found EtherRAT malware being distributed by a website with a strange homepage. Following the trail, we discovered a vast network of malicious infrastructures, distributing malware, malicious docume
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – May. 28, 2026 – Read the full story in Daily Mirror Hilmy Cader warns that the intensity and sophistica
Executive Summary Cyble Research and Intelligence Labs (CRIL) has identified a novel Android banking trojan, dubbed OverlayPhantom, actively distributed in the wild via malicious URLs. The malware emp
The modern enterprise is no longer breached in the traditional sense. Firewalls remain intact; endpoints appear compliant, and credentials are often never “stolen” in the usual way. Yet attackers stil