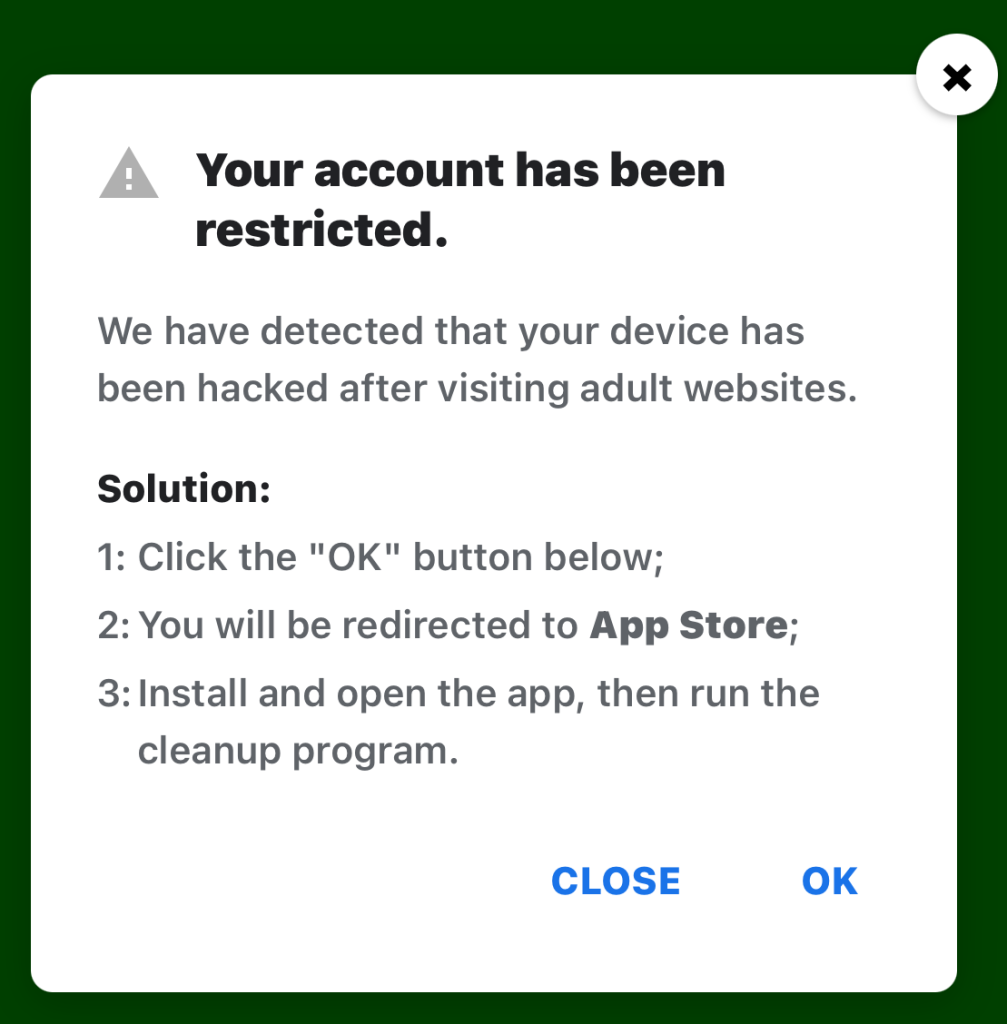
Fake virus alerts are invading mobile games
"Your device is infected!" Fake account warnings and virus alerts are turning some in-game ads into malware traps.
"Your device is infected!" Fake account warnings and virus alerts are turning some in-game ads into malware traps.
The escalated threat posed by the defect showcases how quickly a seemingly mild vulnerability can turn into an urgent warning. The post Attackers are exploiting Palo Alto Networks defect that initiall
New article: " Responsible Disclosure in the Age of AI: A Call for Urgent Action ," by Melissa Hathaway. Abstract: Artificial intelligence is fundamentally reshaping the balance between vulnerability
On May 4th, 2026, we received a submission for an Unauthenticated Privilege Escalation vulnerability in the Kirki WordPress plugin. Although the plugin has more than 500,000 active installations, we e
A fake BlueWallet download tricks Mac users into running malware that steals passwords, crypto wallets, and clipboard data.
In March 2026, the Wordfence Bug Bounty Program received 1718 vulnerability submissions from our growing community of security researchers working to improve the overall security posture of the WordPr
On March 24th, 2026, we received a submission for an Unauthenticated Administrator Account Creation vulnerability in WP Maps Pro, a WordPress plugin with more than 15,000 sales. This vulnerability mak
Last week, there were disclosed in and that have been added to the Wordfence Intelligence Vulnerability Database, and there were that contributed to WordPress Security last week. Review those vulnerab
Searching for ChatGPT? This fake download site serves malware to both Windows and Mac users, using separate payloads tailored to each platform.
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – May. 27, 2026 –Read the full story Immense stress has infected the brains of CISOs (chief information security of
Last week, there were disclosed in and that have been added to the Wordfence Intelligence Vulnerability Database, and there were that contributed to WordPress Security last week. Review those vulnerab
Executive Summary Cyble Research & Intelligence Labs (CRIL) has identified an active FreePBX exploitation campaign, with high confidence tied to INJ3CTOR3, an actor with a documented history of target
A forensic breakdown of how an attacker turned CyberPanel's SnappyMail logging into a persistent webshell that survived every WordPress cleanup attempt. The post How a Webmail Log File Became a Root-L
The report presents key trends and statistics on malware that targeted personal computers running Windows and macOS, as well as Internet of Things (IoT) devices, during Q1 2026.
Kaspersky researchers analyze a range of new PebbleDash-based tools used in recent Kimsuky campaigns and reveal their connection to the AppleSeed malware cluster.
Executive Summary Cyble Research and Intelligence Labs (CRIL) has uncovered a targeted cyberespionage campaign leveraging social engineering and trusted infrastructure to establish persistent, covert
WhatsApp’s new “Private Inference” feature represents one of the most ambitious attempts to combine end-to-end encryption with AI-powered capabilities, such as message summarization. To make this poss
Code coverage is one of the most dangerous quality metrics in software testing. Many developers fail to realize that code coverage lies by omission: it measures execution, not verification. Test suite
We’re releasing a new Claude plugin for developing and auditing code that implements dimensional analysis, a technique we explored in our most recent blog post. Most LLM-based security skills ask the
Account abstraction transforms fixed “private key can do anything” models into programmable systems that enable batching, recovery and spending limits, and flexible gas payment. But that programmabili