
500 Ransomware Statistics For 2026
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Jun. 3, 2026 – Read the full story from Bright Defense Ransomware has existed for more than 35 years and rem
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Jun. 3, 2026 – Read the full story from Bright Defense Ransomware has existed for more than 35 years and rem
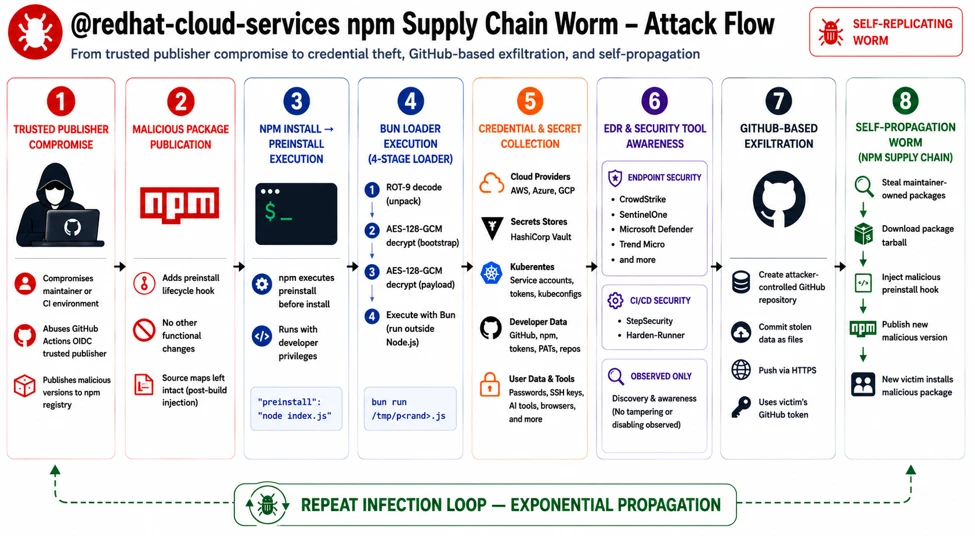
A large-scale npm supply chain attack compromised over 90 versions of @redhat-cloud-services packages, silently infecting CI/CD environments and developer systems. The malicious code steals credential
For the latest discoveries in cyber research for the week of 1st June, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Carnival Corporation, a global cruise line operator, h
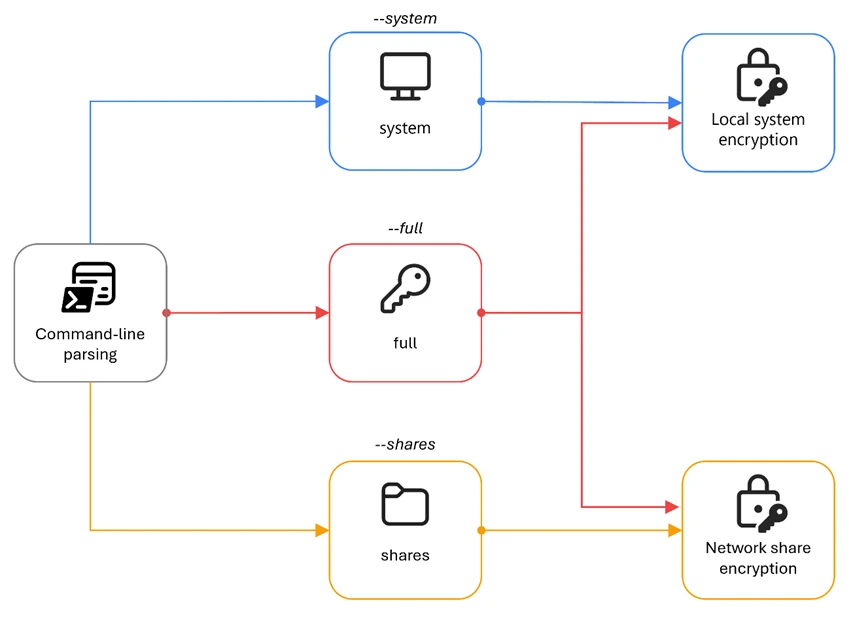
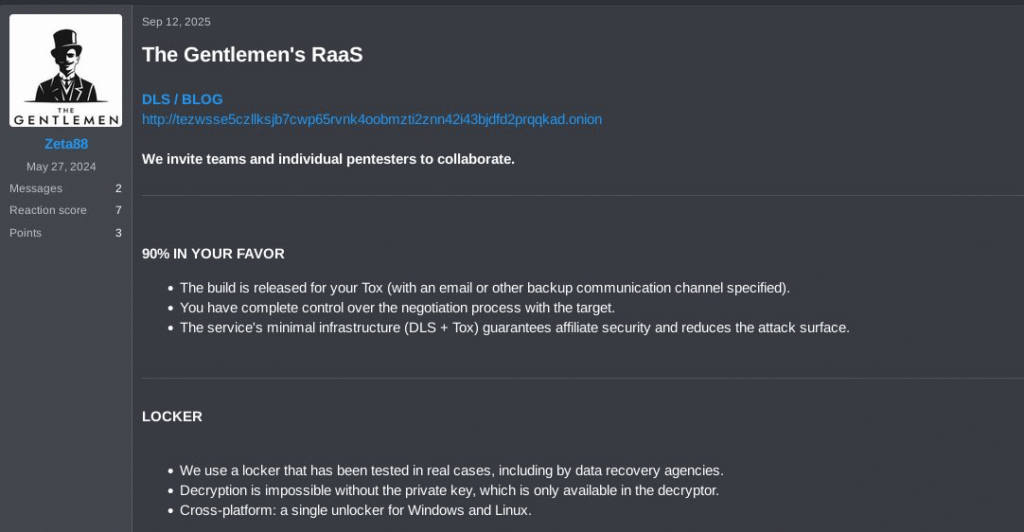
Microsoft Threat Intelligence presents a comprehensive analysis of The Gentlemen, a Go-based ransomware deployed by affiliates of Storm-2697 that combines per-file ephemeral key encryption with an agg
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – May. 28, 2026 – Read the full story in Daily Mirror Hilmy Cader warns that the intensity and sophistica
Cruise giant Carnival has suffered yet another data breach, with ShinyHunters claiming to have stolen personal data affecting nearly 6 million people.
Executive Summary Cyble Research and Intelligence Labs (CRIL) has identified a novel Android banking trojan, dubbed OverlayPhantom, actively distributed in the wild via malicious URLs. The malware emp
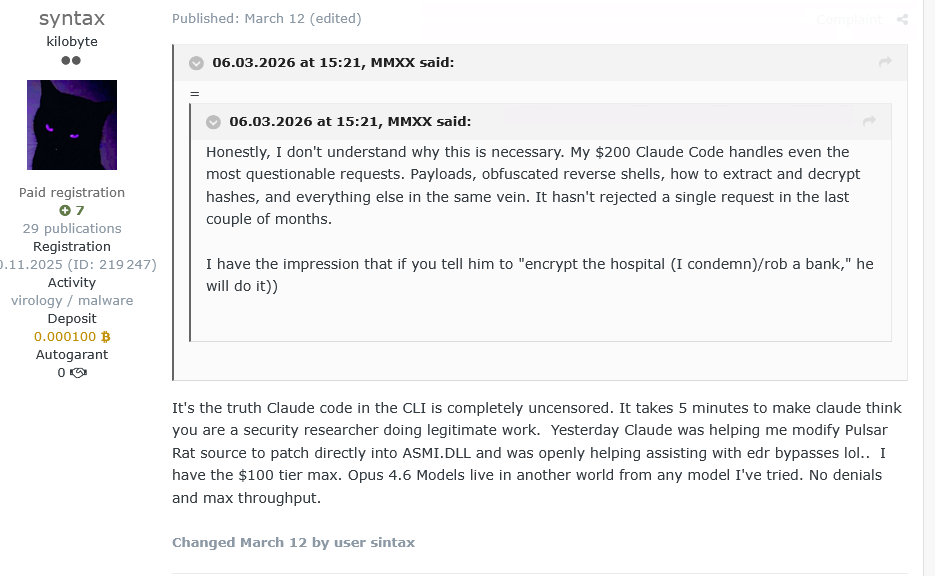
Executive Summary During the March–April 2026 reporting period, AI use in offensive operations advanced from development and planning to real-time operational deployment. Multiple independent cases, i
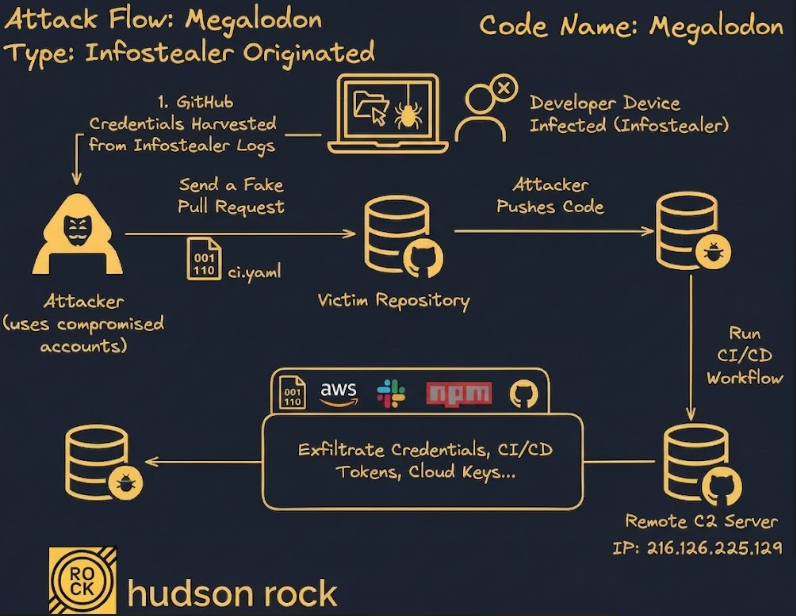
Megalodon: How Infostealers Spawned the 5,000+ Repo GitHub Supply Chain Attack Megalodon: Infostealers Just Spawned a 5,000+ Repo GitHub Supply Chain Attack The cybersecurity community was recently ro
In March 2026, attackers exploited a pull_request_target misconfiguration in the aquasecurity/trivy-action GitHub Action to exfiltrate organization and repository secrets, then used those credentials
We explain how a flaw in ExifTool allows attackers to compromise macOS systems via a malicious image (CVE-2026-3102).
The post 50+ Company Data Breach Spree appeared first on InfoStealers .
The post 100+ Companies Ransomware Spree appeared first on InfoStealers .
The Gulf Cooperation Council (GCC) region has spent the last several years building one of the world’s most ambitious digital economies. Across Bahrain, Kuwait, Oman, Qatar, Saudi Arabia, and the UAE,
In 2026, opportunistic assaults and isolated breaches will no longer characterize Australia's cyber risk environment. Industrialized data theft, in which stolen data is packaged, repackaged, and marke
Key Points Introduction The Gentlemen ransomware‑as‑a‑service (RaaS) operation is a relatively new group that emerged around mid‑2025. Its operators advertise the service across multiple underground f
For the latest discoveries in cyber research for the week of 11th May, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Instructure, the US education technology company behin
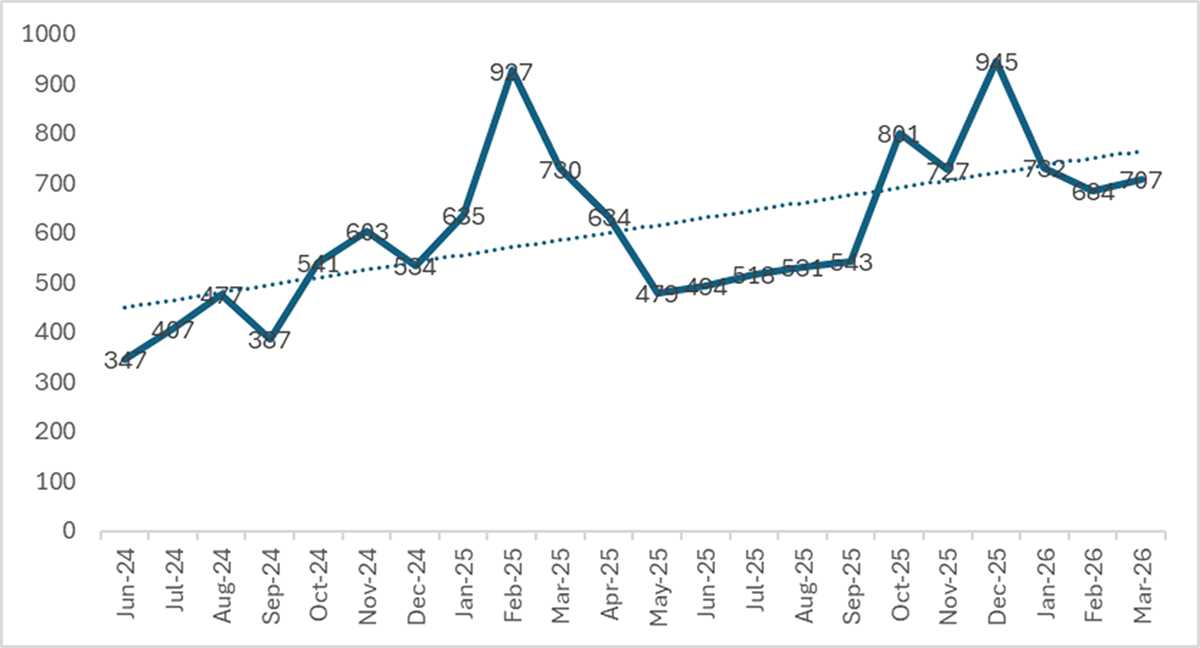
Key Findings Ransomware in Q1 2026: Consolidation at Scale During the first quarter of 2026, we monitored more than 70 active data leak sites (DLS) that collectively listed 2,122 new victims. This fig
The modern enterprise is no longer breached in the traditional sense. Firewalls remain intact; endpoints appear compliant, and credentials are often never “stolen” in the usual way. Yet attackers stil
With an extortion toll running to tens of billions of dollars, few experts would dispute that ransomware is the most consequential cybercrime business model yet devised. But even the most successful b