How to use GitHub safely
Knowing how to spot a malicious GitHub repository can help you avoid downloading malware disguised as legitimate software.
Knowing how to spot a malicious GitHub repository can help you avoid downloading malware disguised as legitimate software.
Last week, there were disclosed in and that have been added to the Wordfence Intelligence Vulnerability Database, and there were that contributed to WordPress Security last week. Review those vulnerab
Researchers said the vulnerabilities, which attackers are chaining together, were first exploited three weeks before the vendor disclosed and patched the defects. The post SonicWall customers under th
The ClaudeBleed vulnerability still lets malicious Chrome extensions abuse Claude for Chrome's permissions.
The company forewarned customers and defenders that a flood of defects would be uncovered by AI. It delivered with a striking exponential increase. The post Microsoft discloses ‘the mother of all’ vul
Microsoft Corp. today released software updates to plug at least 570 security holes in its Windows operating systems and other software, almost triple the number of vulnerabilities the software giant
The designations hit 1VPNS, its alleged Ukrainian administrator and a Belarusian who allegedly sold “cryptors” to disguise ransomware and other malware. The post Treasury sanctions First VPN Service,
FIFA’s network was vulnerable to anyone with even minimal access.
Instead of helping victims negotiate with BlackCat, a trusted ransomware negotiator secretly helped the gang extort them.
For the latest discoveries in cyber research for the week of 13th July, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES U.S. auto insurer AssuranceAmerica has disclosed a da
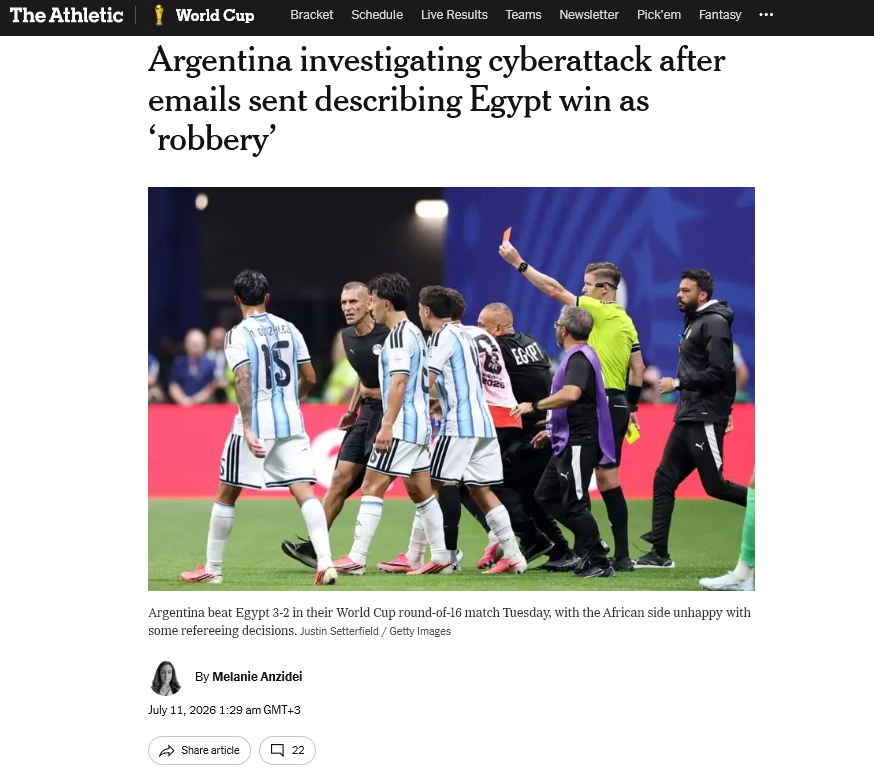
Infostealer Malware Triggers Major Database Breach at the Argentine Football Association Infostealer Malware Triggers Major Database Breach at the Argentine Football Association When the Argentine Foo
In a rare combined cybersecurity/squid post, a twenty-nine-year-old squid proxy bug can leak HTTP requests. As usual, you can also use this squid post to talk about the security stories in the news th
Karen Vardanyan faces up to 15 years in federal prison and agreed to pay nearly $1.2 million in restitution. The post Armenian national pleads guilty to Ryuk ransomware attacks appeared first on Cyber
GigaWiper is a remote access Trojan that can spy on victims and permanently wipe their systems in three different ways.
Angelo Martino exploited his insider position and fed confidential information to ransomware co-conspirators to extort a combined $75.3 million from five U.S.-based victims. The post Former DigitalMin
Last week, there were disclosed in and that have been added to the Wordfence Intelligence Vulnerability Database, and there were that contributed to WordPress Security last week. Review those vulnerab
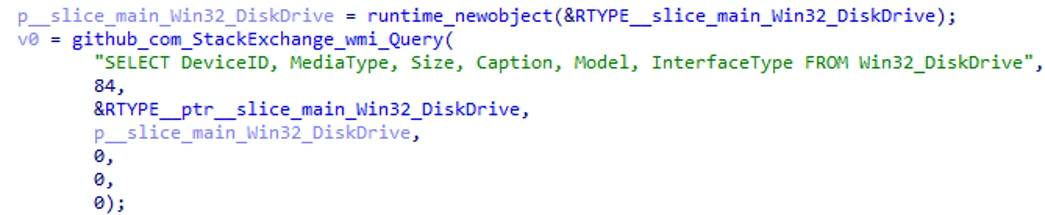
GigaWiper is a destructive backdoor that combines multiple wiping and ransomware-like capabilities into a single operational platform. This blog analyzes how the malware incorporates code from several
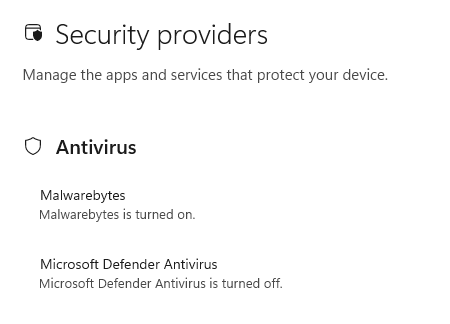
The RoguePlanet zero-day is now fixed in Microsoft Defender. Here's how to make sure your system is protected.
A cybersecurity startup dangling millions of dollars to acquire zero-day security vulnerabilities in popular software is run by a pair of far-right conspiracy theorists and convicted felons whose most
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Jul. 7, 2026 – Listen to the podcast EdTech company Instructure confirmed a massive data breach this past spring.