27th July – Threat Intelligence Report
For the latest discoveries in cyber research for the week of 27th July, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Nichirei, a Japan-based frozen-food supplier and logi
For the latest discoveries in cyber research for the week of 27th July, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Nichirei, a Japan-based frozen-food supplier and logi
ESAFENET&#;x26;#;39;s CDG showed up in our data before. The company focused on secure document management and data leakage prevention solutions. The "CDG" stands for "Conte
Last week, there were disclosed in WordPress Core, and no WordPress themes that have been added to the Wordfence Intelligence Vulnerability Database, and there were that contributed to WordPress Secur
Laundry Bear exploited a zero-day vulnerability for five months before it was patched in July 2025, and the group is still actively exploiting vulnerable environments. The post Russian espionage group
PRISM, our autonomous AI researcher, is now our #1 vulnerability researcher. A look at AI's new threat landscape — and the new kind of defender it demands. The post A New Threat Landscape Meets A New
HermeticReader is a now-patched vulnerability in Adobe's popular Acrobat Chrome extension that could have been used to spy on WhatsApp Web users.
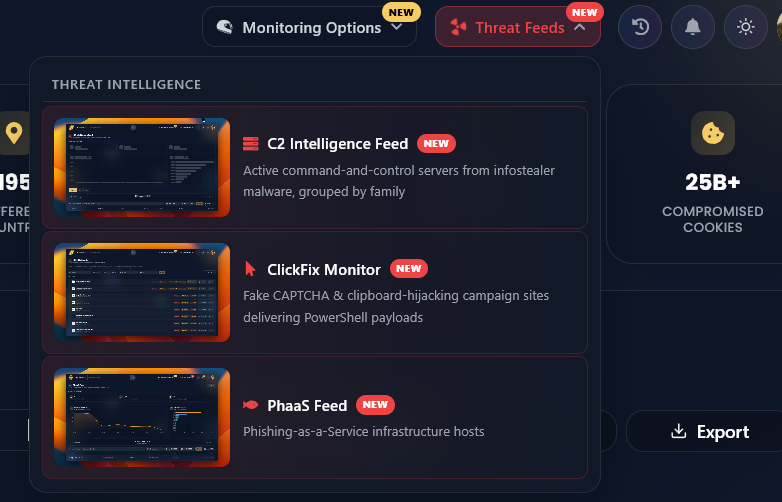
Introducing Cavalier’s New Threat Feeds: Comprehensive Visibility into Attacker Infrastructure We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and Phaa
The worm blends in with thousands of other commands occurring daily in any given environment, yet its intent and origins remain unknown. The post Malware is targeting AI tools in software development
Attackers started exploiting the critical wp2shell vulnerability chain within hours of patches being released, putting sites and their visitors at risk.
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Jul. 21, 2026 – Read the full story in StationX Nathan House, founder and CEO at StationX, one of the UK’s
A new macOS infostealer tricks victims into revealing their system password and installs a persistent backdoor for future access.
Introducing Cavalier’s New Threat Feeds: Deep Dive into Phishing-as-a-Service (PhaaS) Intelligence We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and
Introducing Cavalier’s New Threat Feeds: Deep Dive into ClickFix Monitoring We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and PhaaS (Phishing-as-a-se
Introducing Cavalier’s New Threat Feeds: Deep Dive into Infostealer C2 Intelligence We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and PhaaS... The po
wp2shell is a critical unauthenticated RCE chain in WordPress Core, patched July 17, 2026. See who's affected, the exploitation timeline, and what to do now. The post wp2shell Aftermath: The First Cri
Last week, Searchlight Cyber released details about a vulnerability they are calling "wp2shell". The vulnerability was initially announced without a CVE number. But now has been assigned CVE-2026-6303
The release of The Odyssey has already sparked a wave of piracy scams, from fake browser errors to malware masquerading as movie files.
For the latest discoveries in cyber research for the week of 20th July, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Ernst & Young, a global accounting and profession
We look into how attackers are using the legitimate Ren'Py game engine to spread a malware loader that ultimately delivers Amatera Stealer.
On July 17, 2026, the WordPress Security Team released updates to WordPress core addressing two security vulnerabilities. The first is an unauthenticated SQL injection vulnerability identified as CVE-