Friday Squid Blogging: Neon Flying Squid
The neon flying squid can fly in formation. The shoal of about 100 squid rose unexpectedly from a patch of the Pacific Ocean around 370 miles from Tokyo and glided near the boat for about 30 metres. T
The neon flying squid can fly in formation. The shoal of about 100 squid rose unexpectedly from a patch of the Pacific Ocean around 370 miles from Tokyo and glided near the boat for about 30 metres. T
The private equity firm said attackers broke into some of its cloud platforms during a five-day period in early July, compromising sensitive personal data. The post Apollo discloses data breach from o
Last week, there were disclosed in and that have been added to the Wordfence Intelligence Vulnerability Database, and there were that contributed to WordPress Security last week. Review those vulnerab
On August 10th, 2026, we received a submission for an Unauthenticated Privilege Escalation vulnerability in Pods, a WordPress plugin with more than 100,000 active installations. This vulnerability all
Sen. Ron Wyden and Rep. Greg Casar want a GAO probe on the government’s use of spyware and other sophisticated hacking tools and authorities. The post Lawmakers seek watchdog review of federal hacking
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Aug. 21, 2026 – Read the full Irish Times Story A special report from The Irish Times declares cyber fr
Healthcare technology provider CareCloud confirmed that 3.75 million people were affected by a March data breach.
The AI Security Institute has a new report of AI systems engaging in "unsanctioned behavior"—what I have been calling " genie behavior —while being tested on their cybersecurity capabiliti
Kaspersky expert has discovered new Android malware designed to serve ads and build a proxy botnet. It's delivered through legitimate software for DoFun head units.
In every MFA rollout, there will come a time where you think you are closing in on "done", and some automation to list what&#;x26;#;39;s left would be handy. Something quic
(c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.
One thing that folks never seem to do after "going to the CLOOOOUUUUD" is to look at their logs, logs that they would have checked daily when things were on premise. 
 One log that really bears lo
As firewall rule sets grow in complexity, security teams face a common challenge: manual log analysis is used to determine which rules are actively matching traffic and which are consuming capacity wi
OpenAI presented details of its AI’s model’s cyberattack on Hugging Face at Black Hat last week. Simon Willison details the timeline. It’s really interesting to read through—an
The Combating Organized Retail Crime Act has won a big House vote and could be on the fast track in the Senate — and supporters say it could help fight cybercrime. The post Retail theft bill spurs ‘ve
Flashpoint’s monthly analysis of insider threat recruitment, illicit access advertising, and threat actor activity targeting enterprise environments. The post Insider Threat Report: Dark Web Recruitme
On July 24th, 2026, we received a submission for an Unauthenticated Arbitrary File Upload vulnerability in Elementor Pro, a WordPress plugin with an estimated 6,000,000 active installations. This vuln
The designation would unlock a range of federal services, tools and resources for an industry that policymakers view as increasingly tied to national and economic security. The post The push to design
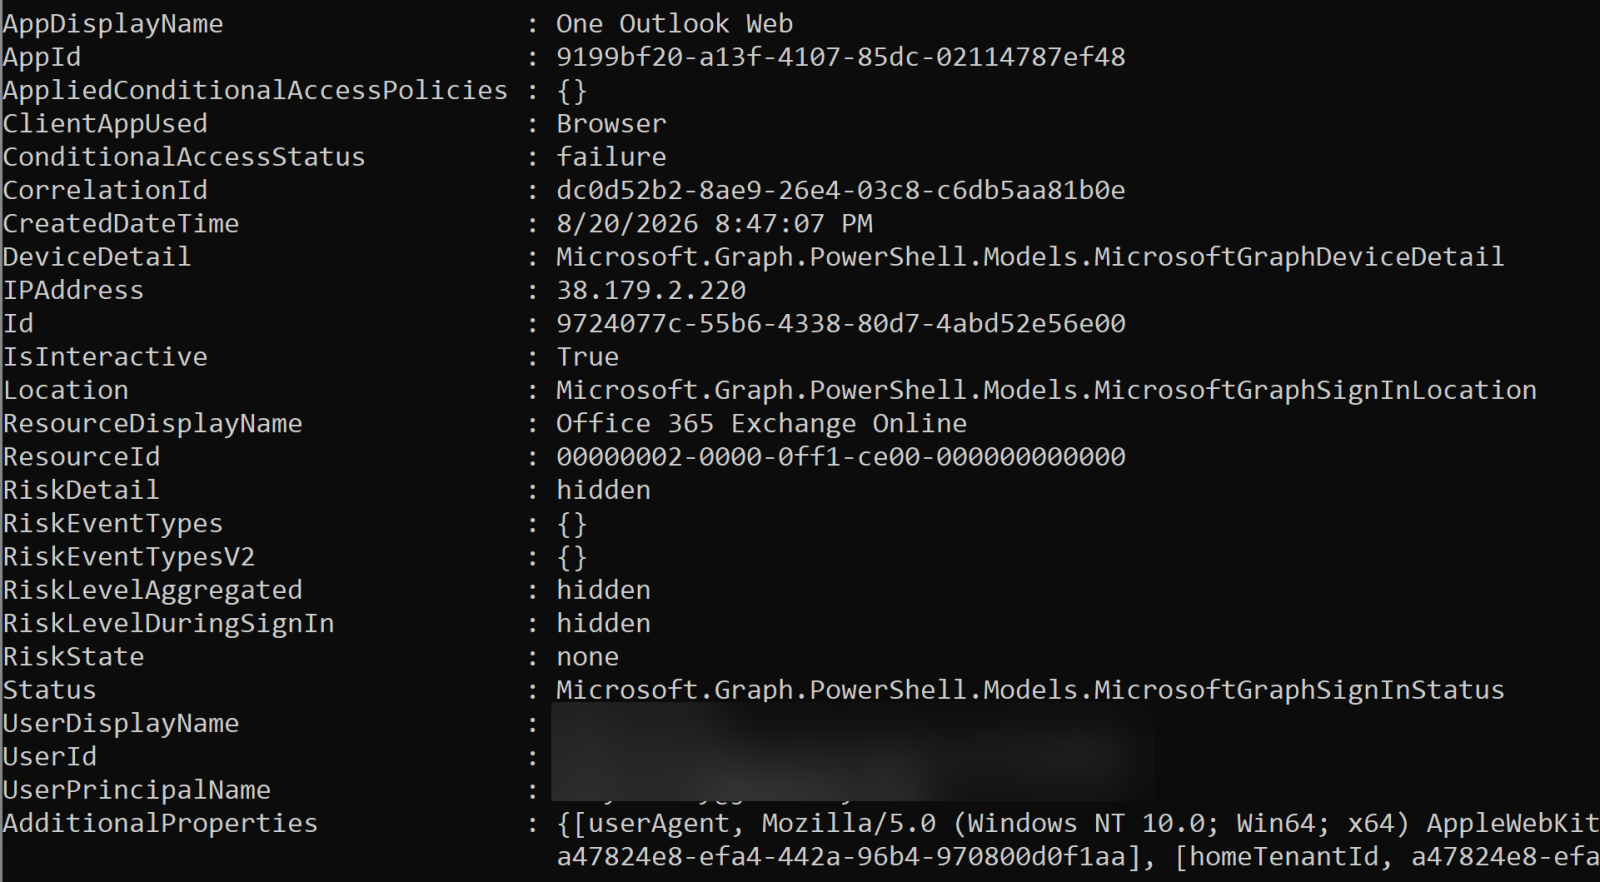
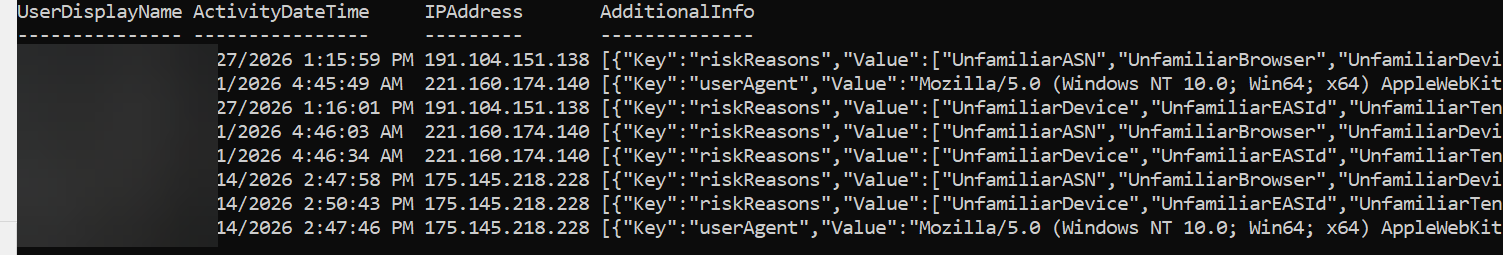
Building on the last diary on Using MS Graph and Powershell, let&#;x26;#;39;s look at "Risky" logins. 
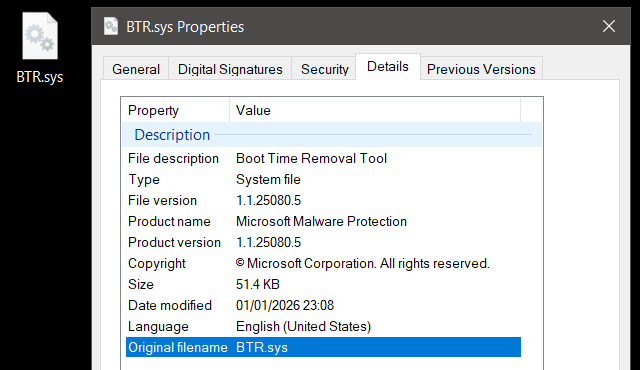
Research by: Jiří Vinopal (@vinopaljiri) Abstract What if a trusted security component could be repurposed into an attacker-controlled kernel primitive? What if a signed Microsoft remediation driver c