
AI Hackers Are Dumb And They Can Wreak Havoc
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Sep. 17, 2026 – Watch the Video "It’s never been tougher for a practitioner to secure their environment," S
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Sep. 17, 2026 – Watch the Video "It’s never been tougher for a practitioner to secure their environment," S
Kaspersky experts have discovered a new MovieReaper campaign. The multi-stage Trojan spreads through movie torrents, such as "The Odyssey," and uses the Solana blockchain to hide its C2 infrastructure
A large phishing campaign is using fake T-Mobile rewards points and looming expiry dates to pressure recipients into clicking malicious links.
Ports, railroads, and utilities keep the military operational. They're all vulnerable to Iranian cyberattacks. The post America’s cyber strategy overlooks the infrastructure that actually keeps
(c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.
It’s the first guidance from the Cybersecurity and Infrastructure Security Agency on deploying decoys, like honeypots, to detect and distract adversaries. The post CISA promotes a fresh way to deter c
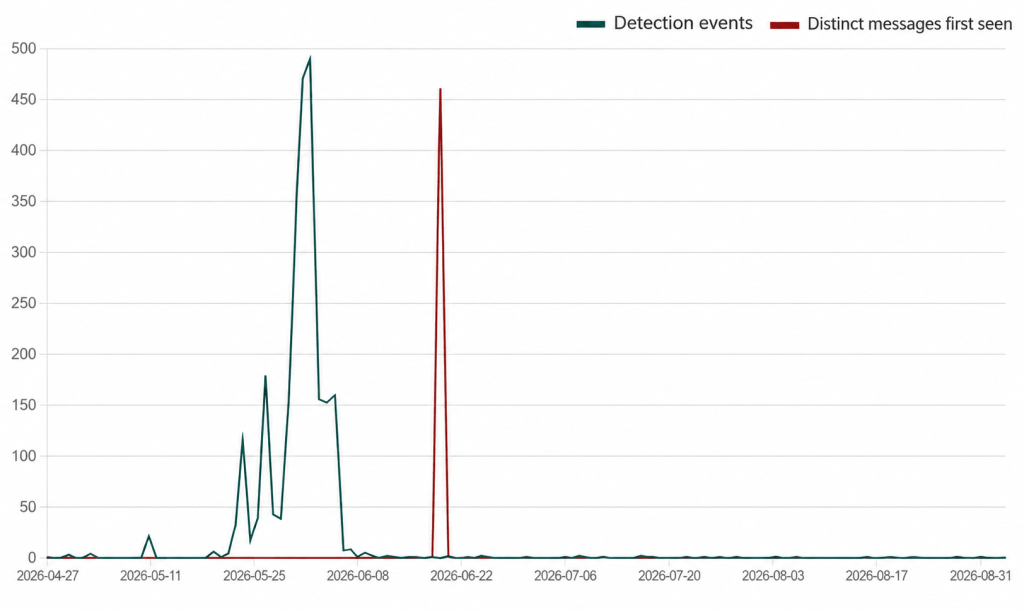
Earlier today, I noted an odd request showing up in our "First Seen" report: 
The consumer data broker Radaris.com has long had a reputation for ignoring requests to remove personal information from its vast empire of people-search services online. That reputation caught up wit
The agencies issued a joint statement saying the “joint security boardings” came in response to “indications that the networks of both vessels were compromised.” The post Coast Guard, FBI board US-bou
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Sep. 16, 2026 – Listen to the Podcast Silk Road 2.0 was a dark web marketplace launched in Nov. 2013, approx
Google’s September Pixel update fixes 110 vulnerabilities, including a modem flaw being used in limited, targeted attacks.
Kaspersky GERT experts have uncovered a new campaign by the NightEagle APT, featuring the GhostContainer backdoor and tools hosted on GitHub. The group is also exploiting vulnerabilities in Active Dir
(c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.
AWS Security Token Service (AWS STS) has simplified session token size limits, giving you more room for your session policies and session tags. STS has replaced the packed policy size and the overall
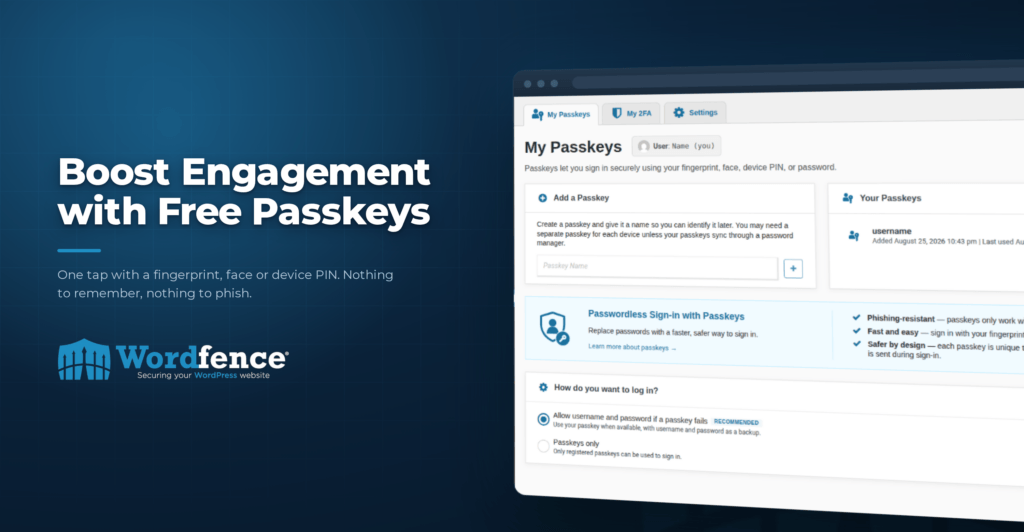
Wordfence 9 introduces passkeys, and passkeys provide a huge friction reduction because your user no longer has to remember their password or retrieve it from a password manager and copy/paste. The po
Three feds spoke about future plans for the Continuous Diagnostics and Mitigation program, and lessons they’ve learned. The post What’s next for CISA’s CDM program that gives cybersecurity tools
Your consumer identity and access management (CIAM) system is the foundation of your customer experience. It’s how users sign in, access services, and engage with your applications. As your business s
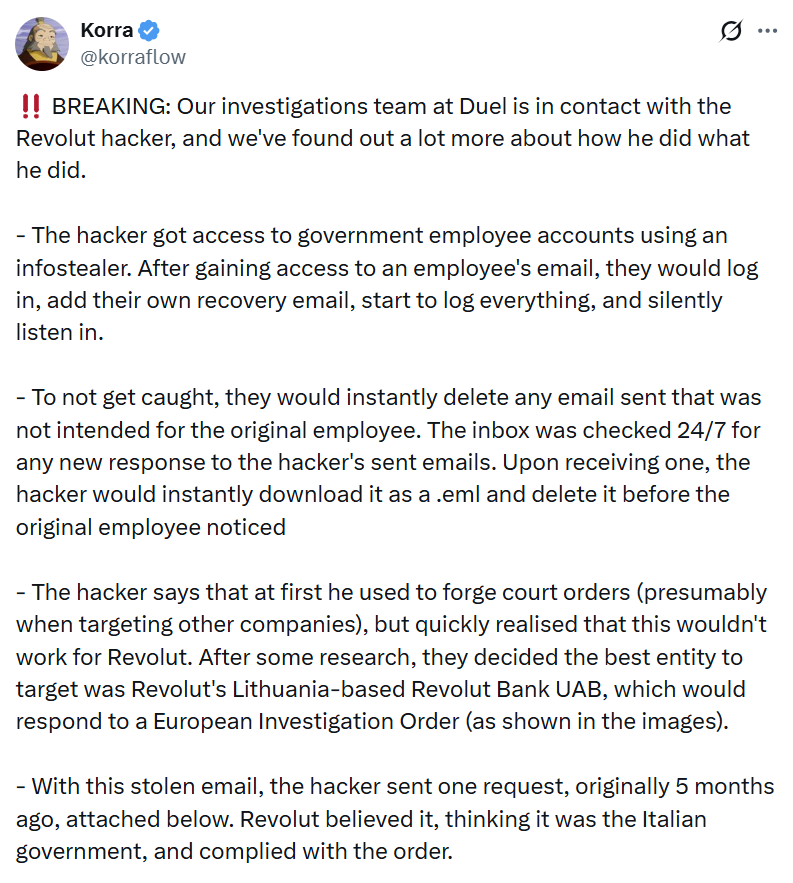
Revolut Hackers Exploited Infostealers for Social Engineering Revolut Hackers Used Infostealers for Elaborate Social Engineering BREAKING: The investigations team at Duel has established contact with
The company confirmed the defect was exploited before it was disclosed and patched, but it did not describe the nature of the attacks or the scope of impact across its customer base. The post Cisco wa
I have not done this type of diary in a while: What traffic will you see from a system on boot, before a user logs in? I just took a quick look at macOS 27 "Golden Gate" to see what traffic you s