How Bad Is The 2026 Data Breach Crisis?
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Oct. 26, 2026 – Read the Full Story from Encryption Consulting Cybersecurity Ventures projects global cybercrime
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Oct. 26, 2026 – Read the Full Story from Encryption Consulting Cybersecurity Ventures projects global cybercrime
The California Department of Education notified students about a data breach at contractor Educational Testing Service.
Google has frozen its OSS VRP product vulnerability submissions to stop the flood of AI generated vulnerability reports.
A malicious file could trigger the vulnerability. Apple says it may already have been used against iPhone users.
The report details a Russian-aligned espionage campaign against more than 20 organizations, an exploit foundry run by Chinese undergraduates and ShinyHunters-affiliated breaches, among other disrupted
Four different espionage groups used the same exploit kit to target recently fixed flaws, showing why “patch later” is a dangerous gamble.
The ongoing social engineering threat, which dates back to late 2025, tricks victims into granting threat actors long-term access to their accounts. The post FBI raises alarm over deceptive phishing c
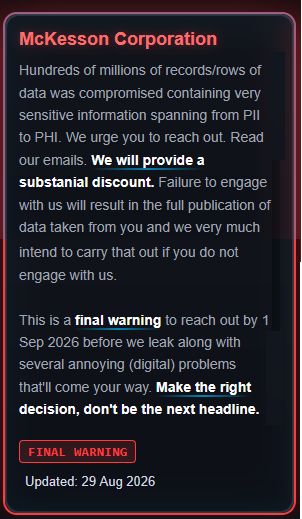
Healthcare company McKesson acknowledged a data breach. ShinyHunters claims to have stolen hundred of millions of records
Chrome’s latest update fixes 327 security vulnerabilities, including some that malicious websites could exploit as soon as you visit them.
The private equity firm said attackers broke into some of its cloud platforms during a five-day period in early July, compromising sensitive personal data. The post Apollo discloses data breach from o
Healthcare technology provider CareCloud confirmed that 3.75 million people were affected by a March data breach.
Leaked personal and financial data of around 750,000 US citizens, including SSNs and bank details, could put victims at risk of identity theft and phishing.
Attackers are exploiting a Mac Screen Sharing vulnerability to gain root access and install Monero cryptominers.
Apple is fighting another attempt by the UK's Home Office to get a backdoor providing access to encrypted iCloud data.