Is this link safe? Find out with Malwarebytes Scam Link Check
Not sure if a link is safe? Malwarebytes Scam Link Check scans suspicious links for signs of phishing, scams, malware, and other online threats before you click.
Not sure if a link is safe? Malwarebytes Scam Link Check scans suspicious links for signs of phishing, scams, malware, and other online threats before you click.
Since January 2026, Microsoft has observed Russian state threat actor Star Blizzard evolve their detection evasion capabilities through large-scale phishing campaigns, the use of accounts on compromis
See how Microsoft Defender detects and disrupts AI-themed phishing, malware, and multi-stage attacks across the attack chain. The post Detect and disrupt AI-themed attacks with Microsoft Defender appe
We cover a cloud-based AitM attack scenario leveraging service workers and Ultraviolet, and provide detailed phishing hosting statistics across platforms like Cloudflare Workers, Vercel, Netlify, GitH
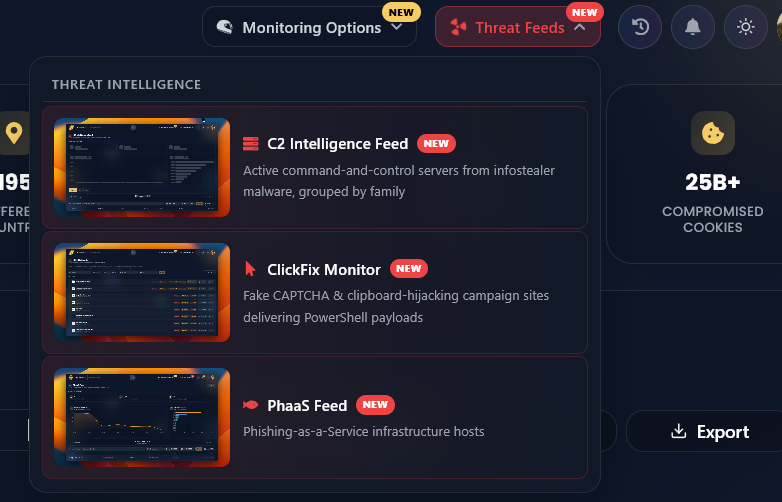
Introducing Cavalier’s New Threat Feeds: Comprehensive Visibility into Attacker Infrastructure We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and Phaa
Introducing Cavalier’s New Threat Feeds: Deep Dive into Phishing-as-a-Service (PhaaS) Intelligence We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and
Introducing Cavalier’s New Threat Feeds: Deep Dive into ClickFix Monitoring We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and PhaaS (Phishing-as-a-se
An inside look at the active Armored Likho APT campaign. The attackers are using spear-phishing, AI-generated loaders, and a new Python-based tool, BusySnake Stealer, to target organizations in Russia
A phishing campaign installs a malicious Chrome extension to hijack browser sessions and compromise Windows devices.
Malwarebytes got top marks in independent tests against malware, phishing, and other online threats.
We found EtherRAT malware being distributed by a website with a strange homepage. Following the trail, we discovered a vast network of malicious infrastructures, distributing malware, malicious docume
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – May. 28, 2026 – Read the full story in Daily Mirror Hilmy Cader warns that the intensity and sophistica
Executive Summary Cyble Research and Intelligence Labs (CRIL) has identified a novel Android banking trojan, dubbed OverlayPhantom, actively distributed in the wild via malicious URLs. The malware emp
Executive Summary Cyble Research and Intelligence Labs (CRIL) has uncovered a targeted cyberespionage campaign leveraging social engineering and trusted infrastructure to establish persistent, covert