The Gentlemen are knocking: сustom backdoors and evolving tactics
Kaspersky researchers analyze incidents related to The Gentlemen RaaS group, disclose their tools and TTPs, and find a new ransomware variant.
Kaspersky researchers analyze incidents related to The Gentlemen RaaS group, disclose their tools and TTPs, and find a new ransomware variant.
A phishing campaign installs a malicious Chrome extension to hijack browser sessions and compromise Windows devices.
Six weeks of undetected access through a compromised VPN exposes why patching isn't a solution for the organizations already breached. The post Why patch directives only go so far appeared first on Cy
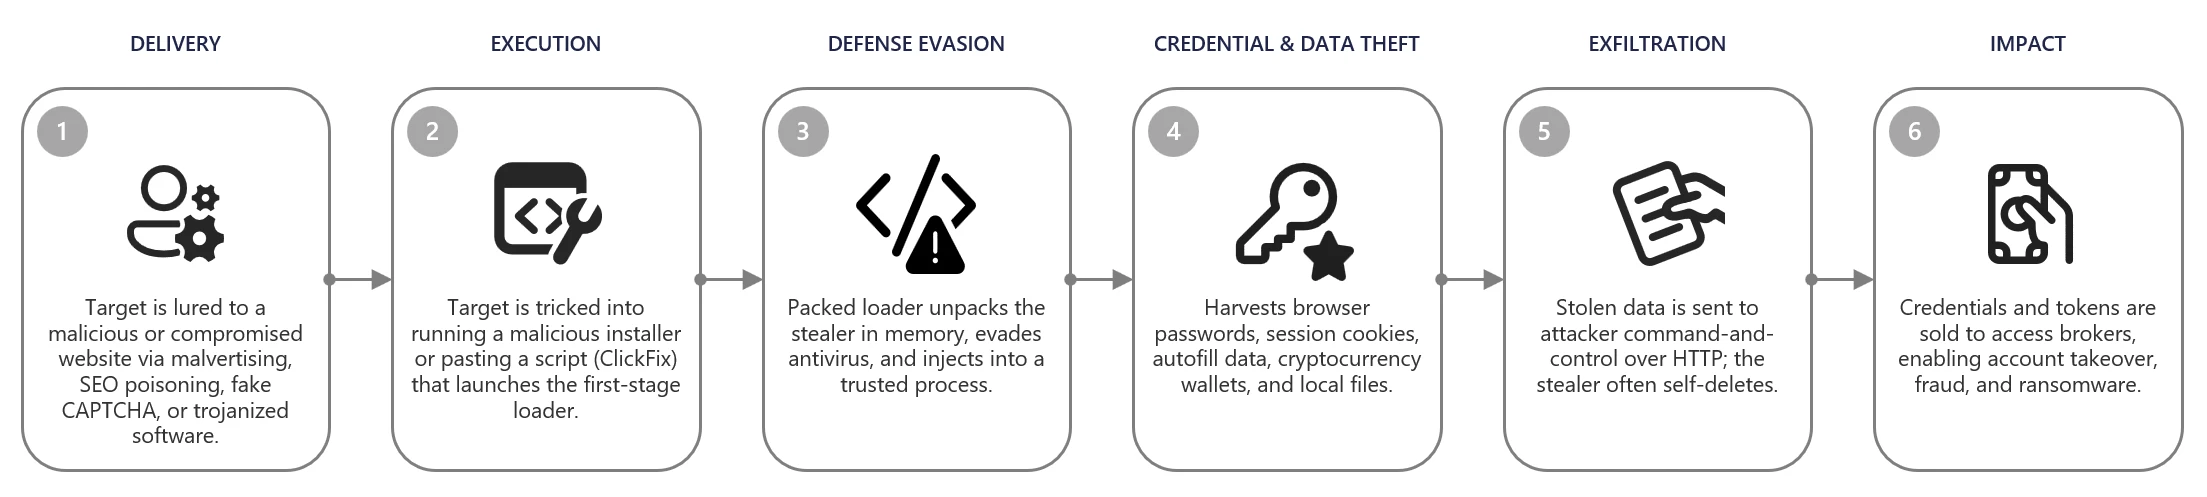
On June 24, 2026, Microsoft’s Digital Crimes Unit (DCU) facilitated the takedown, suspension, and blocking of domains that formed the backbone of the StealC and Amadey infrastructure. This blog is a t
Microsoft, with law enforcement and industry partners, disrupted more than 200 command and control servers for Amadey and StealC, often used in conjunction. The post In a first, a court takedown goes
At least one malware developer is adding text about nuclear and biological weapons to their spyware, in an effort to stop automatic AI analysis. Details : The _index.js payload begins with a large Jav
They say they have videos, malware, and total control of your devices. Here's how to read a sextortion email like a security researcher instead of a victim.
Kaspersky researchers analyze a new global campaign dubbed StrikeShark that delivers Cobalt Strike Beacon via custom SharkLoader malware.
We spent 48 hours exploring the dark web and found stolen identities, malware, scams, and a thriving cybercrime economy.
Ransomware case reveals two parallel threat actors, blending tactics and evasion—showing why isolated signals can often miss modern, overlapping cyberattacks. The post One intrusion, two cyberattacker
Thousands of outdated D-Link routers have been absorbed into the AryStinger botnet, with no future security updates available to protect them.
Thousands of everyday websites were cleaned as part of a global operation targeting the malware network behind fake browser update scams.
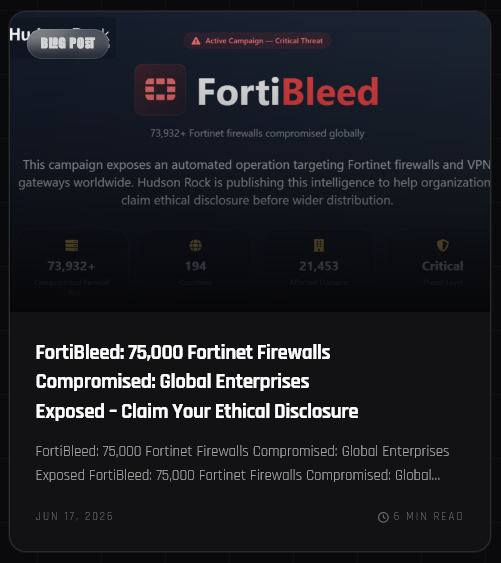
Fortibleed updates from Hudson Rock Inside the FortiBleed Response: Hudson Rock’s Insights into the Global Disclosure Effort The past few days following our publication on the Fortinet compromis
Cybersecurity firms, researchers and officials took down 106 servers and remediated nearly 15,000 sites that were infected with the malware. The post Authorities disrupt Evil Corp’s SocGholish botnet
For the past four years, a sprawling Android-based botnet called Popa has forced millions of consumer TV boxes to relay Internet traffic linked to advertising fraud, account takeovers, and mass data-s
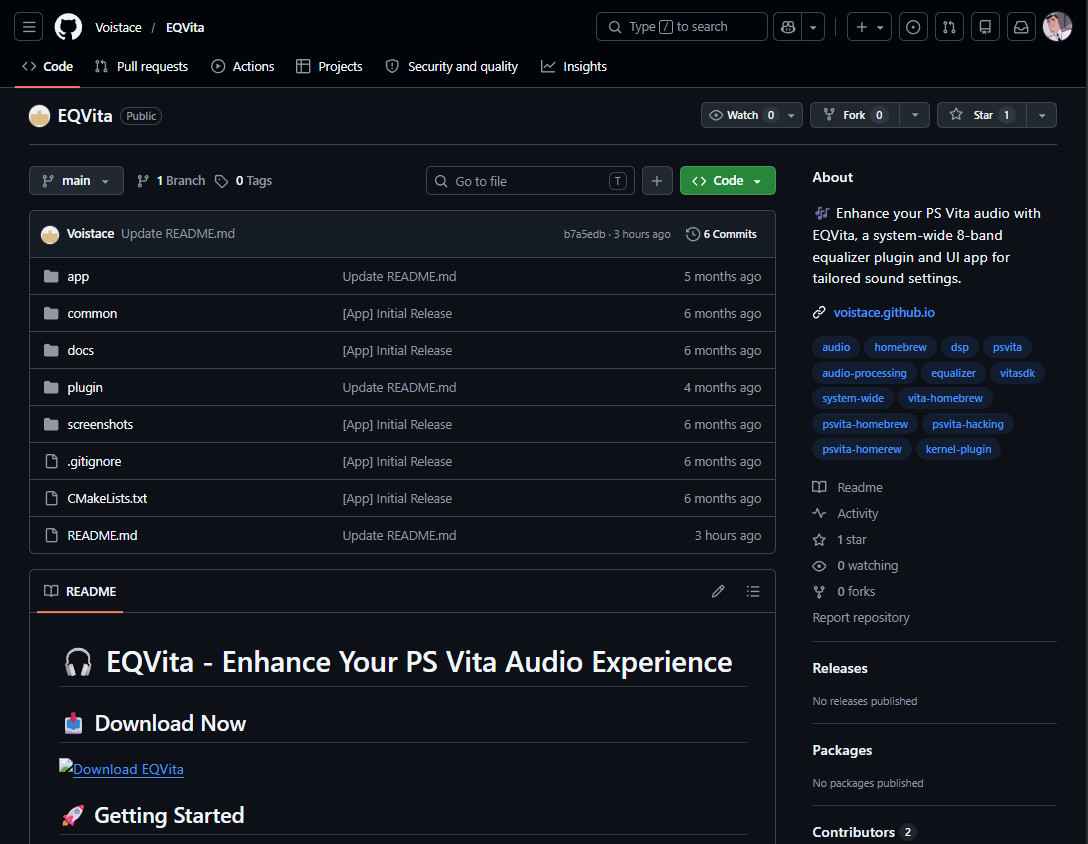
Retro gaming fans should be careful with GitHub projects that claim to be tools or plugins for their consoles. We looked at one example aimed at PlayStation Vita owners.
At least one malware developer is adding text about nuclear and biological weapons to their spyware, in an effort to stop automatic AI analysis. Details : The _index.js payload begins with a large Jav
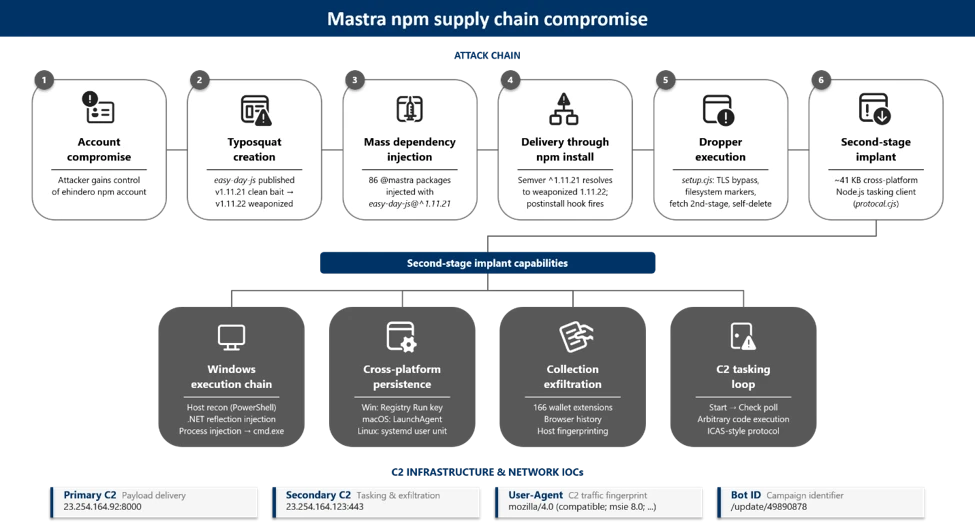
A poisoned npm package infected 140+ projects with a hidden payload. This report highlights how to detect, hunt, and defend against supply chain attacks using Microsoft Defender and actionable threat
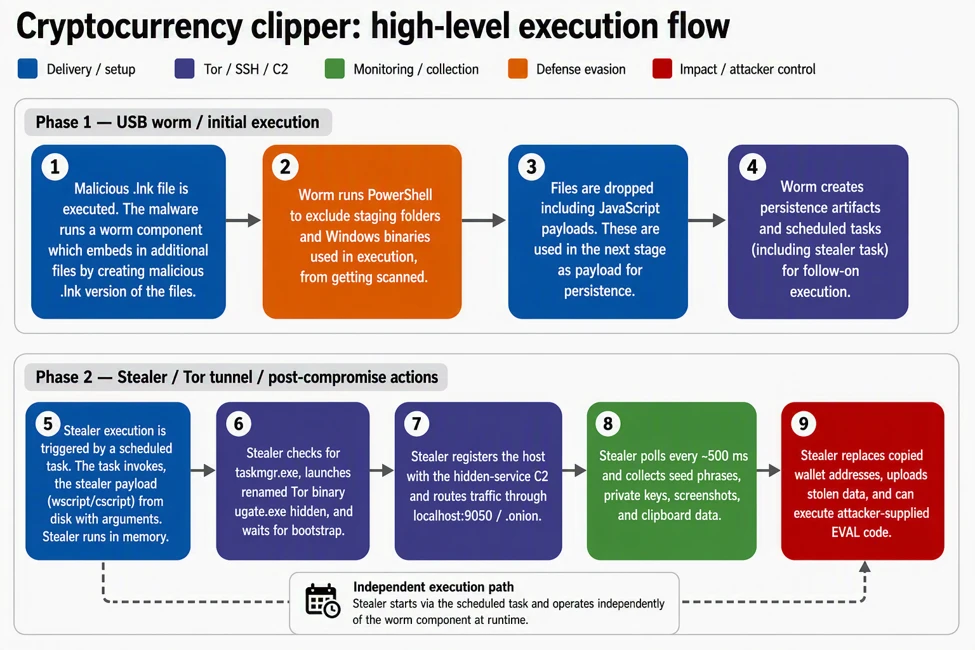
Microsoft Threat Intelligence analyzed a cryptocurrency clipper campaign that combines clipboard theft, wallet replacement, Tor-based communications, and worm-like propagation. Beyond stealing cryptoc
Attackers are using fake job offers and malware to steal accounts, Robux, and Roblox games from the developers who build them.