Toy Ghouls’ new toy: the GenieLocker ransomware
Kaspersky experts dissect GenieLocker: new custom ransomware variants for Windows, Linux, and ESXi systems. We found this family in attacks by Toy Ghouls, a financially motivated extortion group.
Kaspersky experts dissect GenieLocker: new custom ransomware variants for Windows, Linux, and ESXi systems. We found this family in attacks by Toy Ghouls, a financially motivated extortion group.
Your phone needs more than a lock screen to stay safe. We've rebuilt Malwarebytes Mobile Security to put scam protection first and keep your phone secure.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
For the latest discoveries in cyber research for the week of 27th July, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Nichirei, a Japan-based frozen-food supplier and logi
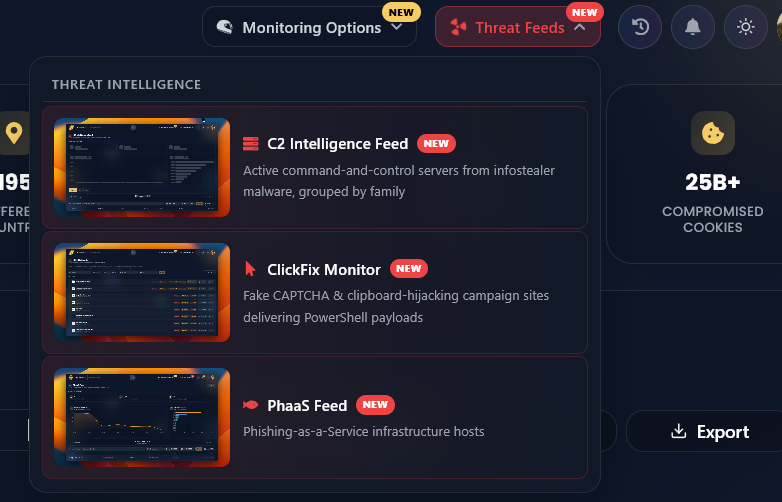
Introducing Cavalier’s New Threat Feeds: Comprehensive Visibility into Attacker Infrastructure We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and Phaa
The worm blends in with thousands of other commands occurring daily in any given environment, yet its intent and origins remain unknown. The post Malware is targeting AI tools in software development
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Jul. 21, 2026 – Read the full story in StationX Nathan House, founder and CEO at StationX, one of the UK’s
A new macOS infostealer tricks victims into revealing their system password and installs a persistent backdoor for future access.
Introducing Cavalier’s New Threat Feeds: Deep Dive into Phishing-as-a-Service (PhaaS) Intelligence We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and
Introducing Cavalier’s New Threat Feeds: Deep Dive into ClickFix Monitoring We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and PhaaS (Phishing-as-a-se
Introducing Cavalier’s New Threat Feeds: Deep Dive into Infostealer C2 Intelligence We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and PhaaS... The po
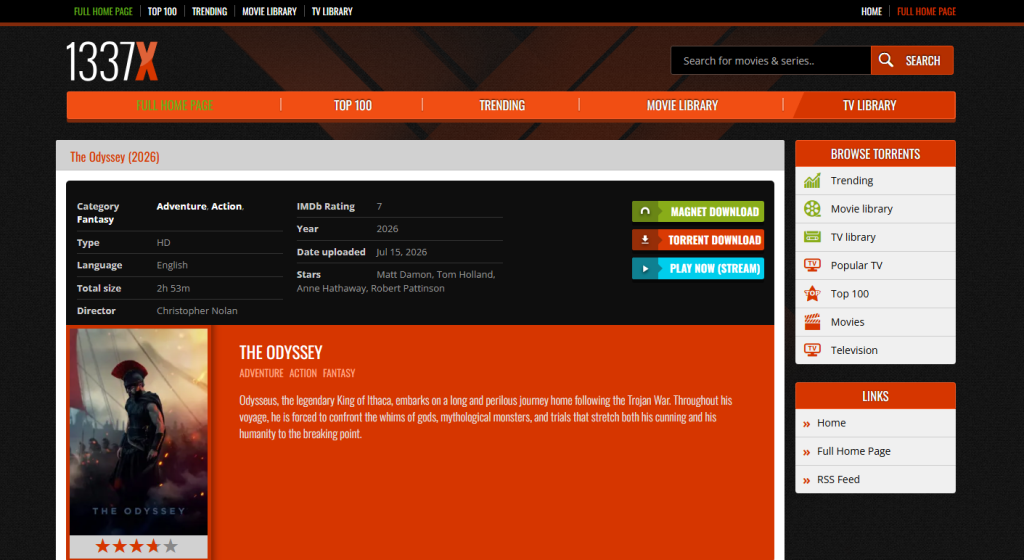
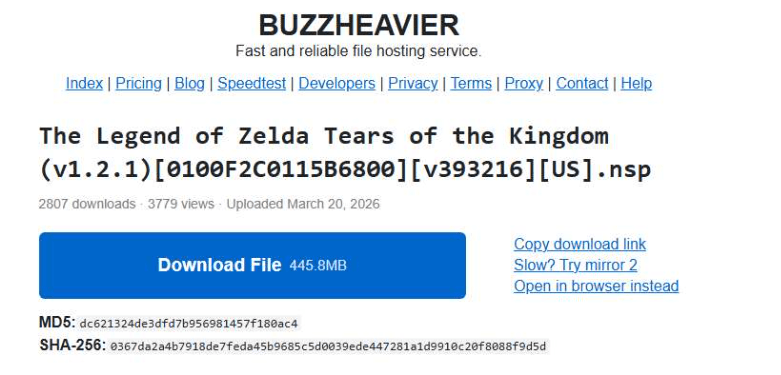
The release of The Odyssey has already sparked a wave of piracy scams, from fake browser errors to malware masquerading as movie files.
We look into how attackers are using the legitimate Ren'Py game engine to spread a malware loader that ultimately delivers Amatera Stealer.
Thalha Jubair and Owen Flowers led and directed many attacks attributed to the hacker subset of The Com. U.S. authorities previously accused Jubair of participating in at least 120 attacks. The post L
Knowing how to spot a malicious GitHub repository can help you avoid downloading malware disguised as legitimate software.
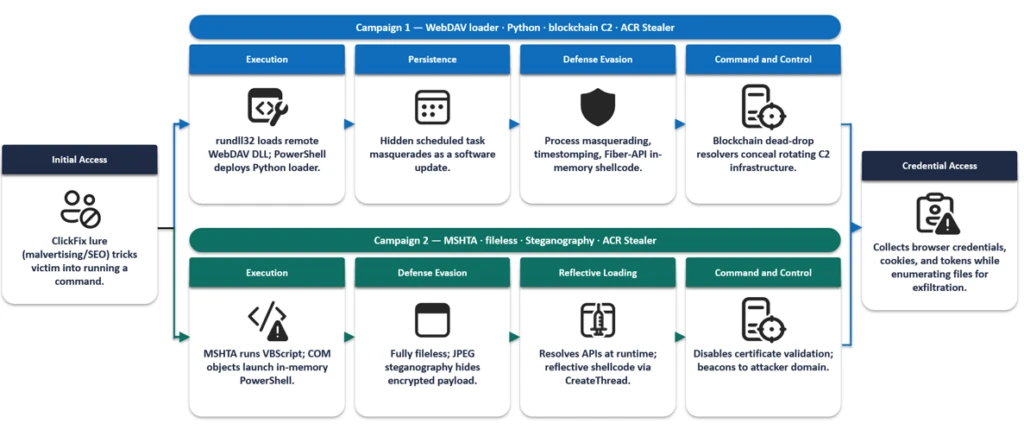
From late April 2026 to mid-June 2026, Microsoft Defender Experts observed increased ACR Stealer activity across customer environments. These campaigns are successfully using ClickFix lures to steal b
Officials accused three Russian nationals, Media Land and ML.Cloud of supporting cyberattacks spanning 21 U.S. states and other countries, resulting in losses surpassing $62 million. The post Russian
Two-phase attacks with the GoSerpent backdoor, Stowaway RAT, ThumbcacheService and other tools aim to steal data from government entities in Southeast Asia.
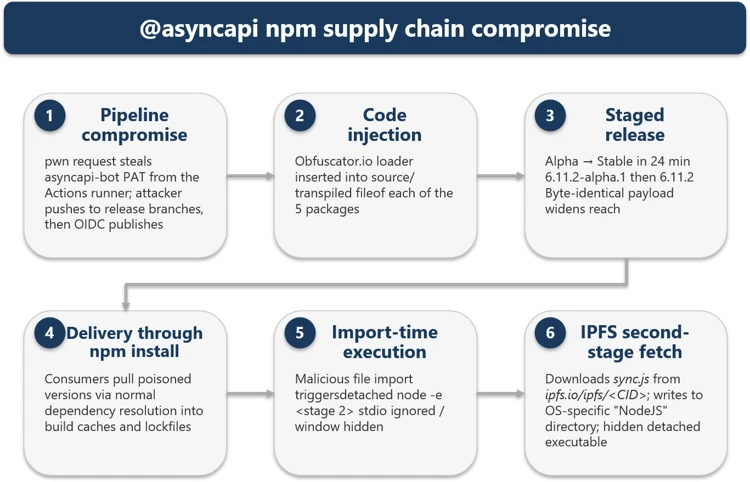
Threat actors compromised AsyncAPI packages and weaponized trusted CI/CD workflows to distribute malware through npm. This analysis breaks down the attack chain, payload delivery, and recommended defe
Kaspersky GReAT experts dissect the new OkoBot campaign targeting cryptocurrency users. This complex framework employs TookPS, exfiltrates seed phrases, monitors Chromium-based browsers, and installs