Google’s synchronized passkeys can be stolen in ‘Pass‑ta‑key’ attacks
Over time, passkeys are supposed to replace passwords. But what happens when malware steals the master key?
Over time, passkeys are supposed to replace passwords. But what happens when malware steals the master key?
Researchers from multiple security firms observed a variant of Mini Shai-Hulud, self-replicating malware linked to TeamPCP, in all the affected packages. The post Massive supply-chain attack compromis
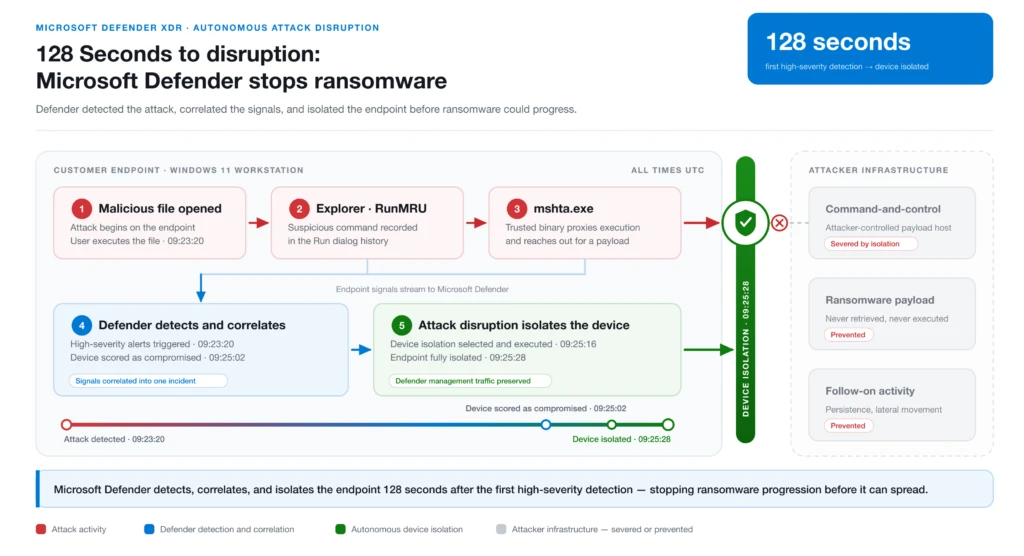
Microsoft Defender automatically isolated a compromised QNET endpoint in 128 seconds, stopping a multi-stage attack before the payload could persist or spread. The post 128 Seconds to disruption: Micr
INC ransomware wasn’t the first group to exploit the zero-days, but it’s been the most assertive and effective in chaining both vulnerabilities to steal and encrypt data for extortion. The post Prolif
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Aug. 4, 2026 – Listen to the podcast "This wasn’t someone behind the keyboard using AI as a tool to write m
Researchers have uncovered a new campaign that spreads the AtlasRAT remote access Trojan by disguising it as a Flash Player installer.
Kaspersky experts dissect GenieLocker: new custom ransomware variants for Windows, Linux, and ESXi systems. We found this family in attacks by Toy Ghouls, a financially motivated extortion group.
For the latest discoveries in cyber research for the week of 27th July, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Nichirei, a Japan-based frozen-food supplier and logi
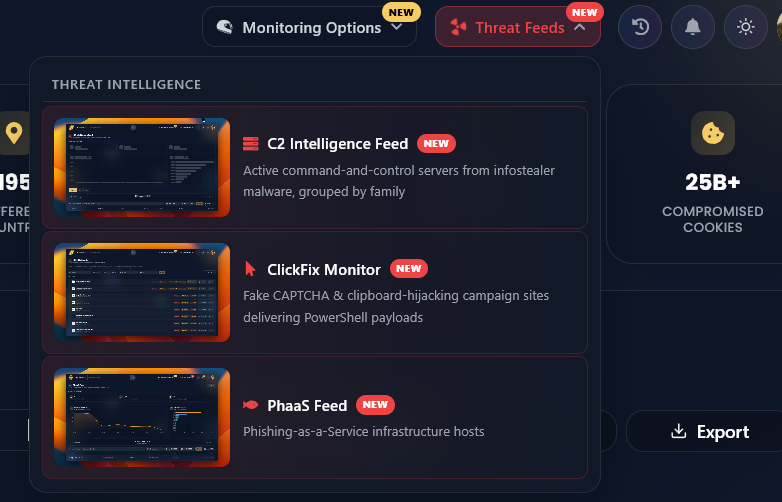
Introducing Cavalier’s New Threat Feeds: Comprehensive Visibility into Attacker Infrastructure We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and Phaa
The worm blends in with thousands of other commands occurring daily in any given environment, yet its intent and origins remain unknown. The post Malware is targeting AI tools in software development
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Jul. 21, 2026 – Read the full story in StationX Nathan House, founder and CEO at StationX, one of the UK’s
A new macOS infostealer tricks victims into revealing their system password and installs a persistent backdoor for future access.
Introducing Cavalier’s New Threat Feeds: Deep Dive into Phishing-as-a-Service (PhaaS) Intelligence We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and
Introducing Cavalier’s New Threat Feeds: Deep Dive into ClickFix Monitoring We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and PhaaS (Phishing-as-a-se
Introducing Cavalier’s New Threat Feeds: Deep Dive into Infostealer C2 Intelligence We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and PhaaS... The po
The release of The Odyssey has already sparked a wave of piracy scams, from fake browser errors to malware masquerading as movie files.
We look into how attackers are using the legitimate Ren'Py game engine to spread a malware loader that ultimately delivers Amatera Stealer.
Knowing how to spot a malicious GitHub repository can help you avoid downloading malware disguised as legitimate software.
The designations hit 1VPNS, its alleged Ukrainian administrator and a Belarusian who allegedly sold “cryptors” to disguise ransomware and other malware. The post Treasury sanctions First VPN Service,
Instead of helping victims negotiate with BlackCat, a trusted ransomware negotiator secretly helped the gang extort them.