OneNote File Extraction
Recently, I had to extract embedded files from a set of OneNote files (extension .one). 
Recently, I had to extract embedded files from a set of OneNote files (extension .one). 
Wireshark Release Candidate 5.0.0 was published : soon we can expect a new major version of Wireshark. 
YARA-X&#;x26;#;39;s 1.22.1 is a bugfix version, it brings 2 bugfixes. 
Introduction 
Apple today released patches for 304 vulnerabilties. This number is still in line with prior Apple updates, and comes just about a month after the last apple update. 
YARA-X&#;x26;#;39;s 1.22.0 release brings 11 improvements and 9 bugfixes. 
Here is the YARA rule I used to detect " Orphaned VBA Projects Inside DWG Files ". 
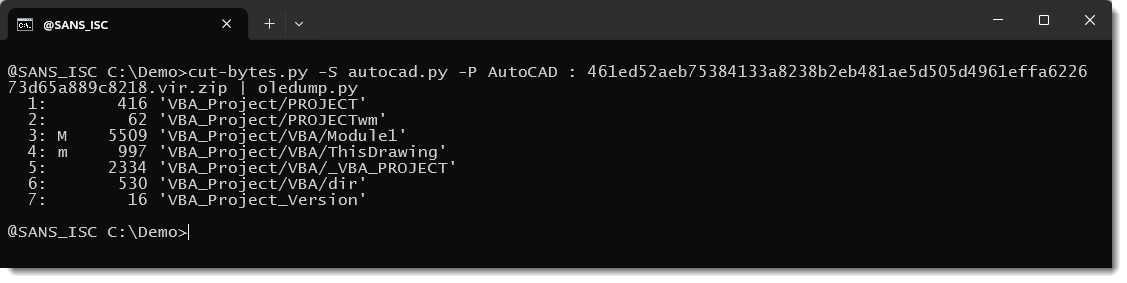
Years ago I wrote diary entries about VBA code stored inside AutoCAD drawing files (.dwg). 
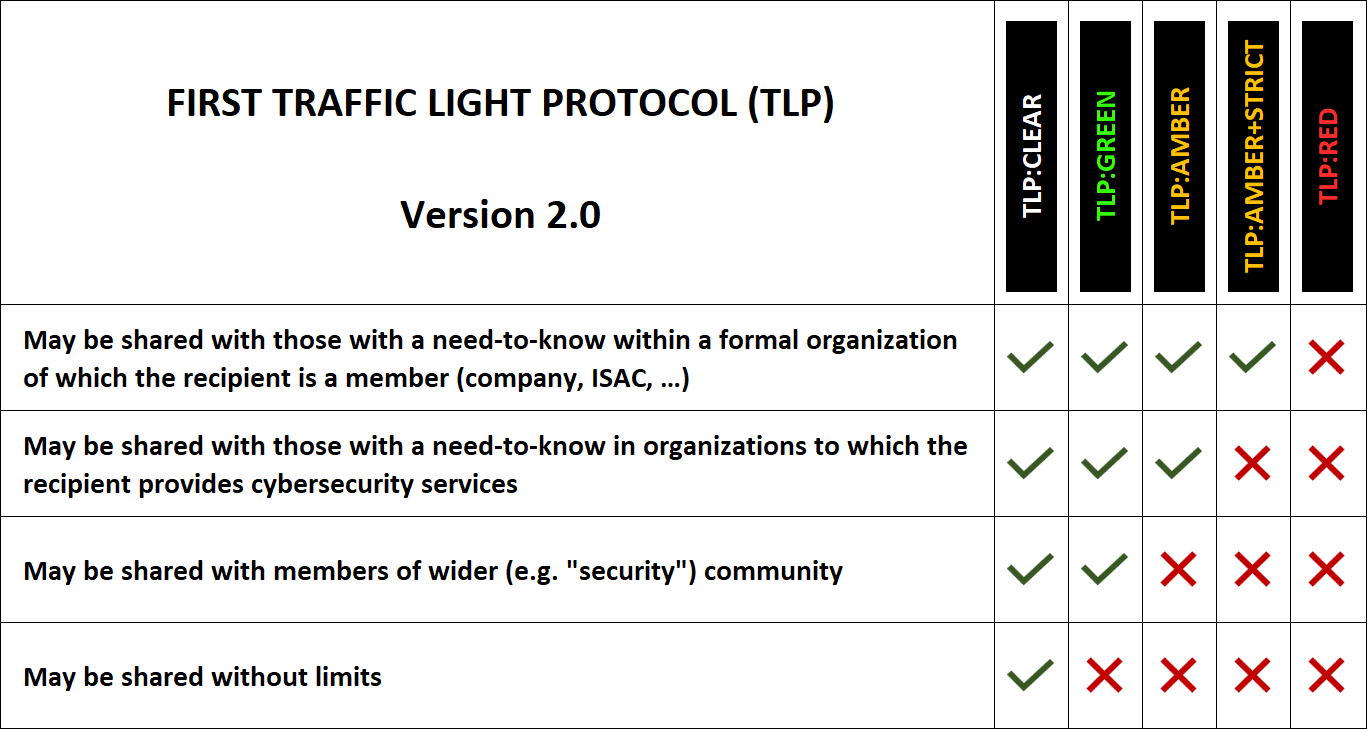
The Traffic Light Protocol (TLP)[ 1 ], which is now in its second incarnation, is a wonderful standard that enables one to easily communicate whether information may be shared further (and i
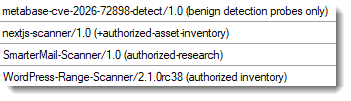
Sometimes I have to smile, or my interest is triggered, when I review new User Agent Strings in the honeypot logs. 
YARA-X&#;x26;#;39;s 1.21.0 release brings 5 improvements and 4 bugfixes. 
Starting yesterday, our sensors picked up a small number of scans for "wordfence-waf.php". This particular script is used by Wordfence, a solution to protect WordPress sites. During the Wordfence inst
Wireshark release 4.6.9 fixes 19 vulnerabilities and 16 bugs. 
Introduction 
On Friday, Xavier talked about the newly introduced HTTP Query method. This new method was introduced to allow "GET" requests that include a body. The main reason for this was that GET requests typica
Earlier today, I noted an odd request showing up in our "First Seen" report: 
I have not done this type of diary in a while: What traffic will you see from a system on boot, before a user logs in? I just took a quick look at macOS 27 "Golden Gate" to see what traffic you s
I identified an attacker using a semi-autonomous coding agent to run an offensive operation: finding poorly secured LLM resale gateways, acquiring API access through ordinary web flaws and account far
​​​​​​​ 
One of my internet-exposed inference honeypots was discovered, relabeled with sought-after model names, and incorporated into infrastructure apparently used to provide "free" LLM backends. It then rec