Reimagining the SOC for the agentic era in Microsoft Defender
We are announcing ISOC in Microsoft Defender: a foundation built for agentic security that brings leading solutions for SIEM and threat protection together. The
In-depth threat intelligence and security research from Palo Alto Unit 42, Cisco Talos, Mandiant, Check Point, CrowdStrike, and other leading intelligence labs.
We are announcing ISOC in Microsoft Defender: a foundation built for agentic security that brings leading solutions for SIEM and threat protection together. The
The Australian Signals Directorate (ASD) has this month issued a clear call to action through its Multi-factor authentication: Switch it on campaign, urging bus
New paper: " Self-Jailbreaking: Language Models Can Reason Themselves Out of Safety Alignment After Benign Reasoning Training ." Abstract: We discover a novel a
In this post, Flashpoint analysts examine Process Parameter Poisoning—a novel EDR evasion technique we validated in Rust—and detail how abusing undocumented pro
The threat group Volexity tracks as UTA0565 showcased a variance in tactics, but it used the same exploit kit as multiple Chinese threat groups. The post Volexi
EvilTokens has quickly become one of the top PhaaS platforms, enabling device code phishing attacks through AI-assisted lures, automated infrastructure, and tok
The popular phishing-as-a-service platform used AI throughout the attack chain, allowing cybercriminals to steal tokens for account takeover and business email
This is pretty amazing: However, the most astonishing thing about this break is that the GPT6 Astra did it entirely on its own. Carter Leffer only directed GPT
For the latest discoveries in cyber research for the week of 21st Setpember, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Japan’s
Security teams investigating possible AI-related security events need guardrail intervention data alongside their existing security telemetry. When a guardrail
Hackers captured a Flock camera and got a look (alternate link ) at the software: While much of the automatic license plate reader’s (ALPR) most sensitive
Born out of academia and raised in corporate IT departments, the Security Assertion Markup Language (SAML) authentication protocol continues to be a staple in t
Short essay about squid egg sacs. As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered. Blog m
Anthropic’s recent security-incident document contains a bit about how CAPTCHAs are still frustrating Claude. In the transcript, the Claude model that is
Security firms have published numerous blog posts describing how they pointed their agent harness at a codebase and found dozens of bugs (we’re one of them). Ho
AI has made fundamental changes to the operating environment for cybersecurity. Explore exposure management guidance on recommended controls and take action and
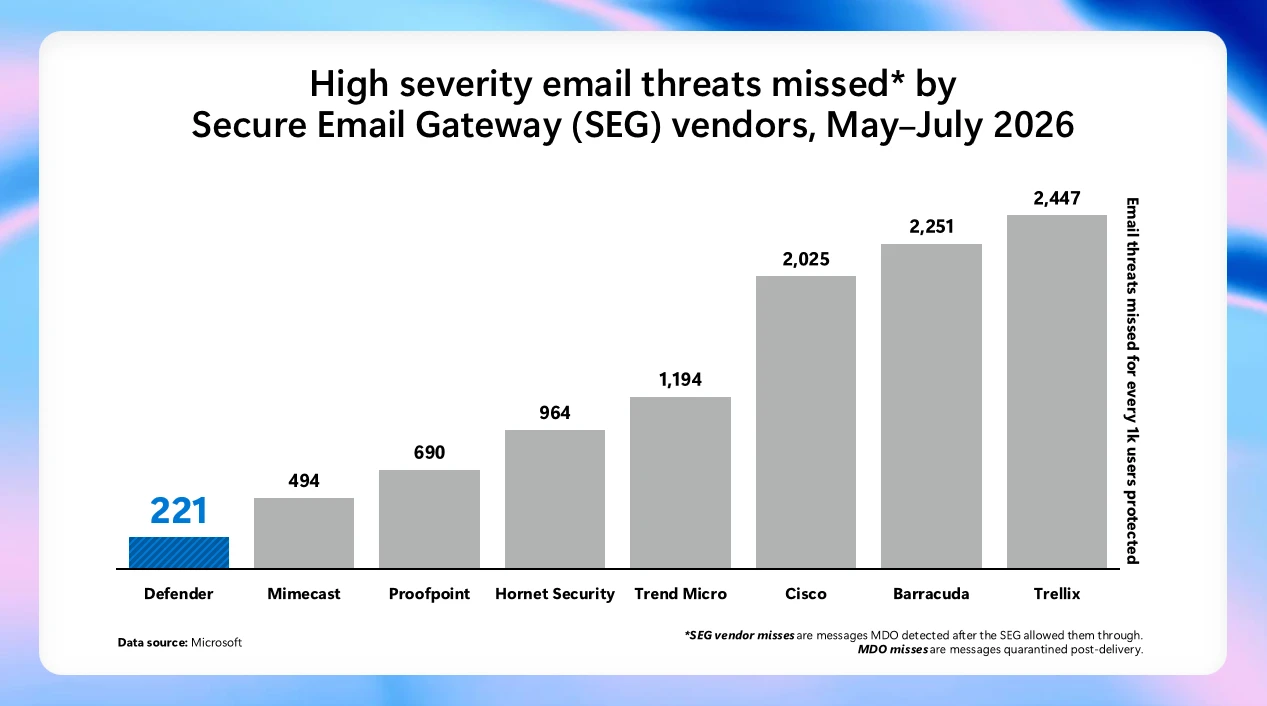
The latest email security benchmarking reports show strong Microsoft Defender performance across pre-delivery and post-delivery scenarios and reveal where threa
The defining development of the period came not from attackers but from the AI labs themselves, whose models broke out of controlled evaluations and reached rea
Revolut customers received phishing texts only days after the digital bank acknowledged disclosing customer data to a government impostor.
In this blog we explore the recently published Forrester Wave™: External Threat Intelligence Service Providers, Q3 2026 report which named Flashpoint a Customer
The CyberHawk platform goes far beyond news. Scan indicators, track active campaigns, monitor infostealer feeds, and access a complete analyst toolkit — all free to join.