Ransomware doesn’t need AI when simple weaknesses leave the door standing ajar
After reading recent reports of AI’s impact on cybercrime, one might assume that the world is about to enter an era of frightening, AI-powered ransomware attack
Ransomware campaigns, trojan analysis, botnet takedowns, infostealer tracking, and malware IOC reports from cybersecurity researchers worldwide.
After reading recent reports of AI’s impact on cybercrime, one might assume that the world is about to enter an era of frightening, AI-powered ransomware attack
Between October and November 2025, one of the biggest cybercrime operations in Interpol history saw the arrest of 574 people suspected of business email comprom
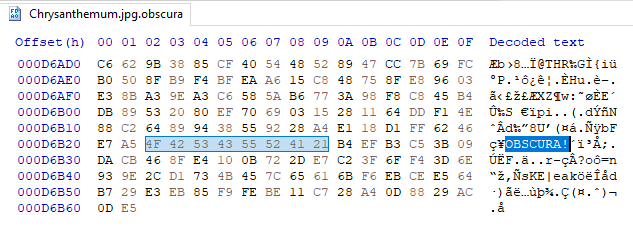
Discover how Obscura ransomware corrupts encrypted files beyond recovery, and why technical validation is key to smart ransom response decisions
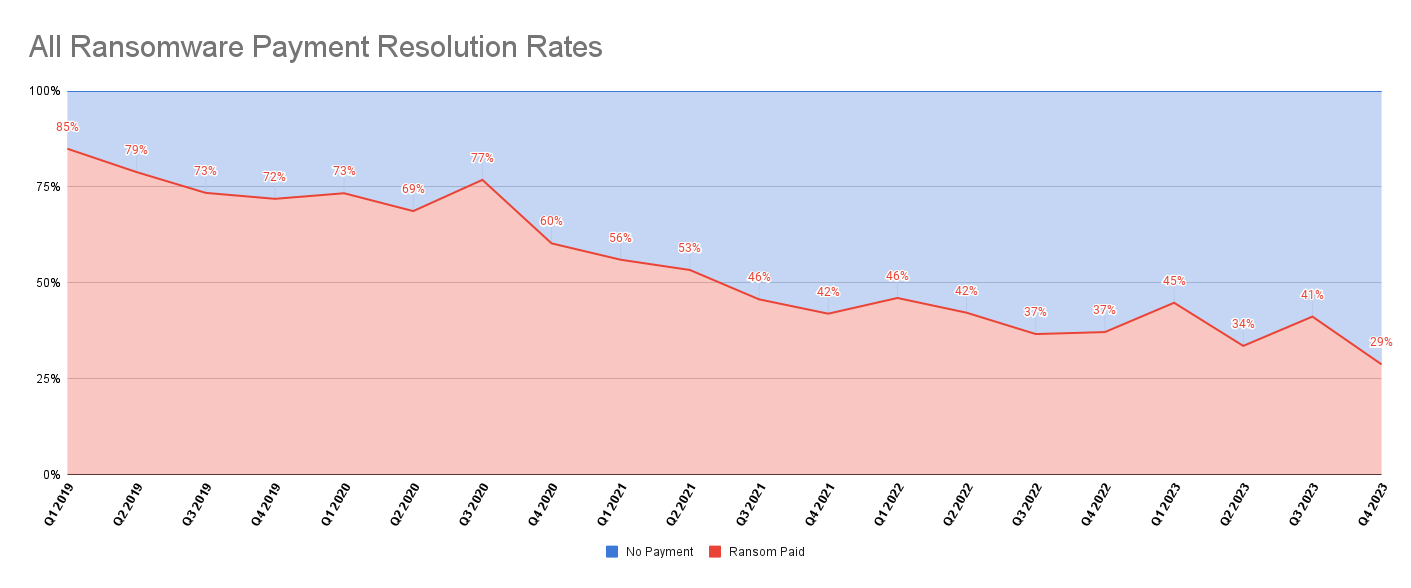
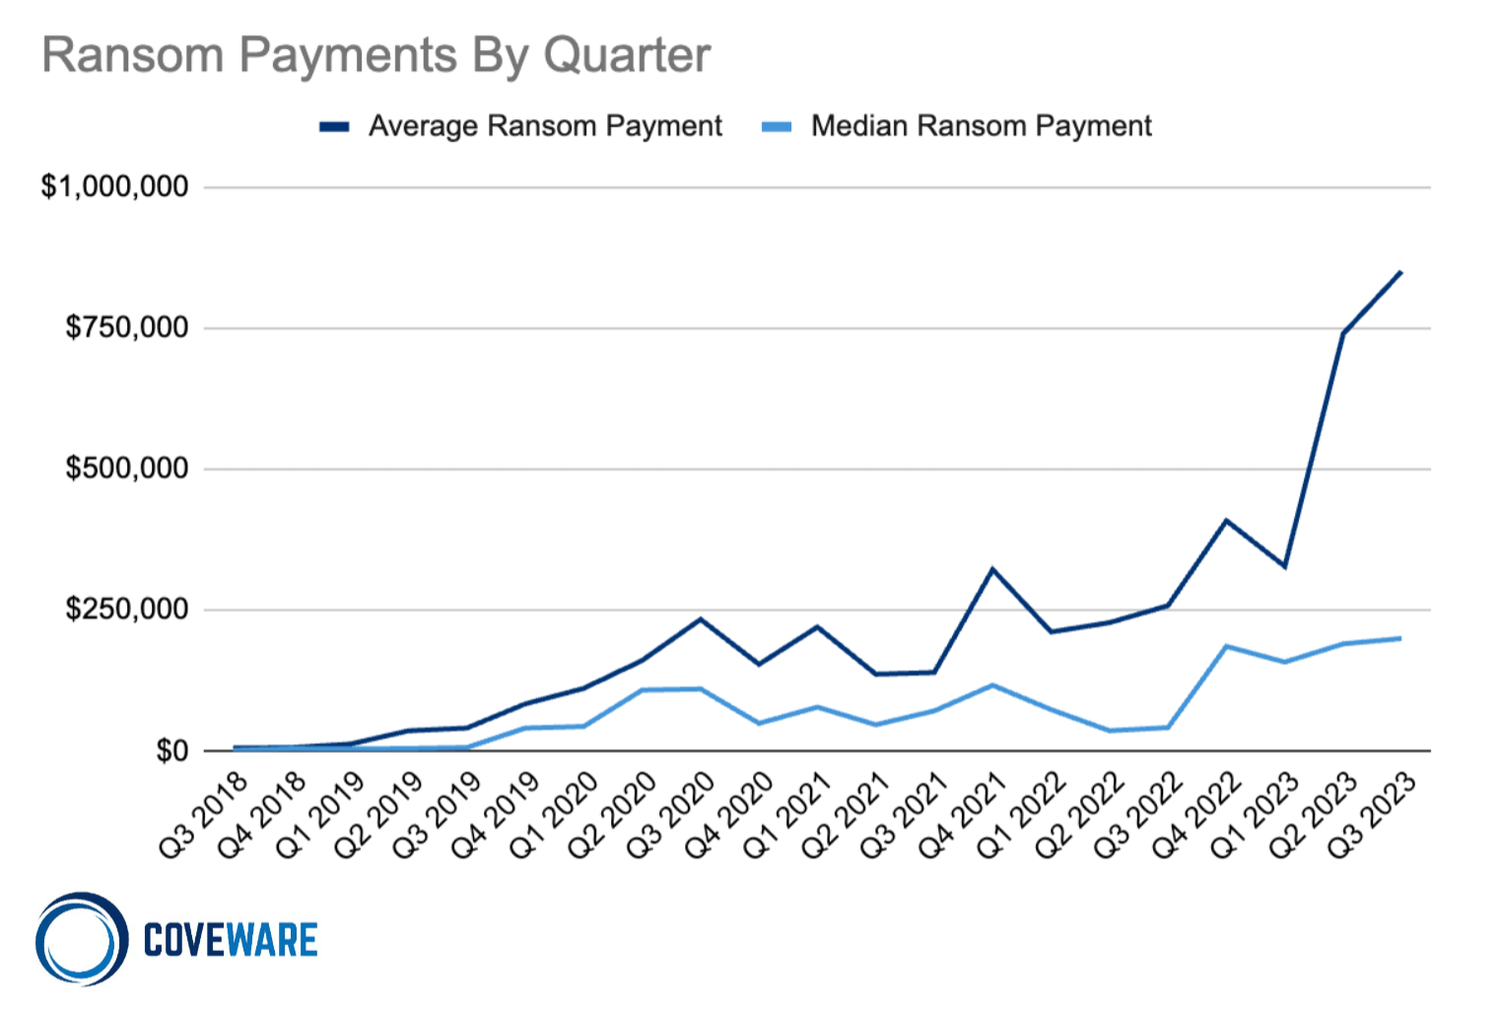
The percentage of companies choosing to pay ransoms dropped significantly, while threat actors shift their tactics in response to decreasing profits.
There’s no escaping AI’s tightening grip on the technology industry, and it turns out that ransomware criminals are just as susceptible to the reality-bending e
It’s nearly 20 years since I first encountered ransomware as the security editor of an online computer magazine, although at the time I had no idea what it was
More than three-in-ten ransomware victims are being hit multiple times, thanks to ineffective defenses and security fragmentation. According to Barracuda Networ
The Interlock ransomware gang is aggressively targeting businesses and critical infrastructure in North America and Europe, according to a new warning from the
Several ransomware groups used highly targeted social engineering tactics to create a major impact across several industry sectors in Q2 2025.
Nearly half of companies paid a ransom to get their data back last year, according to new research, but they’re taking a hard line with hackers to strike fair d
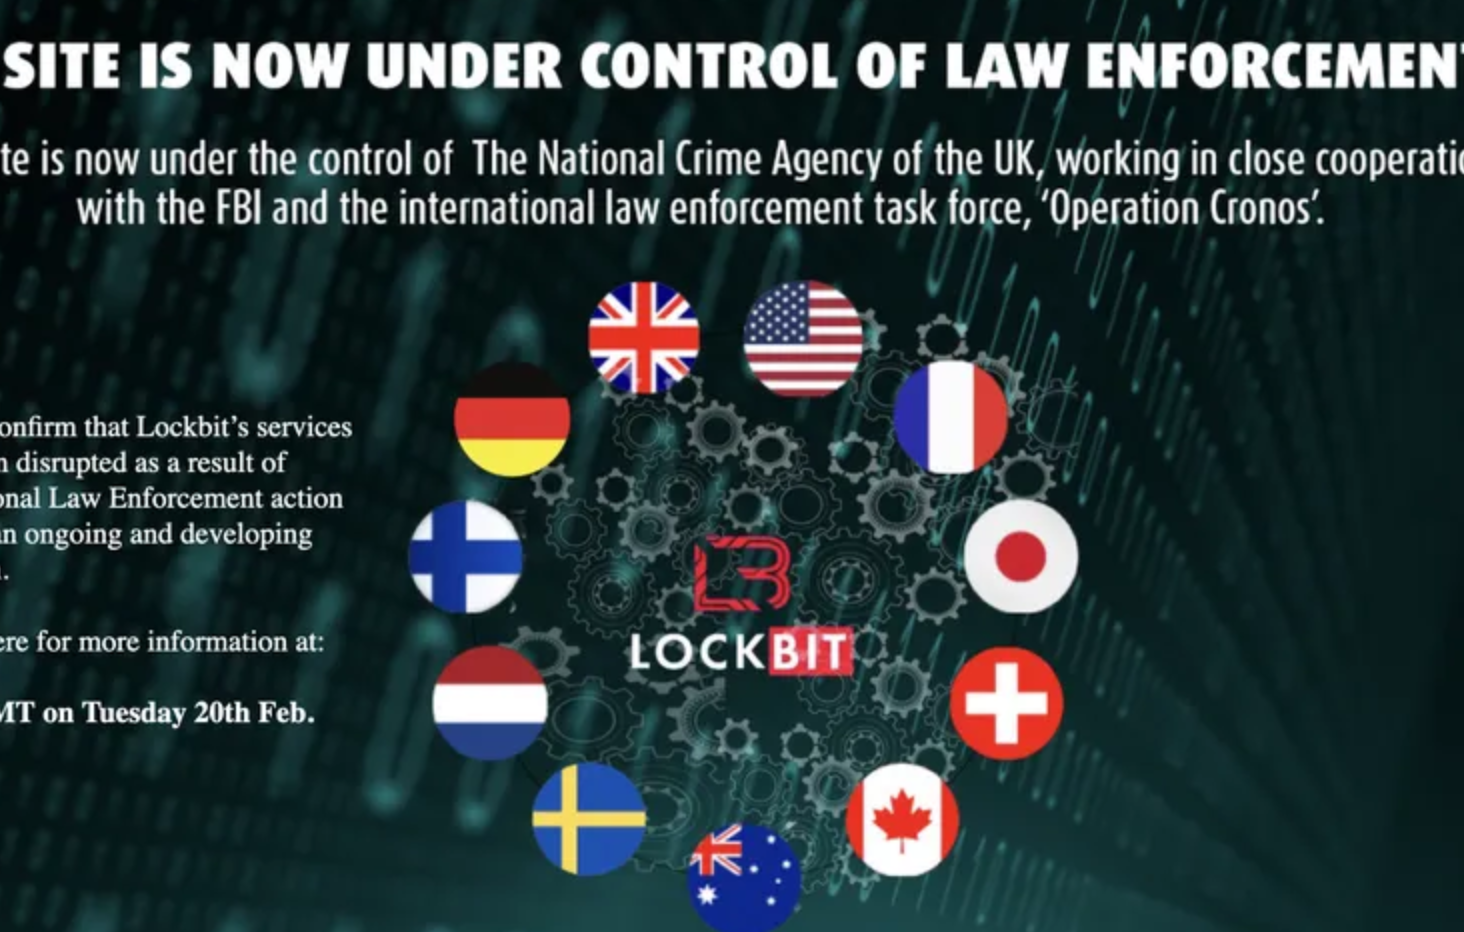
Hundreds of servers have been taken down as part of an international law enforcement operation against ransomware groups. Coordinated by Europol and Eurojust, t
The Ransomware-as-a-service (RaaS) model has not recovered from law enforcement disruption, and the entrance of novice actors along with non-Russian state-linke
2024 was a banner year for Law enforcement agency actions against ransomware and cybercrime groups. Will the new administration ensure this momentum continues?
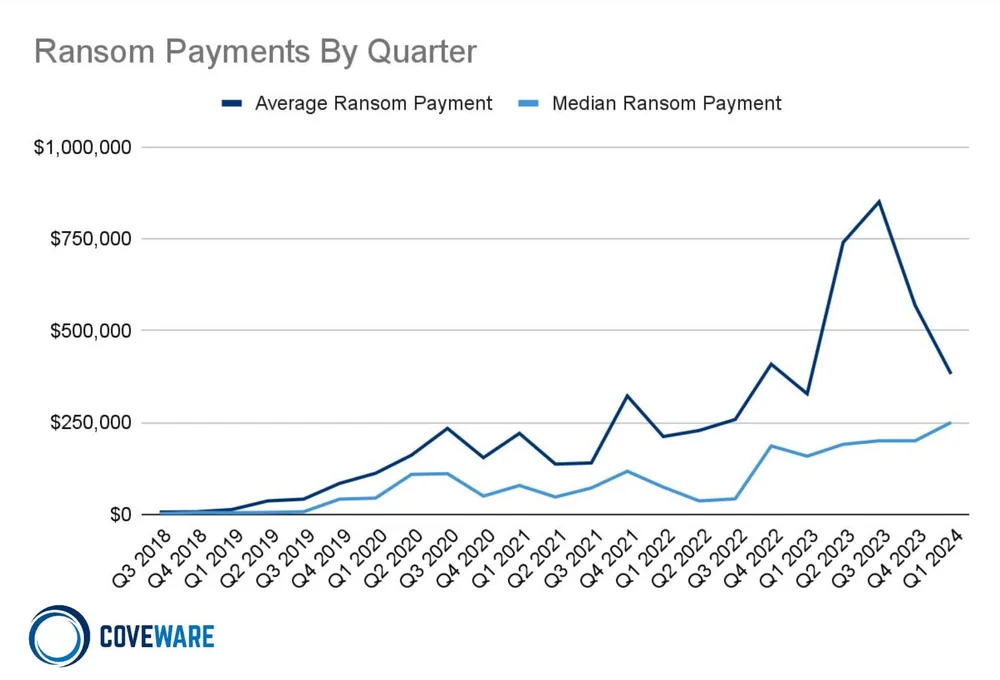
A recent Australian Financial Review (AFR) article contained statistics about ransomware payment trends that require some deeper inspection.
In Q3 2024 Law enforcement actions disrupted infrastructure and publicized the identity of several prolific ransomware threat actors
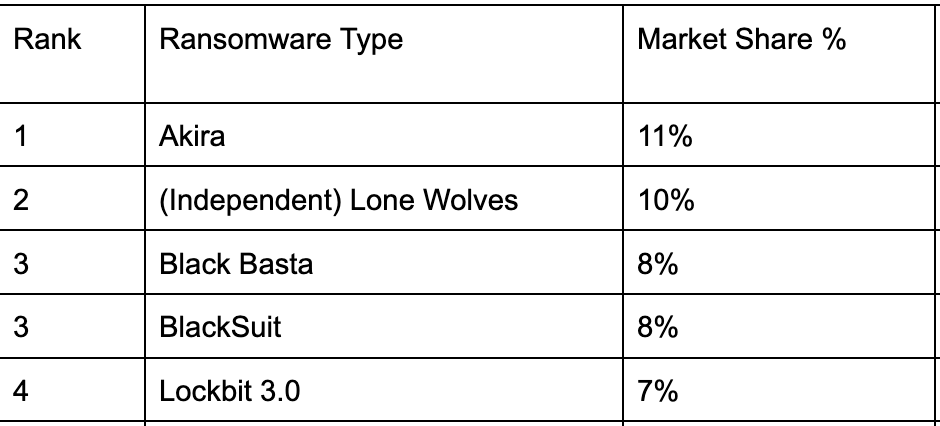
Unaffiliated ‘lone wolf’ threat actors carry out a greater share of attacks as they attempt to obfuscate their identity in Q2 2024.
RaaS developers were caught cheating their affiliates, shaking the trust in the RaaS model following several high profile law enforcement actions.
A lower percentage of ransomware victims are paying, as new regulations begin to elicit more and more public disclosure of ransomware incidents.
In Q3 2023 a series of ransomware attacks by similar threat actors created headlines and blurred the lines of attribution.
Prior botnet takedowns like Emotet and TrickBot have shown that sophisticated malware operations, like Qakbot, can often rebuild infrastructure and return from
The CyberHawk platform goes far beyond news. Scan indicators, track active campaigns, monitor infostealer feeds, and access a complete analyst toolkit — all free to join.